 InfoSecBulletin Cybersecurity for mankind
Hackers used Check Point firewall flaws to get root access, insert backdoors, and install harmful malware on a VMware ESXi host. The campaign started on October 30, 2026, by focusing on Israeli groups and later spreading globally. Check Point said that attackers used the privilege escalation issue on about twenty customers.
The investigation talks about two attacks. The first one had harmful actions against some Israeli targets. The second wave on November 2 affected groups in many countries and areas, but there was no proof of data being destroyed. Both waves did not focus on any specific industry.
PHP2Shell attack exploited a Check Point 0-day to deploy malware

North Korean hackers steal more than $400 million using video images, FBI says

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

89 New ransomware groups emerge in 2026, claiming over 2,200 victims

Daily Cyber security update for 08.11. 2026

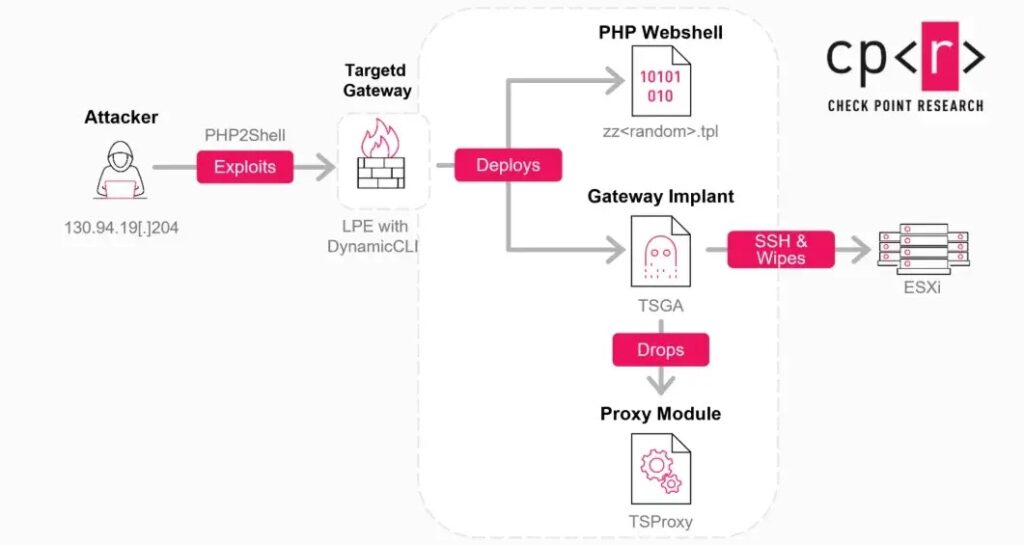
Attackers got in through weak Check Point Mobile Access portals. They used PHP2Shell attacks tied to CVE-2026-109618 and CVE-2026-109619. After accessing the portal service account, they took advantage of CVE-2026-123039 to run commands as root.
The flaw, rated 7.8, harms the Gaia operating system’s DynamicCLI service. Its dynamic_server process runs as root and takes commands through /tmp/dynamic_socket. Weak systems let any local user write to this socket. Also, the service doesn’t check who sent a command.
An attacker who can run code on a local system can send a request that has full system permissions. This is not just a simple remote access problem. The Check Point guide states that you need to have access first. Other reports on Check Point VPN issues talk about different problems, not the entry points for this campaign.
The attackers got root access and put PHP webshells in the portal’s template folder. The webshell could run system commands, execute PHP, and upload files using a fixed key.
They then installed TSGA, a persistent Linux backdoor that ran as slot_CPconfigdaemon. Its embedded TSProxy component was written to /lib/libcpfwcommon.so and loaded into appliance processes. This allowed hidden attacker connections to pass through existing services while normal traffic continued.
Hackers Exploit Check Point Firewall Flaws
The attackers used the Gogo scanner to look for internal systems. Then, they logged into an ESXi host with SSH using the vpxuser account. They ran the destroy_v6 wiper, which goes through target folders, usually replaces files with zeros, and deletes them. Its fast mode does not replace them.
The malware also left notes called DREAM_ANNEXATION.txt that said no to ransom talks. Other reports on GhostFrame attacks against VMware ESXi show another risk to virtual hosts.
Checkpoint Research found that TSGA and TSProxy share code, settings, and cryptographic material with PhiliKit, previously linked to China-associated UNC5221, but found no evidence connecting the toolkit to this incident or confirming who controlled the operation, leaving tool reuse, access brokering, and false flags as possible explanations.
Check Point shows which releases are affected from R81 to R82.20. This includes management, logging, and Maestro products. Spark Firewalls and Smart-1 Cloud are not affected. The fixed Jumbo Hotfix releases start at R82.20 Take 14, R82.10 Take 52, R82 Take 132, and R81.20 Take 174.
Administrators need to check /var/log/dynamicCli.log for commands that are not in the usual Clish wrapper and match what they find with portal and login records. Patched sockets should have permissions 0660 and be owned by root config, not 0777. Stopping dynamic_server for a while blocks this route but disables Dynamic CLI commands. Rejected connection logs show blocked attempts but do not prove that past issues were stopped.



