Saturday , November 14 2026

Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

The Latvian part of CSCTelecom,  a telecommunications provider, made a database with over 125 million SMS messages public. The leaked records are from October 2022 to September 2026 and were updated instantly. This means attackers could have grabbed codes to log in, links to reset passwords, and private details before the users saw them.

CSCTelecom acknowledged that a “security vulnerability” was identified in one of its systems, which is now fixed.

Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

The Latvian part of CSCTelecom,  a telecommunications provider, made a database with over 125 million SMS messages public. The leaked...
Read More
Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

PHP2Shell attack exploited a Check Point 0-day to deploy malware

Hackers used Check Point firewall flaws to get root access, insert backdoors, and install harmful malware on a VMware ESXi...
Read More
PHP2Shell attack exploited a Check Point 0-day to deploy malware

North Korean hackers steal more than $400 million using video images, FBI says

The United States Justice Department said Thursday it had seized cloud infrastructure used by North Korean hackers in a video-call...
Read More
North Korean hackers steal more than $400 million using video images, FBI says

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Microsoft has shared its updates for November 2026. These updates fix 1,093 new flaws in Windows, Office, SQL Server, SharePoint,...
Read More
Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Barracuda has confirmed active exploitation of security flaws affecting its Email Security Gateway (ESG), warning that attackers could combine two...
Read More
Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Apple, SAP, and Ivanti have published security updates that fix several flaws with messaging, Bluetooth, enterprise servers, and endpoint management...
Read More
Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

A jailbroken AI has been attacking a European telecom company and 13 companies using its data center and cloud for...
Read More
Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

IBM patched 208 security flaws in its API Connect platform. The CVE records released out on November 7, 2026. Among...
Read More
IBM fixes 208 API Connect vulnerabilities, 47 critical

89 New ransomware groups emerge in 2026, claiming over 2,200 victims

New ransomware actions in 2026 show more variety in cybercrime, with some groups claimed over 100 victims. The ransomware attack...
Read More
89 New ransomware groups emerge in 2026, claiming over 2,200 victims

Cybernews reported the exposed CSCTelecom ClickHouse database on September 28th, 2026. At the time, the service had sent over 3 million SMS messages in September alone.

The database had messages from big banks, hospitals, popular stores, government groups, and Latvia’s emergency hotline, 112. CSCTelecom mainly works in Latvia, but the leak also impacted people and companies in Lithuania and Estonia.

After the article was published, CSCTelecom shared company’s statement which concluded that a security issue was found in one of the company’s systems.
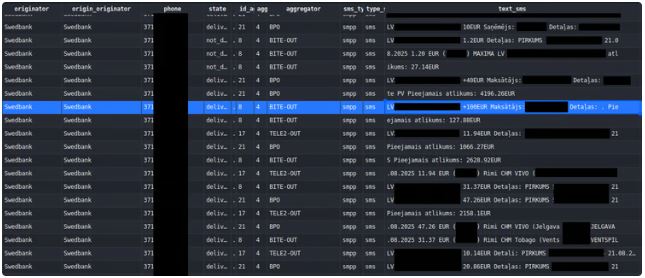
Messages associated with Swedbank exposed account IBAN numbers, transaction amounts, recipients, remaining balances (with some transactions showing the physical stores where purchases were made), and phone numbers. Image by Cybernews.

“We would like to inform you that a security vulnerability was identified in one of our information systems, and information regarding this vulnerability has also appeared in the public domain. Our specialists responded immediately by addressing the identified vulnerability and initiating an in-depth investigation into the incident,” CSCTelecom explained.

According to the company, the preliminary investigation has established that no data was downloaded from its systems. Moreover, CSCTelecom says it remediated the issue and reported it to Latvian CERT.

“In close cooperation with CERT.LV and cybersecurity experts, we are continuing a comprehensive security audit of our systems and enhanced monitoring activities. We are also implementing additional security measures to prevent similar incidents from occurring in the future,” reads the company’s statement. Click here to read the main article.


Check Also

Amadeus cyber incident impacted “Cathay Pacific, Qantas, Japan, Malaysia, Korean & Asiana” Airlines

A cybersecurity incident with Spanish travel tech company Amadeus IT Group has worried the global …