 InfoSecBulletin Cybersecurity for mankind

Zimperium’s zLabs found a new threat called SMS Stealer. It has been found in over 105,000 samples and affects more than 600 global brands. SMS Stealer poses risks like account takeovers and identity theft.
SMS stealer:
The SMS Stealer threat was discovered in 2022. It tricks victims by using fake ads and Telegram bots that pretend to be real services. By gaining access to their SMS messages, the malware then connects to one of its 13 Command and Control servers. It confirms its status and sends stolen SMS messages, including one-time passwords (OTPs).
Hackers deploy Casbaneiro Trojan that activates on bank websites

German police read Signal, Telegram, WhatsApp messages without breaking encryption

Urgent Patch! cPanel, GitLab Flaws Expose Users to RCE, File and Credential Theft

Palo Alto PAN-OS Flaw Enables Root Arbitrary Code Execution

Critical Check Point VPN flaws allow remote code execution attacks

Cisco confirms CVE-2026-20079 flaw in Secure FMC is exploited in attacks

Hackers exploit PaperCut flaws using hundreds of AI agents, compromising 440 servers globally

CISA Says Chinese Firms Extracted Billions of Tokens From Frontier AI Models

Nightmare Eclipse Drops New Microsoft Defender ‘ShieldCrash’ zero-day

cPanel Flaw Lets Hosting Accounts With Mail Privileges Execute Code as Root

OTPs add extra security to online accounts, especially for businesses that control access to sensitive data. However, the SMS Stealer can intercept OTPs, allowing attackers to take control of victims’ accounts. The associated malware stays hidden, enabling continuous attacks.
SMS Stealer impact:
Credential theft: The malware can intercept and steal login credentials.
Malware infiltration: Attackers can use stolen credentials to access systems and install more malware, making the attack more serious.
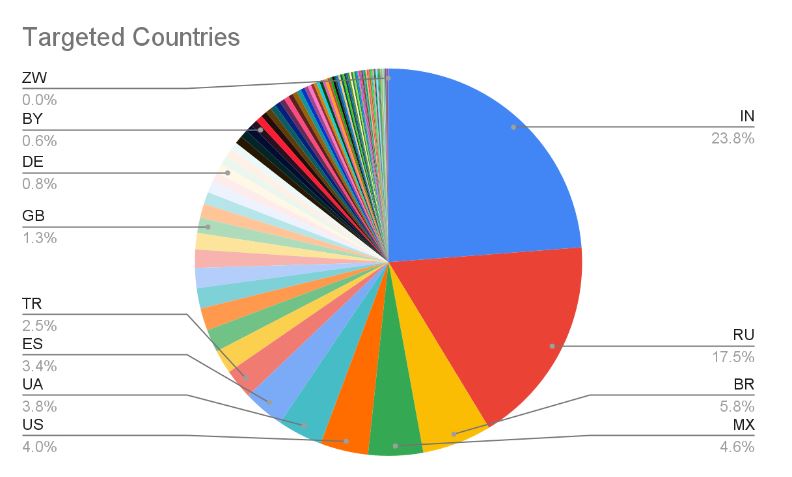
Ransomware attacks: Stolen access can be used to launch ransomware attacks, which encrypt data and demand money for recovery. Attackers can also cause financial loss by making unauthorized charges, creating fraudulent accounts, and committing theft and fraud.
“The SMS Stealer represents a significant evolution in mobile threats, highlighting the critical need for robust security measures and vigilant monitoring of application permissions,” said Nico Chiaraviglio, Chief Scientist at Zimperium. “As threat actors continue to innovate, the mobile security community must adapt and respond to these challenges to protect user identities and maintain the integrity of digital services.”



