 InfoSecBulletin Cybersecurity for mankind
Palo Alto Networks unveils a critical vulnerability in its PAN-OS firewall software that lets unauthenticated attackers remotely restart firewalls by sending specific packets. CVE-2025-4619 is a critical vulnerability that threatens organizations using Palo Alto firewalls for network security.
Daily Cyber security update for 14.11. 2026

Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

PHP2Shell attack exploited a Check Point 0-day to deploy malware

North Korean hackers steal more than $400 million using video images, FBI says

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

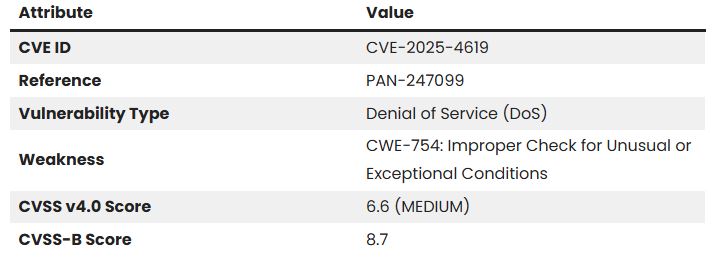
The flaw, identified as CWE-754 (Improper Check for Unusual or Exceptional Conditions), exists in the PAN-OS software dataplane. Attackers can exploit this vulnerability without needing authentication, credentials, or user interaction, causing the firewall to unexpectedly reboot.
Palo Alto Networks assigned the vulnerability a CVSS 4.0 score of 6.6, rating it as MEDIUM severity with MODERATE urgency.
However, the CVSS-B score reaches 8.7, reflecting the potential business impact. The attack vector is network-based and low-complexity.
The vulnerability impacts PA-Series firewalls, VM-Series firewalls, and Prisma Access deployments using outdated PAN-OS versions. Cloud NGFW is not impacted.
Vulnerable versions include PAN-OS 10.2 (through 10.2.13), 11.1 (through 11.1.6), and 11.2 (through 11.2.4). PAN-OS 12.1 and 10.1 are unaffected.
Palo Alto Networks recommends upgrading to patched versions. For PAN-OS 11.2. Organizations should update to 11.2.5 or later.
Upgrade to PAN-OS 11.1.7 for version 11.1. Users on 10.2 should update to 10.2.14 or follow their version’s urgency guidelines. The company has stated there are no known workarounds.
Palo Alto Networks hasn’t found any active exploitation of this vulnerability yet. Administrators should prioritize patching due to the ease of exploitation and potential impact.



