 InfoSecBulletin Cybersecurity for mankind
Safety Detectives’ Cybersecurity Team found a forum post where a threat actor shared a .CSV file with over 200 million records from X users.
The team discovered data in a forum post on the surface web. This popular forum features message boards for database downloads, leaks, cracks, and similar topics.
US banks faced unauthorized access by AI agents in customer accounts: Axios reports

Atlassian patched 176 flaw in Jira and Confluence: Fortinet Urges to Patch Flaws Affecting FortiOS, FortiManager

Hacker claim to access Rajasthan Police data: 70,000 records allegedly exposed

Update now! PHP2Shell: Critical PHP vulnerabilities patched

Trump says data centres should pay dividends to local community

Hackers Actively Exploiting Palo Alto VPN Flaw Via CVE-2026-0257

DeepSeek AI banned by U.S. Government; federal agencies must remove all related tools

CISA, NSA and NIST Publish New 10 AI Agent Control Guidelines

Claude AI Cracks 25-Year NSA Cryptography Number Mystery in Just 30 Minutes

Bypassing firewalls, AI Agents Accessed Indian ‘ Data Without Permission: CERT-In

What Was Leaked?
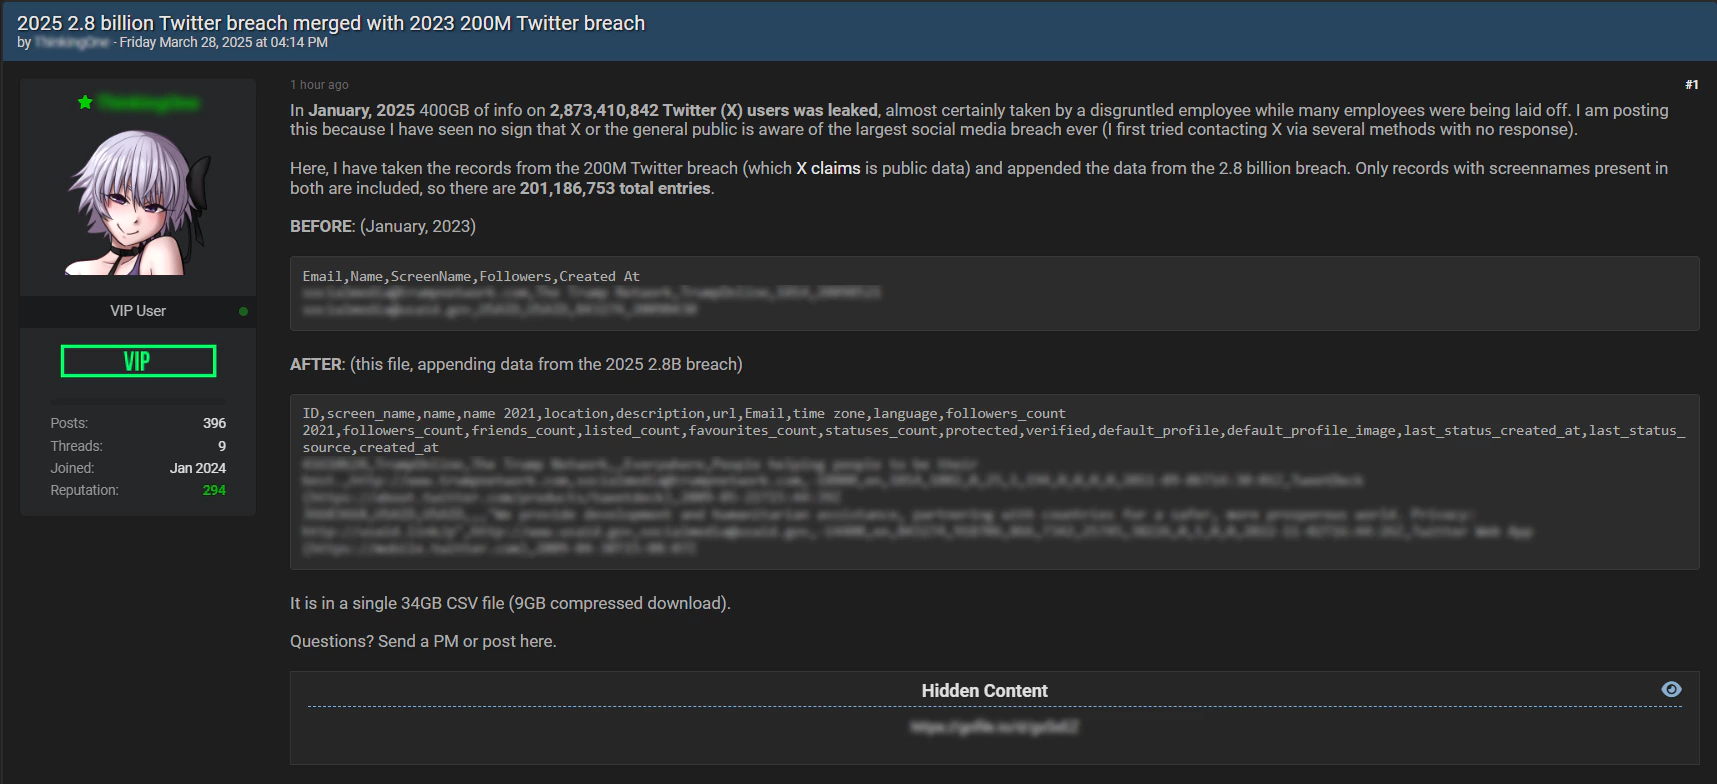
In January 2025, 400 GB of data from over 2.8 billion X users was leaked. The author of the post states they shared the data because they saw “no sign that X or the public knew about the largest social media breach ever” and that they attempted to contact X multiple times without any response.
The author didn’t publish all the data but claims to have combined data leaked in January 2023, which was publicly available, with records from a 2.8 billion breach. Only entries with screennames present in both datasets were included, totaling 201,186,753 records.
The author supposedly combined the 2025 leak data with the 2023 leak, adding emails and statistics. This resulted in a 34 GB .CSV file with 201,186,753 entries of data that allegedly belongs to X’s users.
The headers on the .CSV file are the following:
ID, screen_name, name, location, description, url, Email, time zone, language, followers, friends, lists, favorites, statuses, protected, verified, default profile, default image, last status time, last status source, created date.
Safety Detectives’ Cybersecurity Team said they reviewed a sample of the data to assess its authenticity and found the information corresponding to 100 users in the list, which matched what was shown on Twitter. The team reported that they also verified a considerable amount of emails, which turned out to be valid email addresses, though we cannot confirm that the emails belong to the accounts listed.
The file has 1,048,576 rows, each containing multiple data points about one user. It was free to download for anyone with a forum account.
Risks matter:
The leaked data poses a security and privacy risk to affected users, making them vulnerable to:
Phishing attacks: Cybercriminals could use the leaked information to create convincing emails or messages that trick users into revealing sensitive information or clicking on malicious links.
Targeted scams: Scammers may personalize their fraudulent schemes based on the individual’s activity on X, making their attempts more believable.
Social engineering attacks: Cybercriminals might manipulate users into disclosing confidential information or taking actions that compromise security.
The team suggested a bunch of tips for the users to be followed to remain safe online.



