InfoSecBulletin Cybersecurity for mankind
Cybersecurity researcher Jeremiah Fowler recently revealed a sensitive data exposure involving the Australian fintech company Vroom by YouX, previously known as Drive IQ.
Fowler, in a report to Website Planet, found an unsecured Amazon S3 bucket with 27,000 records. This database contained sensitive personal information, such as driver’s licenses, medical records, employment statements, and bank details, without any password protection or encryption.
Daily Cyber security update for 14.11. 2026

Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

PHP2Shell attack exploited a Check Point 0-day to deploy malware

North Korean hackers steal more than $400 million using video images, FBI says

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

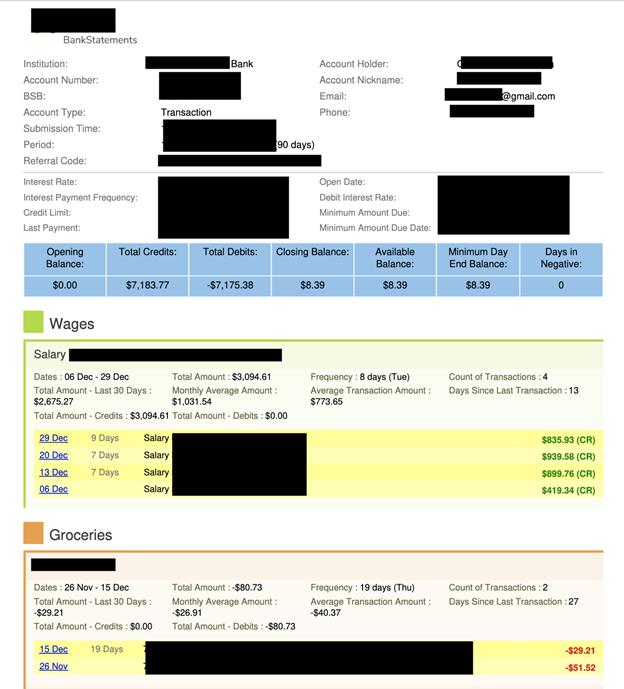
The exposed data is concerning, showing bank statements with account and partial credit card numbers. Fowler also found an internal screenshot of a separate MongoDB instance containing 3.2 million documents.
Company’s Quick Response:
Fowler quickly reported the vulnerability to Vroom, which immediately limited public access to the database. The company recognized the issue and promised a post-incident review, emphasizing its seriousness.
“We’ve identified and resolved the issue causing this vulnerability, so thank you for bringing it to our attention,” the company stated.
Vroom, which launched in 2022 as Drive IQ, is an AI-based platform that simplifies vehicle financing by connecting customers with lenders. It analyzes customer and vehicle information to deliver pre-approved financing offers. However, records from 2022 to 2025 reveal concerns about the company’s management of sensitive customer data.
The exposed information, such as identity and financial documents, poses serious fraud risks, including social engineering, fake accounts, loan applications, and impersonation, according to Fowler. Partial credit card numbers can help fill in missing details through cross-referencing or phishing scams.
He suggested that fintech companies adopt stronger security measures, including end-to-end encryption, access controls, multi-factor authentication, and regular security audits. He also supports data minimization policies, recommending that companies “collect and store active data while deleting outdated records.”
Over 200 Million Info Leaked Online Allegedly Belonging to X