 InfoSecBulletin Cybersecurity for mankind

Ransomware attacks rose 30% in October, reaching the second-highest total ever. With 623 attacks, October’s count was only behind February 2025, when a CL0P MFT campaign led to 854 attacks. This marks the sixth straight month of rising ransomware incidents, as stated in Cyble’s blog.
Qilin was the most active ransomware group for the sixth time in seven months since RansomHub’s decline, claiming 210 victims—three times more than Akira, which had the second-most at 69. Sinobi, a group that debuted in July, showed significant growth.
Daily Cyber security update for 25. 10. 2026

Daily Cyber security update for 24. 10. 2026

PHP shares new RCE flaw (CVE 2026-115560) with no patch but mitigation

US banks faced unauthorized access by AI agents in customer accounts: Axios reports

Atlassian patched 176 flaw in Jira and Confluence: Fortinet Urges to Patch Flaws Affecting FortiOS, FortiManager

Hacker claim to access Rajasthan Police data: 70,000 records allegedly exposed

Update now! PHP2Shell: Critical PHP vulnerabilities patched

Trump says data centres should pay dividends to local community

Hackers Actively Exploiting Palo Alto VPN Flaw Via CVE-2026-0257

DeepSeek AI banned by U.S. Government; federal agencies must remove all related tools


Construction, Professional Services, Healthcare, Manufacturing, IT and Energy/Utilities were the most targeted sectors.
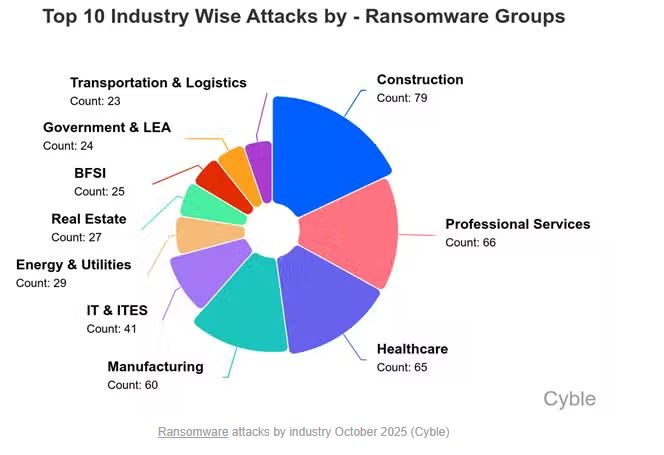
Cyble reported 31 incidents in October that could impact critical infrastructure and 26 incidents that might affect the supply chain.
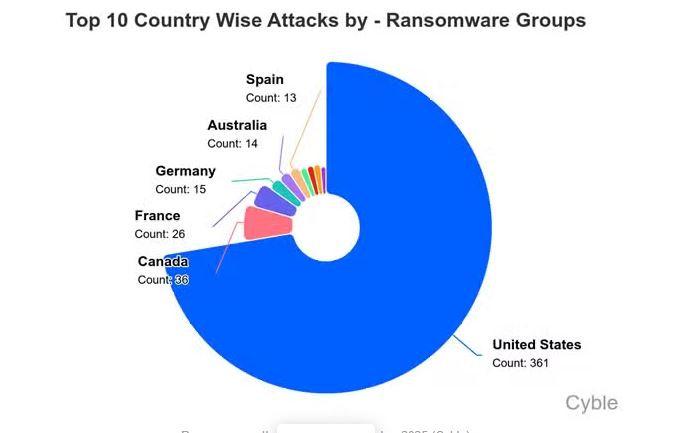
The U.S. faced the highest number of attacks, totaling 361, which is ten times more than Canada’s count.
“Of concern is the emergence of Australia as a top five target, as the country’s rich resources and high per-capita GDP have made the country a rich target for threat actors,” Cyble noted.
Ransomware attacks are up 50% so far this year, with 5,194 ransomware attacks through October 31, Cyble said, “as new leaders like Qilin, Sinobi and The Gentlemen have more than made up for the decline of former leaders such as LockBit and RansomHub.”
Vulnerabilities Exploited by Ransomware Groups:
Cyble reported that critical IT vulnerabilities and unpatched internet-facing assets have increased ransomware and supply chain attacks this year. In October, the targeted vulnerabilities included:
CVE-2025-61882 in Oracle E-Business Suite – targeted by Cl0p
CVE-2025-10035 in GoAnywhere MFT – exploited by Medusa
CVE-2021-43226 a Microsoft Windows Privilege Escalation vulnerability – Exploited by unknown ransomware groups, according to a CISA advisory
CVE-2025-6264 in Velociraptor – targeted by Warlock ransomware operators
CVE‑2024‑1086 in the Linux kernel’s netfilter :nf_tables module – Exploited by unknown ransomware groups, according to a CISA advisory



