 InfoSecBulletin Cybersecurity for mankind
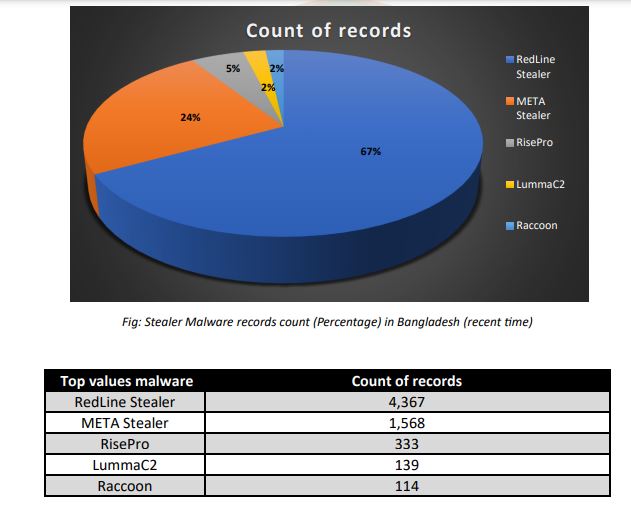
The BGD e-GOV CIRT Cyber Threat Intelligence Unit has noticed a big rise in a type of malware named stealer malware in Bangladesh’s cyberspace. These sneaky programs are good at secretly getting sensitive data like login details, personal information, and secret data from specific systems.
This breach puts financial resources at risk and compromises personal and professional secrets, creating the risk of identity theft, financial fraud, and illegal account access. The malware RedLine Stealer, META Stealer, RisePro, LummaC2, and Raccoon, found increases the risk of digital security on several platforms.
Apple Zero-Day Exploited: Pentagon Data Breach Reportedly Exposes Sensitive Data of 3 Million People

JadePuffer Agentic AI targets and destroys Azure’s cloud resources

“InfoSecCon-2026: Bangladesh’s Cybersecurity Leaders Unite to Shape a Safer Digital Future”

Microsoft Patches CVSS 10.0 Azure AI Foundry Vulnerability Allowing Privilege Escalation

AWS is unable to restore access to Bahrain, one UAE cloud data zone after war damage

Cisco Warns of Critical ISE 0-Day Flaw and Hackers Allegedly Selling Fortinet FortiGate 1-Day Flaw

Anthropic prepares “Claude Money” to analyze bank account and financial data

GhostCode Phishing Kit Evades Microsoft 365 MFA to Hijack Accounts in 78 Seconds

CISA Warns of Cisco Secure Email Gateway 0-Day Flaw Actively Exploited in Attacks

VPN flaw exposed 246,000 personnel records in japan

Recently, there has been a troubling increase in the theft of official and personal information, putting many people and organizations at risk. This has raised concerns about a higher vulnerability to ransomware attacks in Bangladesh. Efforts are being made to identify and address the main sources of these security breaches in order to improve the nation’s cybersecurity.
To read the full report click here.



