Sunday , November 15 2026
Terrapin attack

Shadowserver report
Nearly 11 million SSH servers vulnerable to Terrapin attacks

Around 11 million SSH servers are at risk from the Terrapin attack, which can compromise the security of certain SSH connections. This constitutes roughly 52% of all scanned samples in the IPv4 and IPv6 space monitored by Shadoserver.

The Terrapin attack, created by researchers from Ruhr University Bochum in Germany, affects both clients and servers using the SSH protocol.

Daily Cyber security update for 14.11. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 14.11. 2026

Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

The Latvian part of CSCTelecom,  a telecommunications provider, made a database with over 125 million SMS messages public. The leaked...
Read More
Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

PHP2Shell attack exploited a Check Point 0-day to deploy malware

Hackers used Check Point firewall flaws to get root access, insert backdoors, and install harmful malware on a VMware ESXi...
Read More
PHP2Shell attack exploited a Check Point 0-day to deploy malware

North Korean hackers steal more than $400 million using video images, FBI says

The United States Justice Department said Thursday it had seized cloud infrastructure used by North Korean hackers in a video-call...
Read More
North Korean hackers steal more than $400 million using video images, FBI says

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Microsoft has shared its updates for November 2026. These updates fix 1,093 new flaws in Windows, Office, SQL Server, SharePoint,...
Read More
Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Barracuda has confirmed active exploitation of security flaws affecting its Email Security Gateway (ESG), warning that attackers could combine two...
Read More
Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Apple, SAP, and Ivanti have published security updates that fix several flaws with messaging, Bluetooth, enterprise servers, and endpoint management...
Read More
Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

A jailbroken AI has been attacking a European telecom company and 13 companies using its data center and cloud for...
Read More
Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

IBM patched 208 security flaws in its API Connect platform. The CVE records released out on November 7, 2026. Among...
Read More
IBM fixes 208 API Connect vulnerabilities, 47 critical

SSH channel integrity can be compromised by manipulating sequence numbers during the handshake process. This is especially true when encryption modes like ChaCha20-Poly1305 or CBC with Encrypt-then-MAC are used.

An attacker can lower the security of OpenSSH 9.5 by downgrading public key algorithms and disabling defenses against timing attacks.
    Source: Bleeping computer

Terrapin attack requires attackers to be in a middle position to intercept and modify the handshake exchange. Threat actors often infiltrate important networks and wait for the right time to launch their attack.

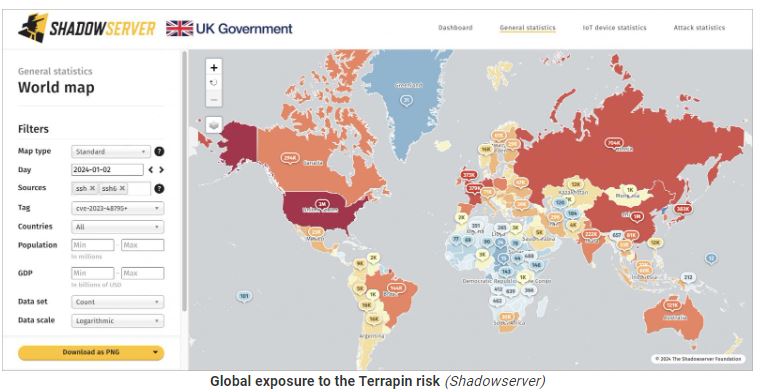
A report by Shadowserver warns that there are around 11 million SSH servers on the internet that can be targeted by Terrapin attacks.
       Source: Bleeping computer

The United States had 3.3 million vulnerable systems, followed by China with 1.3 million, Germany with 1 million, Russia with 700,000, Singapore with 390,000, and Japan with 380,000.

Shadowserver’s report is important because it shows that Terrapin attacks can affect many people.

Adversaries have a large pool of 11 million instances to choose from, even though not all of them are at immediate risk of being attacked. To check if an SSH client or server is vulnerable to Terrapin, the Ruhr University Bochum team offers a vulnerability scanner.


Check Also

€100 million

Cyber attack causes French bank Credit Mutuel Arkea €100 million missing

French lender Credit Mutuel Arkea said on Thursday hackers had stolen around €100 million ($112.61 …