InfoSecBulletin Cybersecurity for mankind
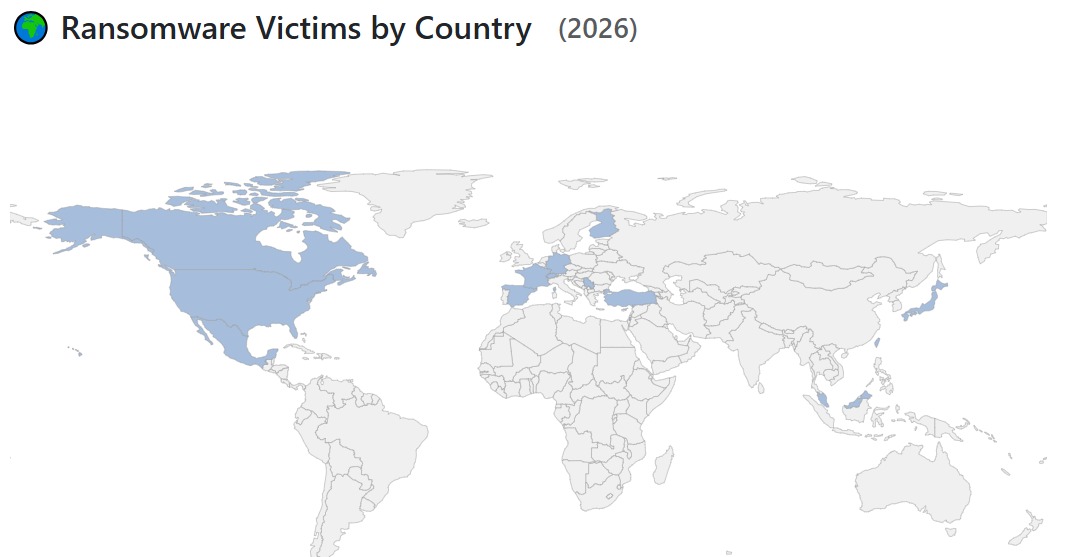
2025 ends but in the first week of 2026 a handsome figure of victims have been listed a victims of ransomware attack. Nearly about 10 groups are active for the very first week. Quin, play, direwolf, handala are some notable ones.
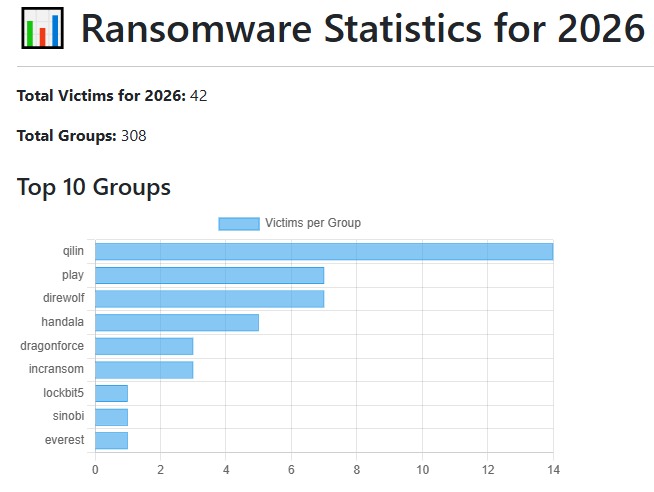
Accroding to ransomware.live as of 5 january of 2026, 42 organizations are in the queue of victims by 308 ransomware groups. Recent analysis reveals that a few threat groups account for most ransomware attacks, with Qilin being the most active and having the highest number of victims.
Daily Cyber security update for 14.11. 2026

Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

PHP2Shell attack exploited a Check Point 0-day to deploy malware

North Korean hackers steal more than $400 million using video images, FBI says

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

Qilin is the main threat actor, responsible for around 14 victims, making it the most active group during this time.
Play and Direwolf are secondary threats, each causing about 7 victims, showing less activity compared to Qilin.
Handala has moderate activity, with around 5 victims, making it a mid-tier threat.
DragonForce and Incransom show some activity, with about 3 victims each, indicating they may be engaging in opportunistic or targeted attacks.
LockBit5, Sinobi, and Everest show minimal activity around 1 victim each.