Saturday , November 14 2026
AI generated image

Hackers Claim Breach, Resecurity Says Attackers Trapped in Honeypot

“Scattered Lapsus$ Hunters” claim to have hacked cybersecurity firm Resecurity and stolen data, but Resecurity says  the hackers only accessed a decoy honeypot with fake information.
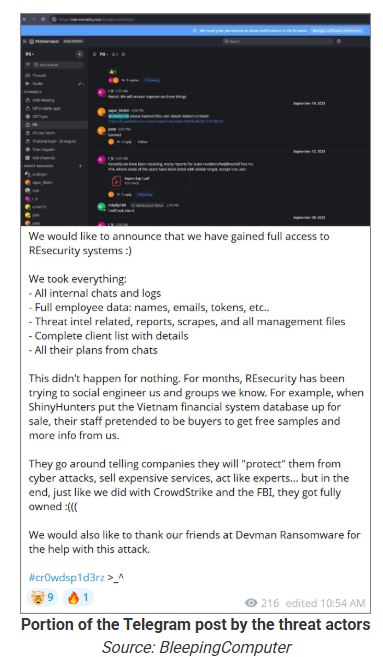
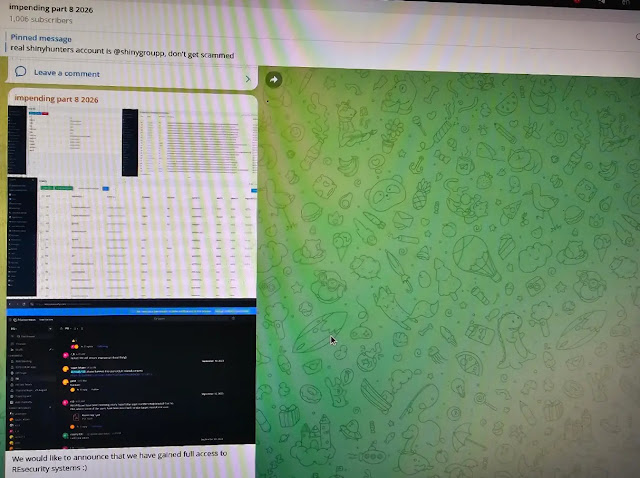
Threat actors shared screenshots on Telegram showcasing the supposed breach, asserting they had stolen employee data, internal communications, threat intelligence reports, and client information.
“We would like to announce that we have gained full access to REsecurity systems,” the group wrote on Telegram, claiming to have stolen “all internal chats and logs”, “full employee data”, “threat intel related reports”, and a “complete client list with details.”

Resecurity challenges the threat actor’s claims, asserting that the supposedly breached systems are not part of its real infrastructure but rather a honeypot intended to lure and observe the actors.

The company reported on December 24 that it first noticed a threat actor investigating its public systems on November 21, 2025.

Daily Cyber security update for 14.11. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 14.11. 2026

Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

The Latvian part of CSCTelecom,  a telecommunications provider, made a database with over 125 million SMS messages public. The leaked...
Read More
Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

PHP2Shell attack exploited a Check Point 0-day to deploy malware

Hackers used Check Point firewall flaws to get root access, insert backdoors, and install harmful malware on a VMware ESXi...
Read More
PHP2Shell attack exploited a Check Point 0-day to deploy malware

North Korean hackers steal more than $400 million using video images, FBI says

The United States Justice Department said Thursday it had seized cloud infrastructure used by North Korean hackers in a video-call...
Read More
North Korean hackers steal more than $400 million using video images, FBI says

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Microsoft has shared its updates for November 2026. These updates fix 1,093 new flaws in Windows, Office, SQL Server, SharePoint,...
Read More
Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Barracuda has confirmed active exploitation of security flaws affecting its Email Security Gateway (ESG), warning that attackers could combine two...
Read More
Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Apple, SAP, and Ivanti have published security updates that fix several flaws with messaging, Bluetooth, enterprise servers, and endpoint management...
Read More
Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

A jailbroken AI has been attacking a European telecom company and 13 companies using its data center and cloud for...
Read More
Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

IBM patched 208 security flaws in its API Connect platform. The CVE records released out on November 7, 2026. Among...
Read More
IBM fixes 208 API Connect vulnerabilities, 47 critical
Souce: Cybersecuritynews

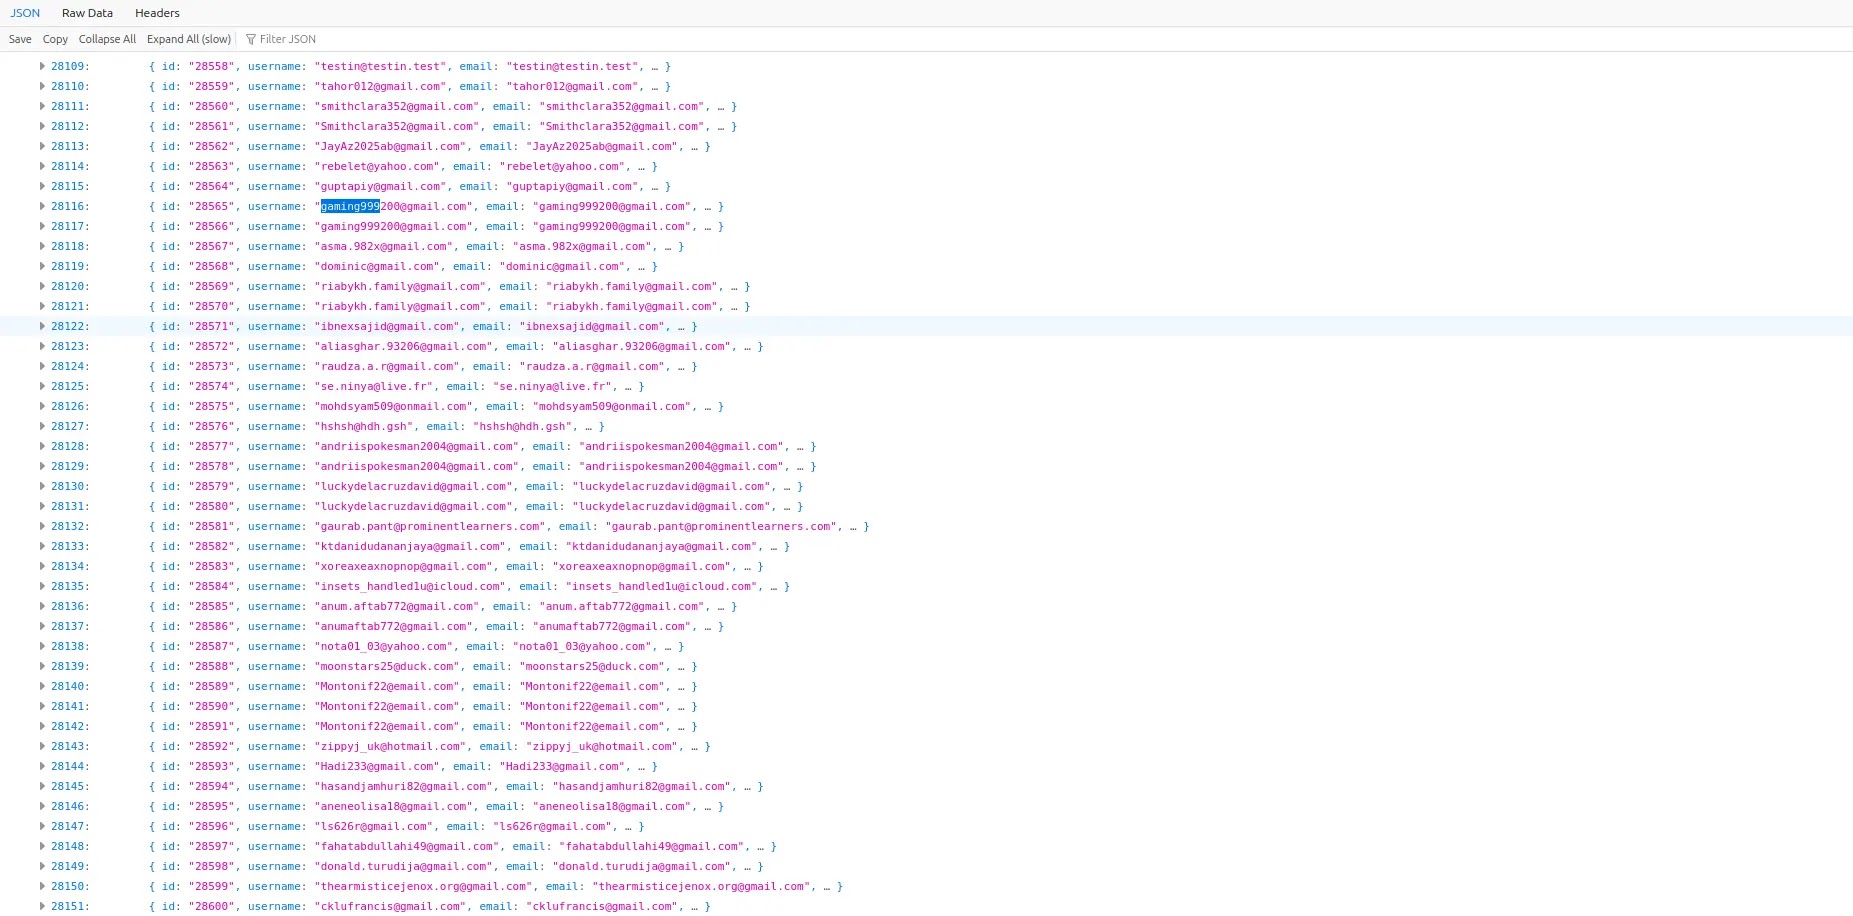
The company filled the honeypot with fake datasets that mimic real business data, including over 28,000 synthetic consumer records and more than 190,000 synthetic payment transaction records, all created using Stripe’s official API format.

Resecurity reports that a threat actor started automating data theft in December, making over 188,000 requests from December 12 to December 24 with many residential proxy IP addresses.

Update: ShinyHunters says they were not involved in this activity as reported by Bleepingcomputer.

Check Also

Cathedral

The Washington Post report
Ex-DOGE AI startup Cathedral Breaches Anthropic Internal Systems within 12 Hours

AI startup Cathedral gained a limited access to internal systems at Anthropic in less than …