 InfoSecBulletin Cybersecurity for mankind
A coordinated international law enforcement operation has dismantled Genesis Market, an illegal online marketplace that specialized in the sale of stolen credentials associated with email, bank accounts, and social media platforms.
Coinciding with the infrastructure seizure, the major crackdown, which involved authorities from 17 countries, culminated in 119 arrests and 208 property searches in 13 nations. However, the .onion mirror of the market appears to be still up and running.
Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

89 New ransomware groups emerge in 2026, claiming over 2,200 victims

Daily Cyber security update for 08.11. 2026

Japan banking crisis
Outage causes disruption at 128 japan banks: preventing ATM transaction

Daily Cyber security update for 06.11. 2026

Cyber attack causes French bank Credit Mutuel Arkea €100 million missing

The “unprecedented” law enforcement exercise has been codenamed Operation Cookie Monster.
Genesis Market, since its inception in March 2018, evolved into a major hub for criminal activities, offering access to data stolen from over 1.5 million compromised computers across the world totaling more than 80 million credentials.
A majority of infections associated with Genesis Market related malware have been detected in the U.S., Mexico, Germany, Turkey, Sweden, Italy, France, Spain, Poland, Ukraine, Saudi Arabia, India, Pakistan, and Indonesia, among others, per data gathered by Trellix.
Some of the prominent malware families that were leveraged to compromise victims encompass AZORult, Raccoon, RedLine, and DanaBot, which are all capable of stealing sensitive information from users’ systems. Also delivered through DanaBot is a rogue Chrome extension designed to siphon browser data.
“Account access credentials advertised for sale on Genesis Market included those connected to the financial sector, critical infrastructure, and federal, state, and local government agencies,” the U.S. Department of Justice (DoJ) said in a statement.
Besides credentials, Genesis also peddled device fingerprints – which include unique identifiers and browser cookies – so as to help threat actors circumvent anti-fraud detection systems used by many websites.
“The combination of stolen access credentials, fingerprints, and cookies allowed purchasers to assume the identity of the victim by tricking third party websites into thinking the Genesis Market user was the actual owner of the account,” the DoJ added.
Court documents reveal that the U.S. Federal Bureau of Investigation (FBI) gained access to Genesis Market’s backend servers twice in December 2020 and May 2022, enabling the agency to access information pertaining to about 59,000 users of the cybercrime bazaar.
The packages of stolen information harvested from infected computers (aka “bots”) were sold for anywhere between $0.70 to several hundreds of dollars depending on the nature of the data, according to Europol and Eurojust.
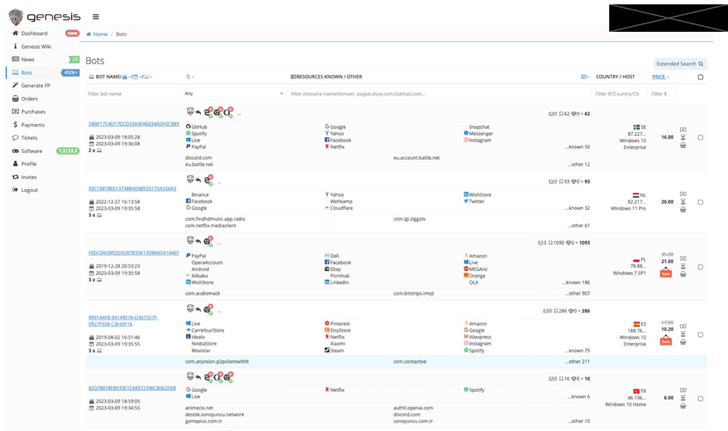
“The most expensive would contain financial information which would allow access to online banking accounts,” Europol noted, stating the criminals purchasing the data were also provided with additional tools to use it without attracting attention.
“Buyers were provided with a custom browser which would mimic the one of their victim. This allowed the criminals to access their victim’s account without triggering any of the security measures from the platform the account was on.”
The proprietary Chromium-based browser, referred to as Genesium, is cross-platform, with the maintainers claiming features such as “anonymous surfing” and other advanced functionalities that permit its users to bypass anti-fraud systems.
Genesis Market, unlike Hydra and other illicit marketplaces, was also accessible over the clearnet, thereby lowering the barrier of entry for lesser-skilled threat actors looking to obtain digital identities in order to breach individual accounts and enterprise systems.
The takedown is expected to have a “ripple effect throughout the underground economy” as threat actors search for alternatives to fill the void left by Genesis Market.
Genesis Market is the latest in a long line of illegitimate services that have been taken down by law enforcement. It also arrives exactly a year after the dismantling of Hydra, which was felled by German authorities in April 2022 and created a “seismic shift in the Russian-language darknet marketplace landscape.”
“Almost a year after Hydra’s takedown, five markets — Mega, Blacksprut, Solaris, Kraken, and OMG!OMG! Market — have emerged as the biggest players based on the volume of offers and the number of sellers,” Flashpoint said in a new report.
The development also follows the launch of a new dark web marketplace known as STYX that’s primarily geared towards financial fraud, money laundering, and identity theft. It’s said to have opened its doors around January 19, 2023.
“Some examples of the specific service offerings marketed on STYX include cash-out services, data dumps, SIM cards, DDOS, 2FA/SMS bypass, fake and stolen ID documents, banking malware, and much more,” Resecurity said in a detailed writeup.
Like Genesis Market, STYX also offers utilities that are designed to get around anti-fraud solutions and access compromised accounts by using granular digital identifiers like stolen cookie files, physical device data, and network settings to spoof legitimate customer logins.
The emergence of STYX as a new platform in the commercial cybercriminal ecosystem is yet another sign that the market for illegal services continues to be a fruitful business, allowing bad actors to profit from credential theft and payment data.
“The majority of STYX Marketplace vendors specialize in fraud and money laundering services targeting popular digital banking platforms, online-marketplaces, e-commerce and other payment applications,” Resecurity noted. “The geographies targeted by these threat actors are global, spanning the U.S., E.U., U.K., Canada, Australia and multiple countries in APAC and Middle East.”



