 InfoSecBulletin Cybersecurity for mankind
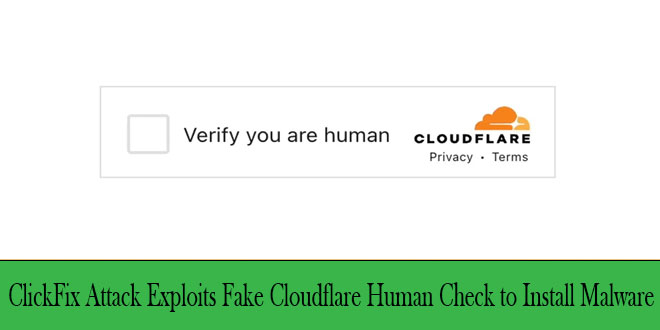
A new social engineering attack uses familiar security checks to trick users into downloading malware via fake Cloudflare verification pages.
The ClickFix attack technique marks a worrying shift in phishing methods, moving away from traditional file downloads to tricking users into running harmful commands on their own devices.
Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

89 New ransomware groups emerge in 2026, claiming over 2,200 victims

Daily Cyber security update for 08.11. 2026

Japan banking crisis
Outage causes disruption at 128 japan banks: preventing ATM transaction

Daily Cyber security update for 06.11. 2026

The attack uses a fake Cloudflare Turnstile interface that looks real, featuring official branding, genuine wording, and dynamic Ray IDs to deceive victims.
Users often encounter fake verification pages displaying familiar messages like “Checking if the site connection is secure – Verify you are human,” which resemble real Cloudflare protection. This mimicry takes advantage of verification fatigue, where users quickly click through security prompts without careful scrutiny.
SlashNext researchers have identified a new threat that uses a clever method to evade traditional security measures.
The technique is very effective because it relies on user trust in established security providers and doesn’t need complex exploits or zero-day vulnerabilities.
The attack tricks users into running harmful code by pretending to be a normal verification process.
The campaign has been seen spreading different types of malware, including information stealers like Lumma and Stealc, and remote access trojans like NetSupport Manager.
The attack succeeds by using legitimate system tools with harmful parameters, allowing it to bypass traditional security filters instead of relying on suspicious downloads.
This method bypasses many endpoint protection tools that scan downloaded files. To read the full report click here.



