 InfoSecBulletin Cybersecurity for mankind

U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added a crucial vulnerability in Fortinet FortiWeb in its Known Exploited Vulnerabilities (KEV) catalog, verifying that the SQL injection flaw is being actively exploited in cyberattacks across the globe.
The vulnerability, tracked as CVE-2025-25257, affects Fortinet’s FortiWeb web application firewall and carries a severe CVSS score of 9.6 out of 10.
PHP shares new RCE flaw (CVE 2026-115560) with no patch but mitigation

US banks faced unauthorized access by AI agents in customer accounts: Axios reports

Atlassian patched 176 flaw in Jira and Confluence: Fortinet Urges to Patch Flaws Affecting FortiOS, FortiManager

Hacker claim to access Rajasthan Police data: 70,000 records allegedly exposed

Update now! PHP2Shell: Critical PHP vulnerabilities patched

Trump says data centres should pay dividends to local community

Hackers Actively Exploiting Palo Alto VPN Flaw Via CVE-2026-0257

DeepSeek AI banned by U.S. Government; federal agencies must remove all related tools

CISA, NSA and NIST Publish New 10 AI Agent Control Guidelines

Claude AI Cracks 25-Year NSA Cryptography Number Mystery in Just 30 Minutes

The vulnerability stems from failure to properly handle special SQL elements, enabling unverified attackers to run unauthorized SQL commands through tailored HTTP or HTTPS requests.
“An improper neutralization of special elements used in an SQL command (‘SQL Injection’) vulnerability [CWE-89] in FortiWeb may allow an unauthenticated attacker to execute unauthorized SQL code or commands via crafted HTTP or HTTPs requests,” Fortinet explained in its advisory.
The vulnerability is in FortiWeb’s Fabric Connector, which connects the firewall to other Fortinet security products.
Security researchers discovered that attackers can exploit the flaw by sending malicious requests to the /api/fabric/device/status endpoint with crafted Authorization headers.
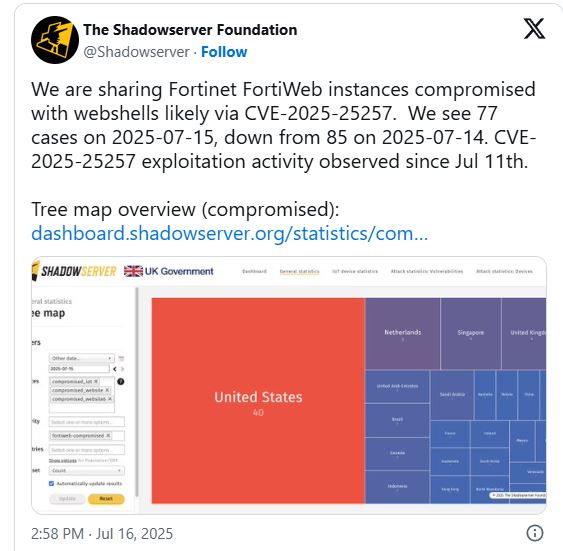
Active Exploitation Campaign:
The Shadowserver Foundation reported that 77 FortiWeb instances were compromised due to a vulnerability as of July 15, 2025, down from 85 the day before.
An exploitation campaign started on July 11, 2025, when watchTowr Labs released proof-of-concept exploit code. This shows how quickly attackers can use available exploits.
“We see 77 cases on 2025-07-15, down from 85 on 2025-07-14. CVE-2025-25257 exploitation activity observed since Jul 11th,” The Shadowserver Foundation reported.
Attacks use webshells on hacked systems, allowing attackers to maintain access. The US has the most compromised devices with 40, followed by the Netherlands, Singapore, and the UK.



