InfoSecBulletin Cybersecurity for mankind

Security researcher Jeremiah Fowler discovered an online database exposing sensitive information from an adoption agency. Jeremiah Fowler Jeremiah specializes in finding exposed cloud storage and often discovers sensitive information.
Research revealed that the database was owned by the Gladney Center for Adoption in Fort Worth, TX. After alerting the agency, the database was secured the next day. Let’s hope no one accessed it before then.
Daily Cyber security update for 14.11. 2026

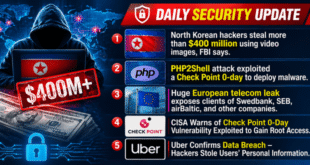
Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

PHP2Shell attack exploited a Check Point 0-day to deploy malware

North Korean hackers steal more than $400 million using video images, FBI says

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

The unencrypted database had 1,115,061 records, including names of children, birth parents, adoptive parents, and sensitive information like case notes.
Leaking adoption data poses significant risks. This sensitive information could harm children and families, as it contains personal details about children, birth parents, adoptive parents, and agency staff.
Criminals with this information could conduct targeted phishing, making their scams more convincing. In some instances, the data might be sensitive enough for extortion or identity theft.

The researcher notes:
“The records did not contain full case files, and the publicly exposed records were a combination of plain text and unique identifiers.”
He goes on to explain that unique identifiers are not necessarily a security enhancement.
“From a cybersecurity perspective, a UUID is designed for unique identification, not secrecy, and it can potentially be guessed, reverse-engineered, or enumerated. UUIDs are not recommended to be used to protect sensitive data.”
Gladney’s strong reputation encourages trust, so they should ensure their online database is securely password protected. It is unclear if Gladney exposed the database or if it was a third-party provider.
Wired posted a statement by Gladney’s Chief Operating Officer:
“The Gladney Center for Adoption takes security seriously. We always work with the assistance of external information technology experts to conduct a detailed investigation into any incident. Data integrity and operations are our top priority.”