InfoSecBulletin Cybersecurity for mankind
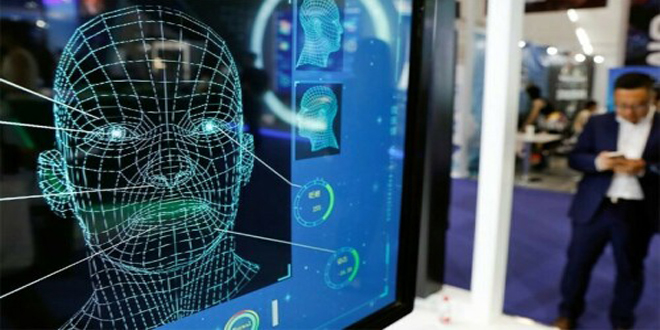
All new artificial intelligence (AI) products developed in China will be required to undergo a “security assessment” before being released to the public, a sweeping new draft law by the country’s internet regulator showed on Tuesday.
“Before providing services to the public that use generative AI products, a security assessment shall be applied for through national internet regulatory departments,” the draft law, released by the Cyberspace Administration of China, reads.
Critical cPanel, GitLab AI Gateway and Dell CSM Flaws Enable RCE And Admin Hijacking

Nearly 100,000 email addresses exposed in first AI-related data breach in Singapore

Hackers Exploit Zimbra Mail Servers: TeamViewer patched 5 critical flaws

Google Warns of Hackers Actively Exploiting Citrix 0-Day Flaws

CISA Warns Critical MikroTik RouterOS Flaw While Cisco SD-WAN Zero-Day Exploited in Attacks

Apple Zero-Day Exploited: Pentagon Data Breach Reportedly Exposes Sensitive Data of 3 Million People

JadePuffer Agentic AI targets and destroys Azure’s cloud resources

“InfoSecCon-2026: Bangladesh’s Cybersecurity Leaders Unite to Shape a Safer Digital Future”

Microsoft Patches CVSS 10.0 Azure AI Foundry Vulnerability Allowing Privilege Escalation

AWS is unable to restore access to Bahrain, one UAE cloud data zone after war damage

The draft law — dubbed “Administrative Measures for Generative Artificial Intelligence Services” — aims to ensure “the healthy development and standardised application of generative AI technology”, it read.
AI-generated content, it continued, must “reflect core socialist values, and must not contain content on subversion of state power”.
The Cyberspace Administration of China said it was seeking public input on the contents of the new regulations, which under Beijing’s highly centralised political system are almost certain to become law.
The fresh regulations come as a flurry of Chinese companies including Alibaba, JD.com, NetEase and TikTok-parent ByteDance rush to develop services that can mimic human speech since San Francisco-based OpenAI launched ChatGPT in November, sparking a gold rush in the market.
Rapid advancements in AI have stoked global alarm over the technology’s potential for disinformation and misuse, with deepfake images and people shown mouthing things they never said.
Beijing in January enforced new rules that would require businesses offering deepfake services to obtain the real identities of their users. They also require deepfake content to be appropriately tagged to avoid “any confusion”.
The Chinese government has also warned that deepfakes present a “danger to national security and social stability”.
ChatGPT is unavailable in China, but the American software is gaining a base of Chinese users who use virtual private networks to get around the ban, deploying it to write essays and cram for exams.
China has announced ambitious plans to become a global leader in the field of AI by 2030, and consultancy group McKinsey estimates the sector could add about $600 billion every year to China’s gross domestic product by then.
Domestic efforts to develop competing products have faltered, however, hamstrung by Beijing’s strict censorship and a US squeeze on chip imports.
Last month, shares in Chinese search engine company Baidu fell as much as 10 percent after the company unveiled its ChatGPT-like AI software, with investors unimpressed by the bot’s display of linguistic and maths skills.