 InfoSecBulletin Cybersecurity for mankind
The UK’s Electoral Commission was targeted by a “sophisticated cyber-attack”, which led to the personal information of many British voters being exposed.
In October 2022, the Commission made a shocking discovery – an attack had been detected on its systems after detecting suspicious activity. Attackers accessed the servers of the Commission in August 2021, according to a subsequent investigation reported in a notification on August 8, 2023.
US banks faced unauthorized access by AI agents in customer accounts: Axios reports

Atlassian patched 176 flaw in Jira and Confluence: Fortinet Urges to Patch Flaws Affecting FortiOS, FortiManager

Hacker claim to access Rajasthan Police data: 70,000 records allegedly exposed

Update now! PHP2Shell: Critical PHP vulnerabilities patched

Trump says data centres should pay dividends to local community

Hackers Actively Exploiting Palo Alto VPN Flaw Via CVE-2026-0257

DeepSeek AI banned by U.S. Government; federal agencies must remove all related tools

CISA, NSA and NIST Publish New 10 AI Agent Control Guidelines

Claude AI Cracks 25-Year NSA Cryptography Number Mystery in Just 30 Minutes

Bypassing firewalls, AI Agents Accessed Indian ‘ Data Without Permission: CERT-In

ALSO READ:
The perpetrators gained unauthorized access to the “reference copies” of the electoral registers. These copies were specifically maintained by the Commission for research purposes and to verify the acceptability of political donations. The data included personal information like names and addresses of all registered voters in the United Kingdom from 2014 to 2022. The names of those registered as overseas voters were also exposed. The register did not contain any information about those who registered anonymously.
JBlake Moore, a cybersecurity advisor at ESET, expressed concern about the 15-month-long unnoticed attack. The authorities were not informed of any irregularities in their systems during this period.
Cybercriminals are most effective when operating in stealth mode, but it is uncommon for them to remain undetected for such an extended period. He expressed sadness at witnessing malicious individuals infiltrating and searching for a prolonged period, regardless of the attack’s complexity.
Social media users have also raised questions about why it took the Commission 10 months to notify the public about the incident.
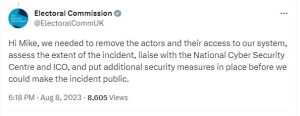
According to the Commission’s official Twitter account, they took steps to safeguard their system by removing the actors involved, evaluating the full impact of the incident, collaborating with the National Cyber Security Centre and ICO, and implementing extra security measures. These precautions were necessary before the Commission publicly disclosed the incident.
There has been no evidence of the “hostile actor” affecting the security of UK elections, including the upcoming 2024 General Election. Accessing the data does not influence individuals’ ability to register, vote, or actively engage in democratic processes. It has no impact on the management of the electoral registers or on the running of elections.”
Furthermore, the attackers were able to breach the Electoral Commission’s email system, resulting in the exposure of additional personal information belonging to voters.
The Commission said the information affected in the breach “does not pose a high risk to individuals.” However, it had a duty to provide the August 8 notification “due to the high volume of personal data potentially viewed or removed during the cyber-attack” under Articles 33 and 34 of the UK General Data Protection Regulation (GDPR).
The Commission has issued a statement expressing its sincere apology to all individuals impacted by the incident. Furthermore, the company has worked with security experts to investigate the issue and improve its system security to prevent future attacks.
The breach’s perpetrator remains unknown at this time. In recent years, there have been frequent accusations of Russia-linked actors targeting the electoral processes of nation-states.
It is not the first time voter information has been exposed. In March 2022, London voters’ personal details were accidentally leaked by their council. The leak occurred when emails were sent to the wrong recipients.



