 InfoSecBulletin Cybersecurity for mankind
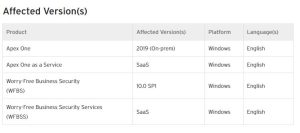
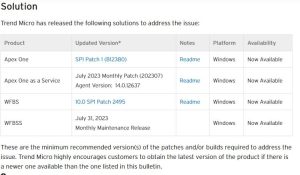
Trend Micro, a cybersecurity company, has released patches and hotfixes for Windows. These fixes address a critical security flaw in Apex One and Worry-Free Business Security solutions. The flaw has been used in real-world attacks.
ALSO READ:
CISA adds PHP2Shell to KEV, PHP Releases New Security Updates to Fix Critical HTTP2Shell flaw
By infosecbulletin
/ Tuesday , October 27 2026
CISA has updated a new alert to reflect the addition of CVE-2026-109618 and CVE-2026-109619 to its Known Exploited Vulnerabilities (KEV)...
Read More

Cloudflare Unveils Emergency WAF Ruleset Update on Brotli flaw
By infosecbulletin
/ Monday , October 26 2026
Cloudflare has shared an urgent update to its Web Application Firewall (WAF) rules due to CVE-2026-111497, a Brotli issue. The release...
Read More

Daily Cyber security update for 26.10. 2026
By infosecbulletin
/ Monday , October 26 2026
Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More

The Washington Post report
Ex-DOGE AI startup Cathedral Breaches Anthropic Internal Systems within 12 Hours
By infosecbulletin
/ Monday , October 26 2026
AI startup Cathedral gained a limited access to internal systems at Anthropic in less than 12 hours, exposing employee information,...
Read More

Daily Cyber security update for 25. 10. 2026
By infosecbulletin
/ Sunday , October 25 2026
Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More

Daily Cyber security update for 24. 10. 2026
By infosecbulletin
/ Saturday , October 24 2026
Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More

PHP shares new RCE flaw (CVE 2026-115560) with no patch but mitigation
By infosecbulletin
/ Friday , October 23 2026
The PHP security team shared ways to protect against a new flaw that lets someone run unwanted code on certain...
Read More

US banks faced unauthorized access by AI agents in customer accounts: Axios reports
By infosecbulletin
/ Friday , October 23 2026
Major US banks have detected unauthorized access to customer accounts by third-party AI agents, with some systems taking actions beyond...
Read More

Atlassian patched 176 flaw in Jira and Confluence: Fortinet Urges to Patch Flaws Affecting FortiOS, FortiManager
By infosecbulletin
/ Thursday , October 22 2026
Fortinet has urged customers to prioritize security updates for FortiOS, FortiManager, and FortiAnalyzer scheduled for October 22, 2026. The coordinated...
Read More

Hacker claim to access Rajasthan Police data: 70,000 records allegedly exposed
By infosecbulletin
/ Wednesday , October 21 2026
Hacker offers to sell Rajasthan Government’s Department of Information Technology & Communication (DoIT&C) data in a underground forum. The threat...
Read More

10 banks may face penalties for Dollar exchange rate manipulation
The issue, classified as CVE-2023-41179 with a CVSS score of 9.1, pertains to a module responsible for uninstalling third-party antivirus software that comes bundled with the program.
To read full release of trend micro click here



