InfoSecBulletin Cybersecurity for mankind

Trend Micro warned customers to quickly secure their systems due to a remote code execution vulnerability in its Apex One endpoint security platform that is currently being exploited.
Apex One is an endpoint security platform designed to automatically detect and respond to threats, including malicious tools, malware, and vulnerabilities.
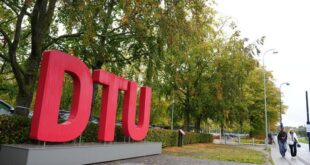
Major Danish university breached, 200,000 users at risk

Microsoft’s X account hijacked to promote Clippy crypto scam

Critical cPanel, GitLab AI Gateway and Dell CSM Flaws Enable RCE And Admin Hijacking

Nearly 100,000 email addresses exposed in first AI-related data breach in Singapore

Hackers Exploit Zimbra Mail Servers: TeamViewer patched 5 critical flaws

Google Warns of Hackers Actively Exploiting Citrix 0-Day Flaws

CISA Warns Critical MikroTik RouterOS Flaw While Cisco SD-WAN Zero-Day Exploited in Attacks

Apple Zero-Day Exploited: Pentagon Data Breach Reportedly Exposes Sensitive Data of 3 Million People

JadePuffer Agentic AI targets and destroys Azure’s cloud resources

“InfoSecCon-2026: Bangladesh’s Cybersecurity Leaders Unite to Shape a Safer Digital Future”

The flaw tracked as CVE-2025-54948 and CVE-2025-54987 depending on the CPU, allows attackers to remotely run arbitrary code on unpatched Apex One Management Console systems due to a command injection vulnerability.
Trend Micro hasn’t released security updates for this actively exploited vulnerability yet, but it has provided a mitigation tool for temporary protection.
The Japanese CERT also issued an alert regarding the active exploitation of the two flaws, urging users to mitigate them as soon as possible.
“While it will fully protect against known exploits, it will disable the ability for administrators to utilize the Remote Install Agent function to deploy agents from the Trend Micro Apex One Management Console,” the company explained in a Tuesday advisory.
“Trend Micro has observed as least one instance of an attempt to actively exploit one of these vulnerabilities in the wild.”
The company announced a patch will be available by mid-August 2025, which will also reinstate the Remote Install Agent feature disabled by the mitigation tool.
Trend Micro advised administrators to secure vulnerable endpoints immediately, even if it means sacrificing remote management, until a security patch is released.
“For this particular vulnerability, an attacker must have access to the Trend Micro Apex One Management Console, so customers that have their console’s IP address exposed externally should consider mitigating factors such as source restrictions if not already applied,” it added.
“However, even though an exploit may require several specific conditions to be met, Trend Micro strongly encourages customers to update to the latest builds as soon as possible.”
Trend Micro fixed two other vulnerabilities in Apex One, one of which was used in attacks in September 2022 (CVE-2022-40139) and another in September 2023 (CVE-2023-41179).
Bangladeshi gov.t/law enforcement email accounts compromised