 InfoSecBulletin Cybersecurity for mankind
ShinyHunters claim to compromise over 3 million Salesforce records with personal data, GitHub files, AWS storage, and other compromised company information. On March 31st, ShinyHunters posted extortion demands targeting Cisco Systems. The hackers are threatening the company with “several annoying (digital) problems,” unless their demands are met by April 3rd.

Daily Cyber security update for 25. 10. 2026

Daily Cyber security update for 24. 10. 2026

PHP shares new RCE flaw (CVE 2026-115560) with no patch but mitigation

US banks faced unauthorized access by AI agents in customer accounts: Axios reports

Atlassian patched 176 flaw in Jira and Confluence: Fortinet Urges to Patch Flaws Affecting FortiOS, FortiManager

Hacker claim to access Rajasthan Police data: 70,000 records allegedly exposed

Update now! PHP2Shell: Critical PHP vulnerabilities patched

Trump says data centres should pay dividends to local community

Hackers Actively Exploiting Palo Alto VPN Flaw Via CVE-2026-0257

DeepSeek AI banned by U.S. Government; federal agencies must remove all related tools

“A total of over 3M Salesforce records containing PII (personally identifiable information), Github repositories, AWS buckets, and other internal corporate data have been compromised,” ShinyHunters claims on its victim page on the dark web.
According to the post, the data comes from three breaches: voice phishing (UNC6040), Salesforce Aura, and AWS accounts. The attackers included two screenshots to back up their claims.
What do the hackers claim to have stolen?
One image shows the AWS EC2 Volumes screen, with many virtual hard drives in the cloud. Many of these likely hold hundreds of gigabytes of data. The screenshot has 5 pages, which means there could be more than 100 virtual storage drives.
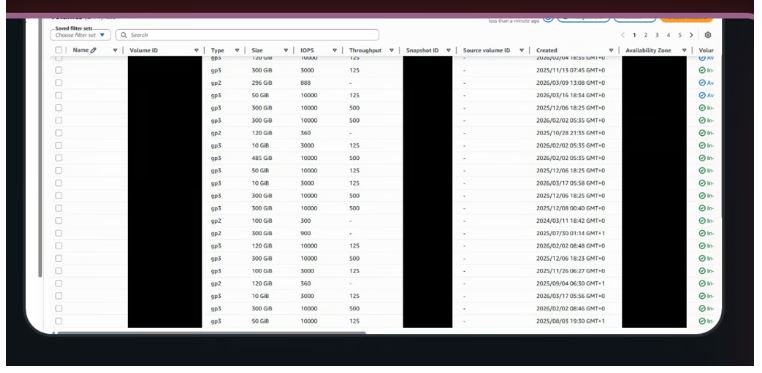
Some of the drive creation dates are specified as March 16th-17th, 2026, suggesting recent access. Another screenshot shows a list of AWS S3 buckets that are said to belong to Cisco. The names hint strongly that it is a Cisco setup, but no real data has been shared.
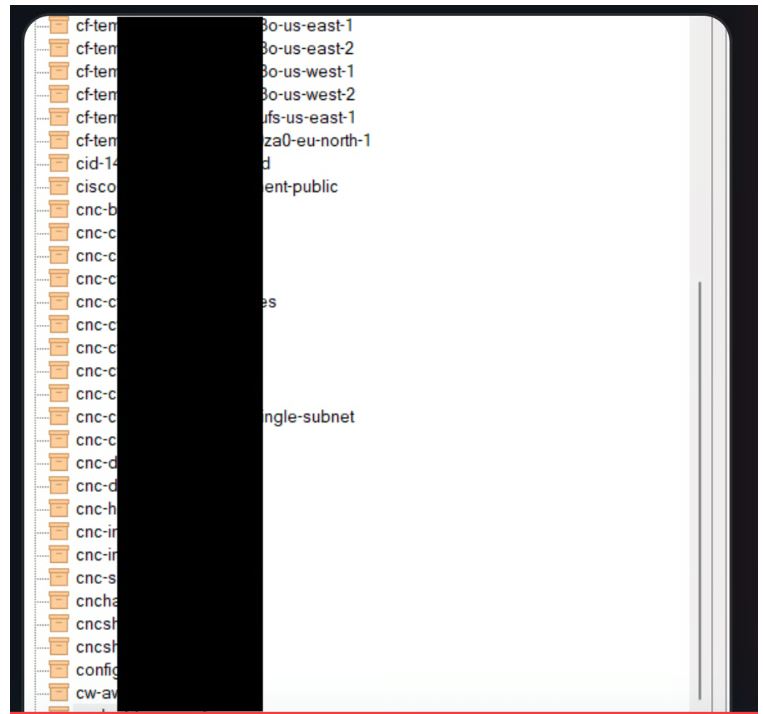
Neither the attacker claims nor the screenshots conclusively prove the breach. “A portion of the stolen repositories allegedly belongs to corporate customers, including banks, BPOs, and US government agencies,” Bleeping Computer reported.
At the same time, Bleeping Computer reported Cisco was hit by a cyberattack linked to the recent Trivy supply chain issue. The report states that hackers took several AWS keys and copied more than 300 GitHub repositories. This included the source code for an AI assistant, defense tools, and other AI products that have not been released.
“We cannot confirm the ShinyHunters’ claims as they did not upload the data yet, but looking at the sample screenshots, it seems plausible,” researchers said.
“This incident can be damaging to the company’s customers, and the main risks are confidential data exposure in general. Data from customers would give attackers a foothold to plan further attacks, and the personally identifiable information could be useful for social engineering, fraud, and other scams.”



