 InfoSecBulletin Cybersecurity for mankind
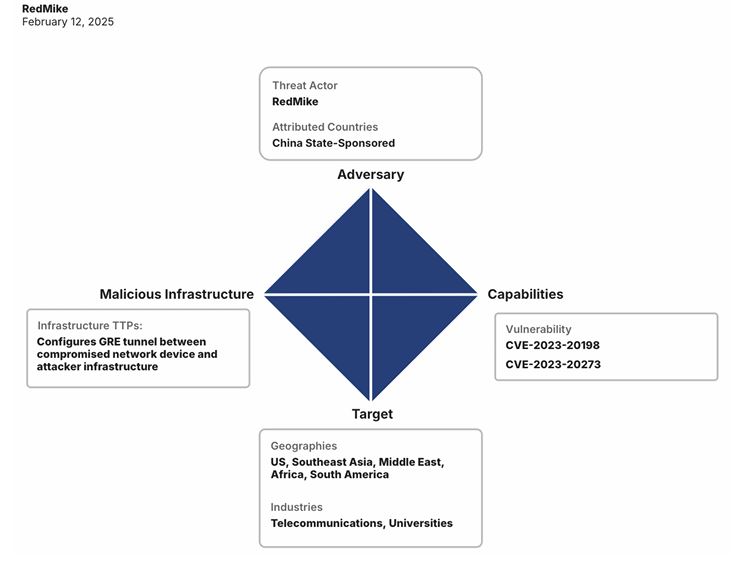
RedMike (Salt Typhoon) targeted university devices in Bangladesh, likely to access research in telecommunications, engineering, and technology, especially from institutions like UCLA and TU Delft.
Recorded Futureʼs Insikt Group identified the campaign targeted universities in various countries like Argentina, Indonesia, Malaysia, Mexico, the Netherlands, Thailand, the United States, and Vietnam.
Daily Cyber security update for 14.11. 2026

Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

PHP2Shell attack exploited a Check Point 0-day to deploy malware

North Korean hackers steal more than $400 million using video images, FBI says

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

According to the report, RedMike possibly targeted the following universities to access research in areas related to telecommunications, engineering, and technology, particularly at institutions like UCLA and TU Delft.
● Islamic University of Technology (IUT) — Bangladesh
● University of California, Los Angeles (UCLA) — US
● California State University, Office of the Chancellor (CENIC) — US
● Loyola Marymount University — US
● Utah Tech University — US
● Universidad de La Punta — Argentina
● Universitas Sebelas Maret — Indonesia
● Universitas Negeri Malang — Indonesia
● University of Malaya — Malaysia
● Universidad Nacional Autonoma — Mexico
● Technische Universiteit Delft — The Netherlands
● Sripatum University — Thailand
● University of Medicine and Pharmacy at Ho Chi Minh City — Vietnam
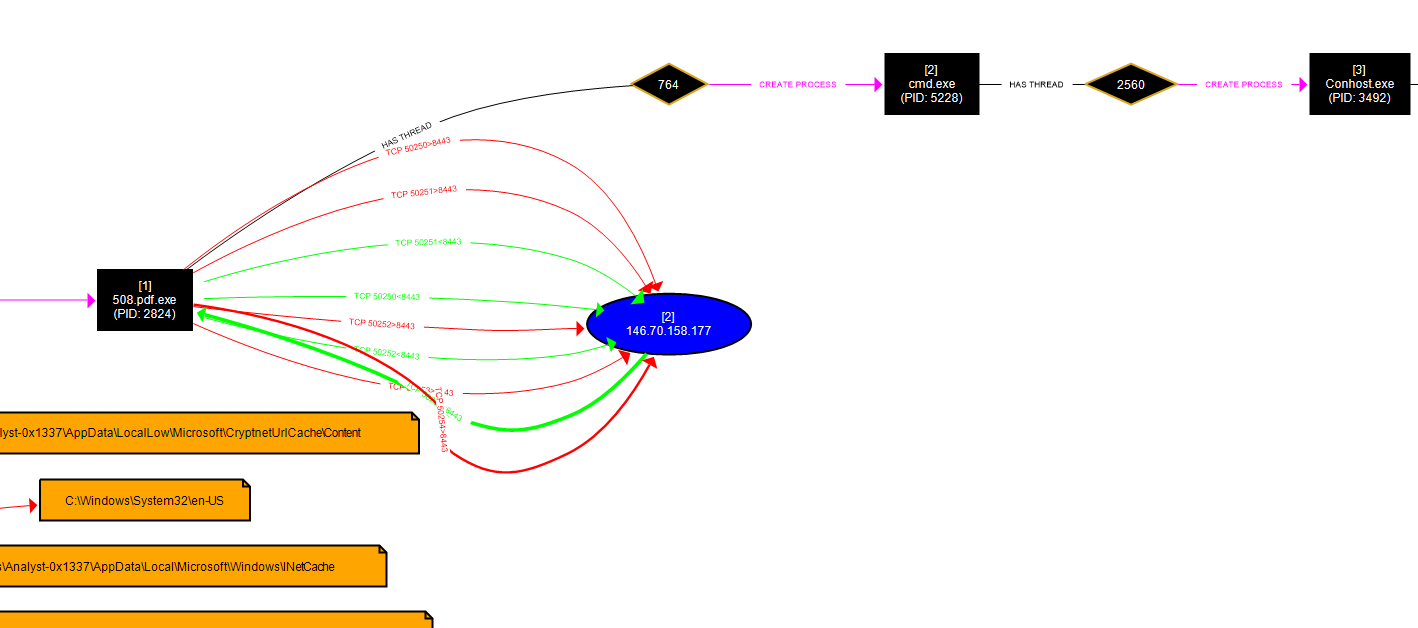
On the other hand, a sophisticated malware campaign is targeting military and government entities in Bangladesh. It uses social engineering to deliver malicious files disguised as official documents, aiming to infiltrate secure networks, steal credentials, and access sensitive systems.
Threat Intelligence Community of Bangladesh warns that a malware campaign is exploiting the critical WinRAR vulnerability (CVE-2023-38831) in versions before 6.23. This vulnerability allows malicious files, like 508.rar, to execute arbitrary code on affected systems, which may lead to unauthorized access or malware installation.
This campaign emphasizes the ongoing cyber threats to Bangladesh’s critical sectors. Experts urges all entities to be more vigilant and take proactive security measures.
Malware campaign target Bangladeshi Government Entities: Report



