 InfoSecBulletin Cybersecurity for mankind

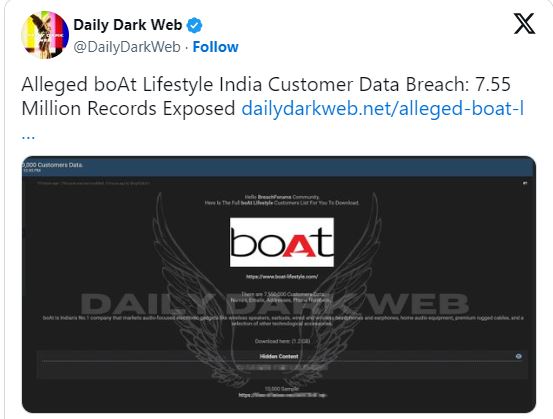
Data of over 7.5 million boAt customers is now on the dark web. This includes personal information like names, addresses, contact numbers, email IDs, and customer IDs. The attacker has released around 2GB of data on a forum.
On April 5, a hacker named ShopifyGUY said they hacked the data of boAt Lifestyle, a company that makes audio products and smartwatches. The hacker released files containing personal information of customers, which includes 7.5 million entries.
Hackers deploy Casbaneiro Trojan that activates on bank websites

German police read Signal, Telegram, WhatsApp messages without breaking encryption

Urgent Patch! cPanel, GitLab Flaws Expose Users to RCE, File and Credential Theft

Palo Alto PAN-OS Flaw Enables Root Arbitrary Code Execution

Critical Check Point VPN flaws allow remote code execution attacks

Cisco confirms CVE-2026-20079 flaw in Secure FMC is exploited in attacks

Hackers exploit PaperCut flaws using hundreds of AI agents, compromising 440 servers globally

CISA Says Chinese Firms Extracted Billions of Tokens From Frontier AI Models

Nightmare Eclipse Drops New Microsoft Defender ‘ShieldCrash’ zero-day

cPanel Flaw Lets Hosting Accounts With Mail Privileges Execute Code as Root

Forbes India said they verified the information by speaking to some of the customers who confirmed purchasing boAt products in the recent past.
Ritesh BhatiaRitesh Bhatia, Founder – V4WEB CYBERSECURITY of india said his social handle that Boat customers should put on their life jackets and exercise heightened caution as their personal information, including mobile numbers and addresses, is exposed, making them potential targets for cybercriminals. It’s advisable to verify any unfamiliar calls or letters received by post (gift cards, bumper prize letters, fake notices impersonating law enforcing agencies, etc etc )
At the very least, the Shark Tank judge, and not the media, should have notified every customer about the breach and the extent of data leakage. Mandatory corporate communications to all stakeholders within 24 to 72 hours should be enforced. As for whether Boat will incur the 50-250 crore penalty under the new Digital Personal Data Protection Bill, it seems improbable.
Founded in 2016 by Aman Gupta and Sameer Mehta from Shark Tank, boAt is now the second most popular wearable brand as per an IDC report. The Gurugram-based company is well-liked by Indian consumers for its affordable earphones, audio products, smartwatches, and speakers.
boAt Lifestyle, a company that specializes in audio devices and wearables, achieved great success in March 2023 with sales of over Rs3,000 crore. Its total revenue for the year was Rs3,403.1 crore, compared to Rs2,886.4 crore in the previous year (FY22). However, in FY23, boAt recorded a net loss of Rs129.4 crore, despite a profit of Rs68.7 crore in FY22.2.
The Indian consumer electronics company postponed its IPO in 2021 due to market instability. In October 2022, its parent company, Imagine Marketing, raised Rs500 crore from an existing shareholder, a Warburg Pincus affiliate, and a new investor, Malabar Investments. In total, the company has raised $177 million from investors including Qualcomm Ventures, InnoVen Capital, Navi Technologies, and Fireside Ventures.
boAt competes against companies like Fire-Boltt, Noise, Xiaomi and Samsung.
Source: Forbes India, Zeenews, India today



