InfoSecBulletin Cybersecurity for mankind
Fortinet has released security updates for various products, including OS and FortiProxy, to fix vulnerabilities that could allow a cyber threat actor to take control of a system.
CISA encourages users and administrators to take the following steps for enhanced security:
Apple Zero-Day Exploited: Pentagon Data Breach Reportedly Exposes Sensitive Data of 3 Million People

JadePuffer Agentic AI targets and destroys Azure’s cloud resources

“InfoSecCon-2026: Bangladesh’s Cybersecurity Leaders Unite to Shape a Safer Digital Future”

Microsoft Patches CVSS 10.0 Azure AI Foundry Vulnerability Allowing Privilege Escalation

AWS is unable to restore access to Bahrain, one UAE cloud data zone after war damage

Cisco Warns of Critical ISE 0-Day Flaw and Hackers Allegedly Selling Fortinet FortiGate 1-Day Flaw

Anthropic prepares “Claude Money” to analyze bank account and financial data

GhostCode Phishing Kit Evades Microsoft 365 MFA to Hijack Accounts in 78 Seconds

CISA Warns of Cisco Secure Email Gateway 0-Day Flaw Actively Exploited in Attacks

VPN flaw exposed 246,000 personnel records in japan

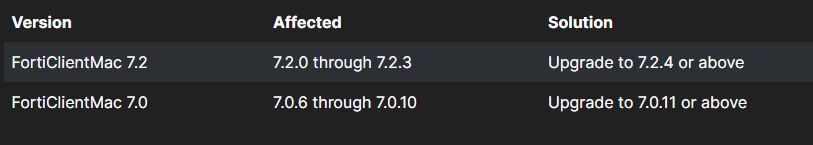
FR-IR-23-345 FortiClientMac – Lack of configuration file validation:
An external control of file name or path vulnerability [CWE-73] in FortiClientMac’s installer may allow a local attacker to execute arbitrary code or commands via writing a malicious configuration file in /tmp before starting the installation process.
FG-IR-23-493 FortiOS & FortiProxy – Administrator cookie leakage
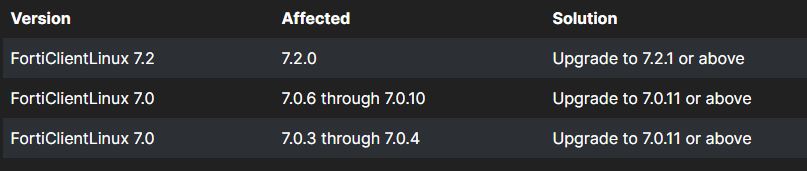
FG-IR-23-087 FortiClient Linux – Remote Code Execution due to dangerous nodejs configuration:
An Improper Control of Generation of Code (‘Code Injection’) vulnerability [CWE-94] in FortiClientLinux may allow
an unauthenticated attacker to execute arbitrary code via tricking a FortiClientLinux user into visiting a malicious website.