 InfoSecBulletin Cybersecurity for mankind
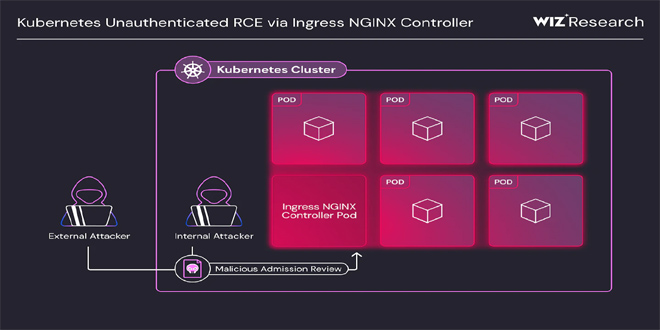
Kubernetes users of the Ingress NGINX Controller are advised to fix four newly found remote code execution ( RCE) vulnerabilities, which have a CVSS score of 9.8.
Wiz Security named four vulnerabilities “IngressNightmare” that affect the admission controller of the popular open-source software used for directing external traffic to Kubernetes services and pods.
North Korean hackers steal more than $400 million using video images, FBI says

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

89 New ransomware groups emerge in 2026, claiming over 2,200 victims

Daily Cyber security update for 08.11. 2026

Japan banking crisis
Outage causes disruption at 128 japan banks: preventing ATM transaction

Wiz Research claimed the flaws impact 43% of all cloud environments, including many Fortune 500 companies. Because the software’s admission controllers are typically exposed to the public internet, they are at “critical risk” of attack, it warned.
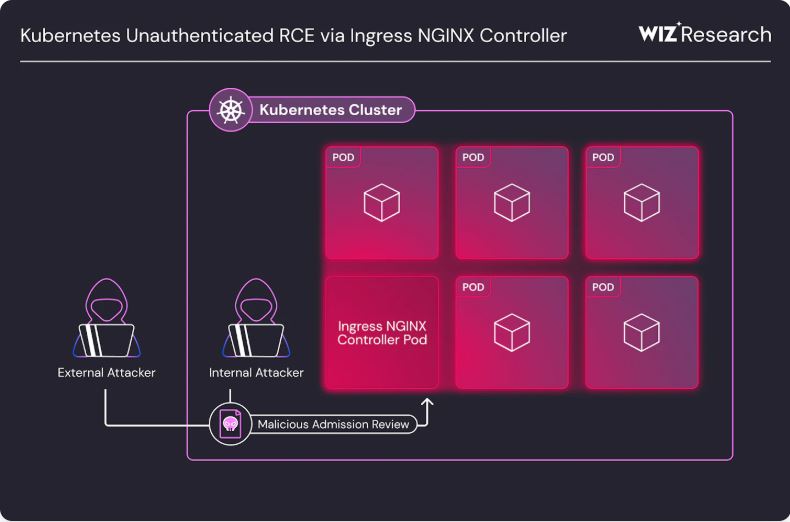
The vulnerabilities are CVE-2025-1097, CVE-2025-1098, CVE-2025-24514, and CVE-2025-1974. The first three allow an attacker to inject arbitrary NGINX configuration directives, potentially leading to remote code execution when combined with the fourth vulnerability.
“When the Ingress-NGINX admission controller processes an incoming ingress object, it constructs an NGINX configuration from it and then validates it using the NGINX binary. Our team found a vulnerability in this phase that allows injecting an arbitrary NGINX configuration remotely, by sending a malicious ingress object directly to the admission controller through the network,” Wiz Security explained.
“During the configuration validation phase, the injected NGINX configuration causes the NGINX validator to execute code, allowing remote code execution (RCE) on the Ingress NGINX Controller’s pod.”
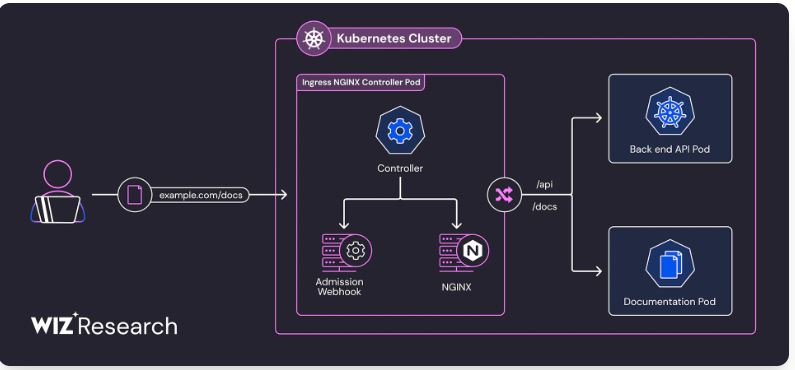
The admission controller has high-level permissions and full network access, so exploiting these vulnerabilities could let an attacker run any code, access all cluster secrets, and fully control a targeted cluster, it added.
Kubernetes admins should upgrade to Ingress NGINX Controller versions 1.12.1 and 1.11.5, and make sure the admission webhook endpoint is not publicly accessible.
The security vendor has provided mitigations for those unable to upgrade to patched versions right away.



