 InfoSecBulletin Cybersecurity for mankind
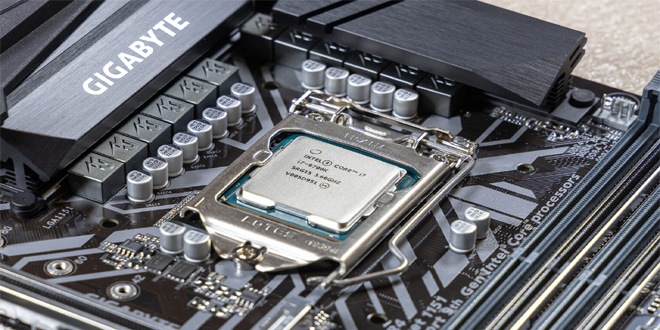
Researchers at firmware and hardware security company Eclypsium discovered that hundreds of motherboard models made by Taiwanese computer components giant Gigabyte include backdoor functionality that could pose a significant risk to organizations.
The backdoor was discovered by Eclypsium based on behavior associated with the functionality, which triggered an alert in the company’s platform.
Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

89 New ransomware groups emerge in 2026, claiming over 2,200 victims

Daily Cyber security update for 08.11. 2026

Japan banking crisis
Outage causes disruption at 128 japan banks: preventing ATM transaction

Daily Cyber security update for 06.11. 2026

Cyber attack causes French bank Credit Mutuel Arkea €100 million missing

Specifically, the researchers determined that the firmware on many Gigabyte systems drops a Windows binary that is executed when the operating system boots up. The dropped file then downloads and runs another payload fetched from Gigabyte servers.
ALSO READ:
The payload is downloaded over an insecure connection – HTTP or improperly configured HTTPS — and the file’s legitimacy is not verified.
There is no evidence that the backdoor has been leveraged for malicious purposes and the feature appears related to the Gigabyte App Center, which is documented on the company’s website.
However, Eclypsium said it’s difficult to conclusively rule out that it is a malicious backdoor planted from within Gigabyte — either by a malicious insider or as a result of the company’s systems being compromised. It’s also difficult to definitively rule out that the backdoor was planted somewhere in the supply chain.
Even if the feature is legitimate, the cybersecurity firm warned that it could end up being abused by threat actors. It’s not uncommon for skilled hackers to take advantage of such tools in their attacks.
UEFI rootkits have in many cases been used to ensure that Windows malware can persist on a compromised system and this backdoor can be useful for that purpose. In addition, these types of firmware backdoors can be difficult to remove. (Affected models here)
Eclypsium also warned that hackers could take advantage of the insecure connection between the system and Gigabyte servers to replace the payload through a man-in-the-middle (MitM) attack.
Eclypsium has published a list of more than 270 affected motherboard models — this indicates that millions of devices likely have the backdoor. The company said it has been working with Gigabyte to address the issue, which will likely require a firmware update.
Threat actors have been known to target Gigabyte products in their attacks, including with sophisticated UEFI rootkits.
Gigabyte is starting to release a fix to address the motherboard vulnerability.



