InfoSecBulletin Cybersecurity for mankind

OpenAI has revealed a data breach involving Mixpanel, a third-party analytics provider that was used to monitor API platform usage. The breach exposed limited but sensitive user information, including names, email addresses, operating system details, and browser metadata.
OpenAI stated that the incident came from Mixpanel’s infrastructure and did not involve any attack on OpenAI’s systems. On November 9, 2025, Mixpanel found unauthorized access and discovered an attacker had exported customer data.
Daily Cyber security update for 14.11. 2026

Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

PHP2Shell attack exploited a Check Point 0-day to deploy malware

North Korean hackers steal more than $400 million using video images, FBI says

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

Mixpanel notified OpenAI about the breach and, by November 25, 2025, shared the specific dataset affected. Data affected was only from OpenAI’s API users through the platform.openai.com interface. ChatGPT and other OpenAI services were not impacted.
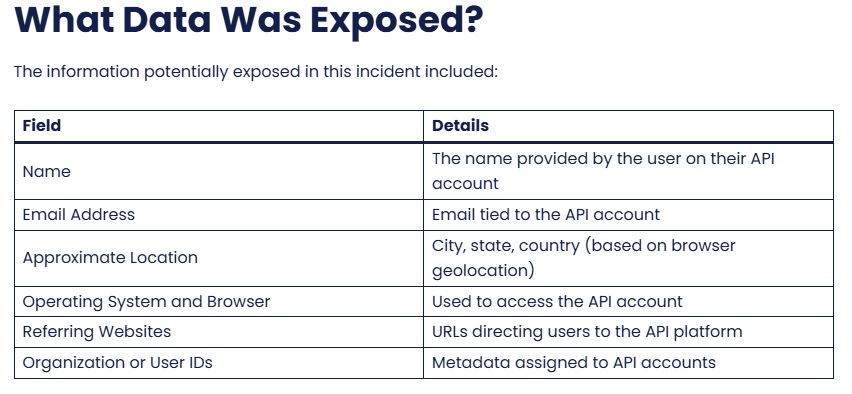
After Mixpanel’s notification, OpenAI quickly removed all Mixpanel analytics integrations from its services and reviewed the impacted datasets. The company is collaborating with Mixpanel to fully evaluate the breach and is informing all affected organizations, admins, and users.
OpenAI advises users to be alert for phishing or social engineering attacks because of the exposed data. If you get an unexpected email or message, you should:
Treat unexpected emails or messages with caution, especially if they include links or attachments.
Double-check that any message claiming to be from OpenAI is sent from an official OpenAI domain.
OpenAI does not request passwords, API keys, or verification codes through email, text, or chat.
Further protect your account by enabling multi-factor authentication (opens in a new window).
The incident highlights the risks of third-party service providers and the need for ongoing security reviews and strong vendor management to protect user data.