 InfoSecBulletin Cybersecurity for mankind
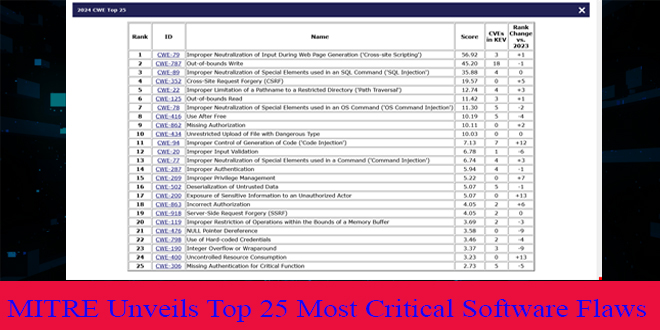
MITRE identified Cross-site scripting as the most critical software flaw in its recent published report of the past year. The nonprofit published its latest ranking of the Top 25 Most Dangerous Software Weaknesses on November 20, highlighting critical flaws from the Common Weakness Enumeration (CWEs) catalog between June 2023 and June 2024.
CWE is a list of common software weaknesses in code, design, or architecture that can lead to vulnerabilities, which are cataloged in the CVE database.
Daily Cyber security update for 14.11. 2026

Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

PHP2Shell attack exploited a Check Point 0-day to deploy malware

North Korean hackers steal more than $400 million using video images, FBI says

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

MITRE reviewed 31,770 CVEs from 2023 and 2024 to determine the criticality level of software weaknesses that needed re-mapping analysis.
MITRE assigned scores to each weakness based on severity and how often they are exploited, particularly focusing on security flaws in the CISA’s Known Exploited Vulnerabilities (KEV) catalog.
Cross-site scripting, or CWE-79, ranked first this year with a score of 56.92 and three known exploited vulnerabilities. It replaced last year’s most dangerous CWE, ‘Out-of-bounds Write’ (CWE-787), which had 18 known exploited vulnerabilities and a score of 45.20.
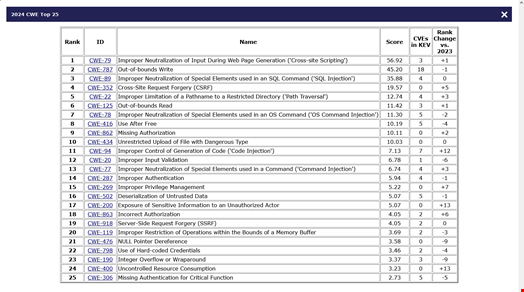
SQL Injection, or ‘Improper Neutralization of Special Elements used in an SQL Command’ (CWE-89), ranks third with a score of 35.88 and has four known exploited vulnerabilities.
MITRE stated that the ranking is a useful resource for developers and security professionals and acts as a strategic guide for organizations looking to make informed decisions about software, security, and risk management investments.
“Organizations are strongly encouraged to review this list and use it to inform their software security strategies. Prioritizing these weaknesses in development and procurement processes helps prevent vulnerabilities at the core of the software lifecycle,” the organization added.
The nonprofit works with CISA on the CVE and CWE programs. CISA regularly issues alerts highlighting common software vulnerabilities, despite effective solutions being available.



