InfoSecBulletin Cybersecurity for mankind
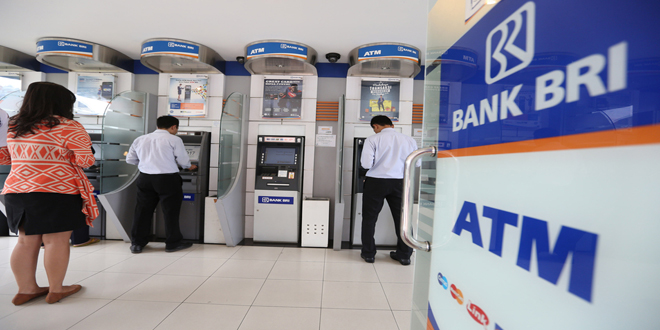
Bank Rakyat Indonesia (BRI), the largest state bank by assets, has assured customers that their data and funds are secure and that normal transactions continue uninterrupted, despite rumors of a ransomware attack on social media.
On Wednesday evening, BRI’s Director of Digital and IT, Arga M. Nugraha, confirmed via Instagram that the bank’s systems are fully operational.
WinRAR, WordPress RCE flaw & Zyxel GS1900 Zero-Day exploited in the wild

Daily Cyber security update for 04.11. 2026

Daily Cyber security update for 03.11. 2026

Using ARTEX AI, Hacker to attack 200 Organizations Across 14 Countries

Amadeus cyber incident impacted “Cathay Pacific, Qantas, Japan, Malaysia, Korean & Asiana” Airlines

Multiple European supermarket fridges got hacked: Temperatures reached high as 55°C

Apple Warns 99 Countries iPhone Users of Mercenary Spyware Attacks

Daily Cyber security update for 31.10. 2026

NetamLoader malware to attack Win10: Customized for Gov.t in Asia
‘SMS of Death’ Zero-Click Flaw Disrupting Android Phones With a Single Text
“We confirm that both customer data and funds are secure. All BRI banking systems are functioning normally, and our transaction services are operating smoothly,” Arga said in the statement.
He assured customers that they can continue using BRI’s banking services, including digital platforms like BRImo, QLola, ATMs, CRMs, and more, with full data security.
The bank stated that its information security systems meet international standards and are regularly updated to tackle new threats.
“Proactive measures are in place to ensure that customer information remains protected,” Arga added.
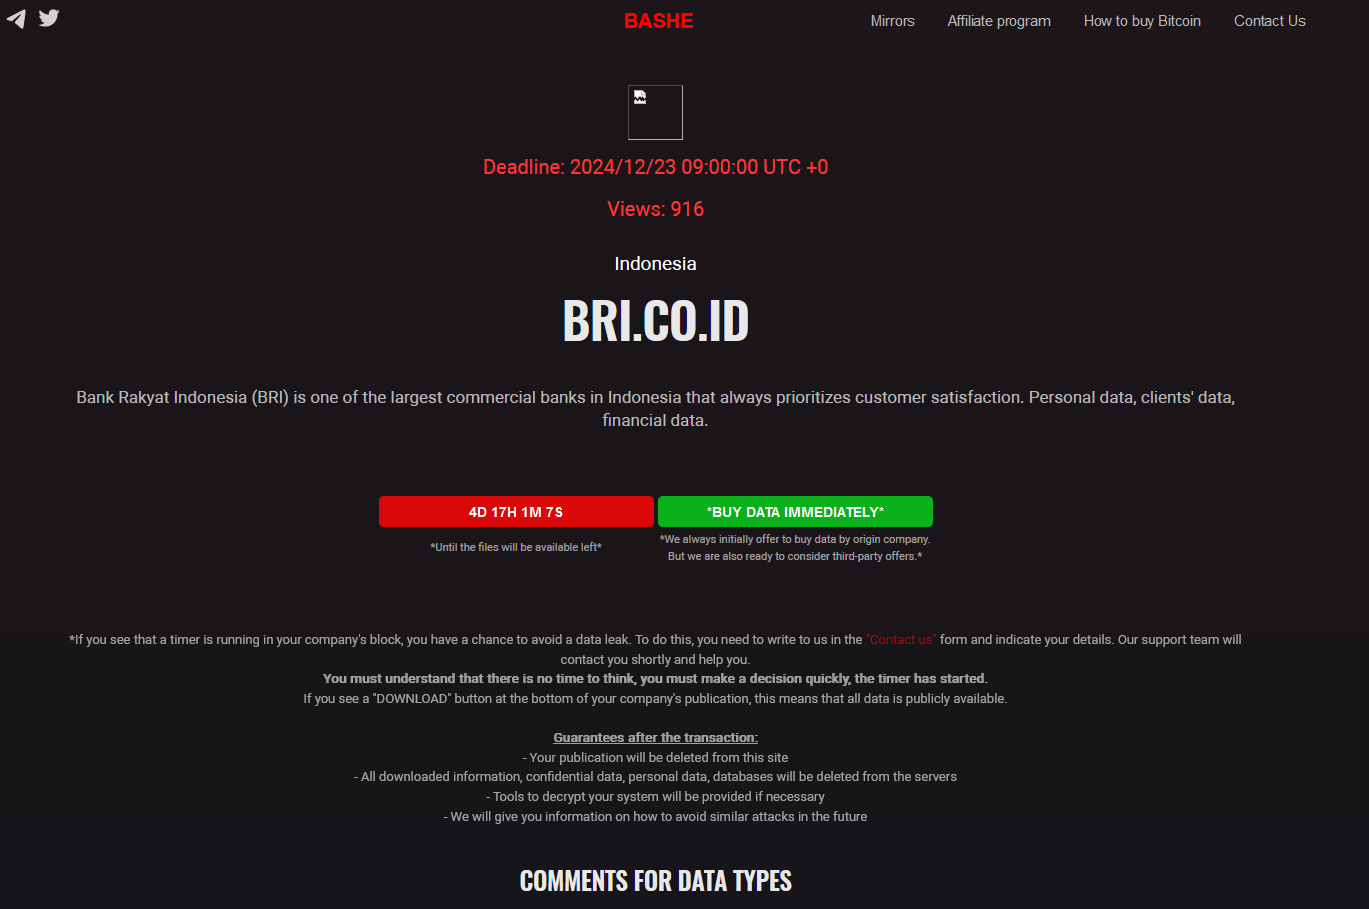
The statement follows social media rumors on Wednesday evening about a possible data breach at BRI.
The attack is thought to be connected to Bashe Ransomware, which has ties to the infamous LockBit group responsible for breaching Indonesia’s National Data Center in June.
Bashe Ransomware mainly targets high-value sectors such as technology, business services, manufacturing, finance, transportation, and healthcare. Its attacks occur in North America and Europe.
Bashe Ransomware usually spreads via phishing emails with malware. When a victim opens the email, the malware quickly encrypts their data across the network. Victims must pay a ransom to access their files again.
Source: darkwebinformer, jakartaglobe, indonesiabusinesspost
((Media Disclaimer: This report is based on research conducted internally and externally using different ways. The information provided is for reference only, and users are responsible for relying on it. Infosecbulletin is not liable for the accuracy or consequences of using this information by any means))
Uganda confirms hack of central bank accounts, Refutes $17 Million Claim