InfoSecBulletin Cybersecurity for mankind
A breach notification site has added millions of new passwords and email addresses obtained from infostealer malware. Troy Hunt, founder of HaveIBeenPwned (HIBP), added 244 million new passwords and 284 million new email accounts to the database after analyzing 1.5TB of stolen logs posted on Telegram.
Six 0-Days Discovered by Researchers Allow Unauthorized Access to Supermarket Fridge Systems

Daily Cyber security update for 14.11. 2026

Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

PHP2Shell attack exploited a Check Point 0-day to deploy malware

North Korean hackers steal more than $400 million using video images, FBI says

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

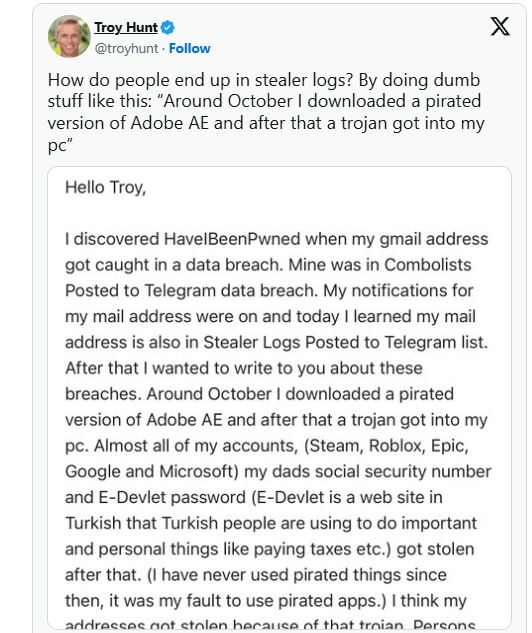
Hunt identified an account called “Alien Textbase” as a significant source for infostealer logs on Telegram. The logs were shared in 744 separate files.
On February 25, HIBP launched two new APIs that help domain owners and website operators find customers with compromised email addresses or passwords by checking stealer logs using email and website domains.
“Both these new APIs are orientated towards larger organisations and can return vast volumes of data,” Hunt said.
While APIs are a paid service, regular HIBP subscribers can check if their accounts have been compromised for free.
HIBP recently added 12 million compromised accounts from BreachForums, but 93% of this data was already in their repository. Infostealers are increasingly threatening corporate and consumer security. Earlier this month, Check Point reported a 58% rise in attacks using this malware and noted over 10 million stolen credentials from EMEA organizations for sale on the dark web.
Infostealers are spread through phishing messages, drive-by downloads, malicious ads, and disguised as legitimate or pirated software. They steal data like credentials, crypto assets, and credit card information, which is then compiled and sold online by vendors like Alien Textbase.
Credential theft from this type of malware poses a significant threat to corporations. Major data breaches at Ticketmaster and AT&T occurred when hackers accessed their Snowflake accounts using credentials stolen by infostealers.