Wednesday , November 11 2026
Microsoft 365 accounts

Botnet Powered by 130,000 Devices Targets Microsoft 365 Accounts

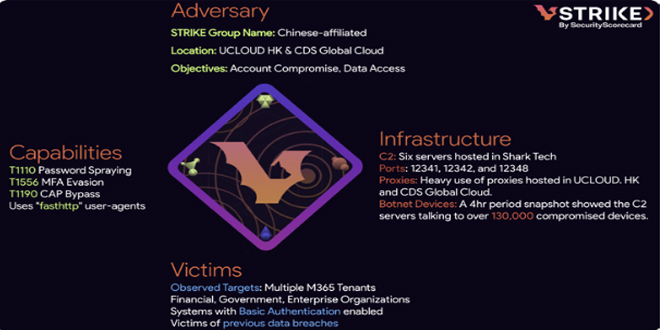
A China-linked botnet is targeting Microsoft 365 accounts with widespread password spraying attacks, according to a report by SecurityScorecard.
Souce: securityscorecard

A security firm reports that a botnet with over 130,000 compromised devices is targeting Microsoft 365 accounts through non-interactive sign-ins using Basic Authentication.

Barracuda ESG flaws exploited, gaining root access

Barracuda has confirmed active exploitation of security flaws affecting its Email Security Gateway (ESG), warning that attackers could combine two...
Read More
Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Apple, SAP, and Ivanti have published security updates that fix several flaws with messaging, Bluetooth, enterprise servers, and endpoint management...
Read More
Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

A jailbroken AI has been attacking a European telecom company and 13 companies using its data center and cloud for...
Read More
Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

IBM patched 208 security flaws in its API Connect platform. The CVE records released out on November 7, 2026. Among...
Read More
IBM fixes 208 API Connect vulnerabilities, 47 critical

89 New ransomware groups emerge in 2026, claiming over 2,200 victims

New ransomware actions in 2026 show more variety in cybercrime, with some groups claimed over 100 victims. The ransomware attack...
Read More
89 New ransomware groups emerge in 2026, claiming over 2,200 victims

Daily Cyber security update for 08.11. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 08.11. 2026

Japan banking crisis
Outage causes disruption at 128 japan banks: preventing ATM transaction

A major system failure has brought customer-facing banking services to a standstill at 128 shinkin banks across western Japan, leaving...
Read More
Japan banking crisis  Outage causes disruption at 128 japan banks: preventing ATM transaction

Daily Cyber security update for 06.11. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 06.11. 2026

Cyber attack causes French bank Credit Mutuel Arkea €100 million missing

French lender Credit Mutuel Arkea said on Thursday hackers had stolen around €100 million ($112.61 million) in a cyber heist...
Read More
Cyber attack causes French bank Credit Mutuel Arkea €100 million missing

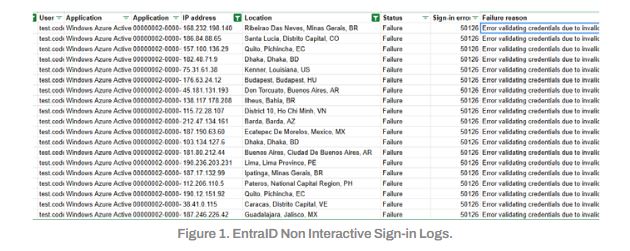
“Non-interactive sign-ins, commonly used for service-to-service authentication, legacy protocols (e.g., POP, IMAP, SMTP), and automated processes, do not trigger MFA in many configurations. Basic Authentication, still enabled in some environments, allows credentials to be transmitted in plain form, making it a prime target for attackers.,” SecurityScorecard said.

Microsoft is phasing out Basic Authentication, but security experts warn that these attacks still present an immediate threat. The attack is stealthy because password spraying attempts are logged but usually go unmonitored by security teams.

SecurityScorecard found multiple command and control servers in the United States. Over four hours, they monitored connections from 130,000 devices to these servers.
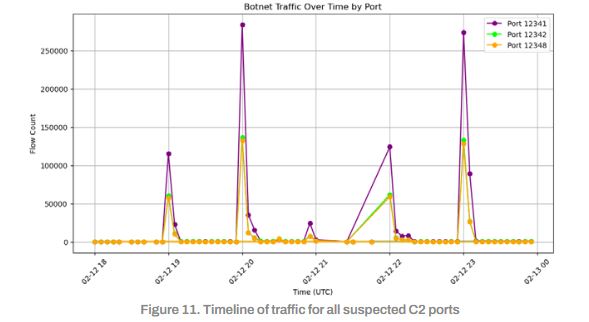
The botnet uses devices to steal credentials from malware and tests them on Microsoft 365 accounts. Hackers can access accounts to steal sensitive information, disrupt business operations, and move through the targeted organization.

The security firm suspects a Chinese threat group controls the botnet, but they are still investigating.

In October 2024, Microsoft reported that several Chinese threat actors were using credentials obtained from a password spray operation involving compromised devices known as CovertNetwork-1658, Xlogin, and Quad7.


Check Also

Multiple European supermarket fridges got hacked: Temperatures reached high as 55°C

A cyberattack on refrigeration systems has affected stores of many supermarket chains in various European …