 InfoSecBulletin Cybersecurity for mankind
ZeroFont Phishing is a new yet old technique for sending Phishing emails. It allows threat actors to bypass security mechanisms and successfully send phishing emails. Using this technique, attackers were able to evade Microsoft’s Natural Language Processing, which was serving as portion against phishing emails for Office users.
Office 365 – Natural Language Processing
Nearly 100,000 email addresses exposed in first AI-related data breach in Singapore

Hackers Exploit Zimbra Mail Servers: TeamViewer patched 5 critical flaws

Google Warns of Hackers Actively Exploiting Citrix 0-Day Flaws

CISA Warns Critical MikroTik RouterOS Flaw While Cisco SD-WAN Zero-Day Exploited in Attacks

Apple Zero-Day Exploited: Pentagon Data Breach Reportedly Exposes Sensitive Data of 3 Million People

JadePuffer Agentic AI targets and destroys Azure’s cloud resources

“InfoSecCon-2026: Bangladesh’s Cybersecurity Leaders Unite to Shape a Safer Digital Future”

Microsoft Patches CVSS 10.0 Azure AI Foundry Vulnerability Allowing Privilege Escalation

AWS is unable to restore access to Bahrain, one UAE cloud data zone after war damage

Cisco Warns of Critical ISE 0-Day Flaw and Hackers Allegedly Selling Fortinet FortiGate 1-Day Flaw

Microsoft is focused on securing its customers in all areas, especially phishing attacks. Phishing attacks, also known as Business Email Compromise, are commonly used by threat actors to infiltrate organizations.
Microsoft prevents phishing emails by using Natural Language Processing. This technology scans the contents of an email to detect signs of impersonation or fraud. If an email contains text such as “© 2018 Microsoft Corporation. All rights reserved” and is not from Microsoft.com, Microsoft flags it as fraudulent.
Threat actors used the ZeroFont Phishing attack to bypass email content authentication. The technique was used to understand different types of information, like banking details, user accounts, password resets, and financial requests.
ZeroFont Phishing
The attacker sends a fake email pretending to be from Office 365, warning the victim about a quota limit. The email looks like it’s from an administrative service. The phishing email uses the ZeroFont attack to bypass security measures.
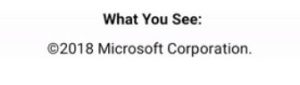
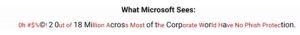
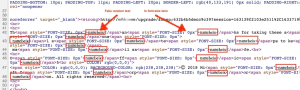
Threat actors inserted random text inside the email, which had <span style=”FONT-SIZE: 0px”> for a zero font size, and broke up the text strings to bypass Microsoft’s natural language processing.
To read the full report published by Avana click here.
Also read:
An attack every 39 seconds, approximately 2,200 attacks per day: Cyber awareness month starts



