 InfoSecBulletin Cybersecurity for mankind
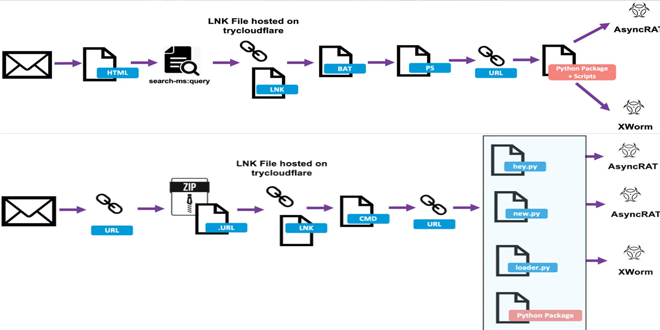
Proofpoint is monitoring a group of cybercriminals using Cloudflare Tunnels to distribute malware. They are exploiting the TryCloudflare feature to create one-time tunnels without needing an account. Tunnels allow remote access to data and resources not on the local network, similar to using a virtual private network (VPN) or secure shell (SSH) protocol.

In February 2024, a cluster was first seen. From May to July, there was an increase in activity. Most of the campaigns resulted in Xworm, a remote access trojan (RAT), in the past few months.
Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

89 New ransomware groups emerge in 2026, claiming over 2,200 victims

Daily Cyber security update for 08.11. 2026

Japan banking crisis
Outage causes disruption at 128 japan banks: preventing ATM transaction

Daily Cyber security update for 06.11. 2026

Cyber attack causes French bank Credit Mutuel Arkea €100 million missing

OpenAI AI Pipeline Discovers 948 Linux Kernel Privilege Escalation Flaws in 30 Hours

Bangladeshi Researcher Rasel Earns First Apple CVE Recognition for Model I/O Flaw

Campaign messages often include a URL or attachment that leads to an internet shortcut (.URL) file. This file connects to an external file share when opened, allowing the download of malicious files. These files can lead to the installation of malware on the user’s system. In some cases, a benign PDF file is shown to the user to look trustworthy.
Most campaigns in June and July delivered a malware called Xworm. However, previous campaigns delivered other malwares like AsyncRAT, VenomRAT, GuLoader, and Remcos. Some campaigns even lead to the installation of multiple malwares, with each unique Python script installing a different one.
Campaign messages can range from hundreds to tens of thousands, affecting many organizations worldwide. Besides English, researchers found lures in French, Spanish, and German. Xworm, AsyncRAT, and VenomRAT campaigns are usually larger than Remcos or GuLoader campaigns. Lure topics vary, but often relate to business, like invoices, document requests, package deliveries, and taxes.
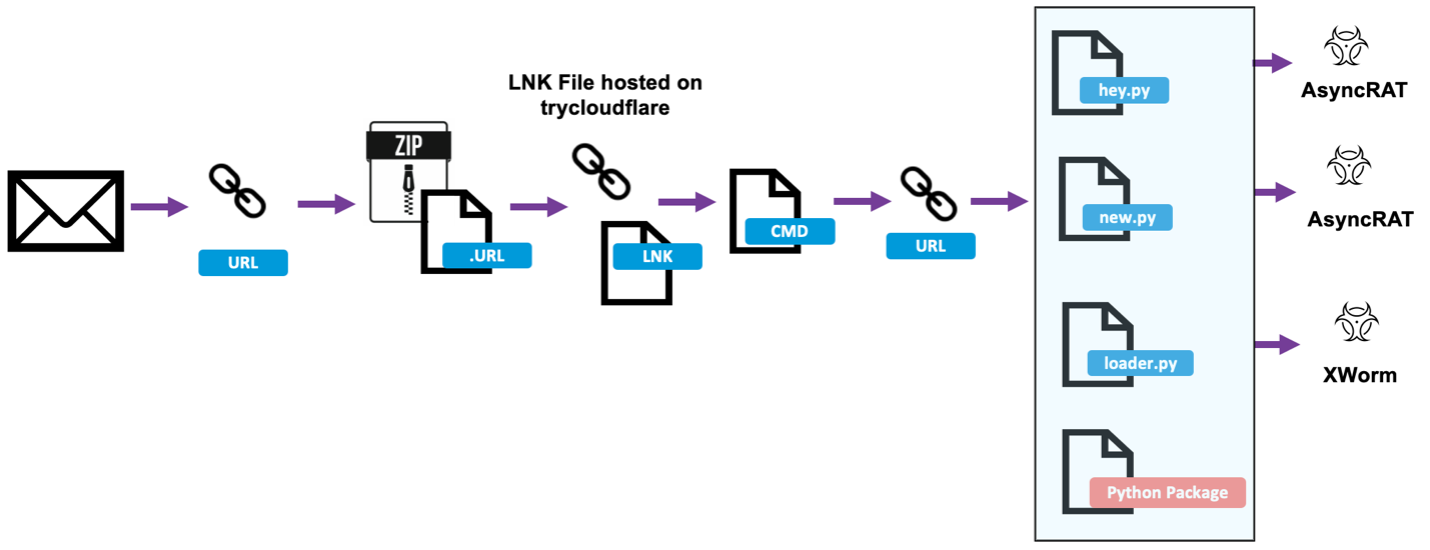
The threat actor modifies different parts of the attack chain to become more sophisticated and avoid defense. Initially, their scripts had no obfuscation and included detailed comments. However, in June, they started to use obfuscation in their code.
Cybercriminals are increasingly using TryCloudflare tunnels to create random subdomains on trycloudflare.com, such as ride-fatal-italic-information.trycloudflare.com, to proxy traffic to their local servers. Full report here.



