Sunday , November 15 2026

BingoMod RAT: Android Banking Trojan Empties Accounts, Wipes data

Cleafy found a harmful software called BingoMod that targets Android devices. The malware tries to get into bank accounts on the device and steal money, then it erases the device’s activity.

Cleafy says that BingoMod is a type of remote access Trojan (RAT). Attackers can use it to control devices remotely and steal bank account information. They do this by tricking users into enabling accessibility services and granting control permissions.

Daily Cyber security update for 14.11. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 14.11. 2026

Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

The Latvian part of CSCTelecom,  a telecommunications provider, made a database with over 125 million SMS messages public. The leaked...
Read More
Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

PHP2Shell attack exploited a Check Point 0-day to deploy malware

Hackers used Check Point firewall flaws to get root access, insert backdoors, and install harmful malware on a VMware ESXi...
Read More
PHP2Shell attack exploited a Check Point 0-day to deploy malware

North Korean hackers steal more than $400 million using video images, FBI says

The United States Justice Department said Thursday it had seized cloud infrastructure used by North Korean hackers in a video-call...
Read More
North Korean hackers steal more than $400 million using video images, FBI says

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Microsoft has shared its updates for November 2026. These updates fix 1,093 new flaws in Windows, Office, SQL Server, SharePoint,...
Read More
Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Barracuda has confirmed active exploitation of security flaws affecting its Email Security Gateway (ESG), warning that attackers could combine two...
Read More
Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Apple, SAP, and Ivanti have published security updates that fix several flaws with messaging, Bluetooth, enterprise servers, and endpoint management...
Read More
Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

A jailbroken AI has been attacking a European telecom company and 13 companies using its data center and cloud for...
Read More
Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

IBM patched 208 security flaws in its API Connect platform. The CVE records released out on November 7, 2026. Among...
Read More
IBM fixes 208 API Connect vulnerabilities, 47 critical

After getting the required permissions, BingoMod is able to install itself and activate the keyboard operation logging feature of accessibility services. This allows it to steal user credentials used for banking services. It also intercepts SMS messages to obtain verification codes for financial transactions, making it possible to transfer funds from the user’s bank account unnoticed.
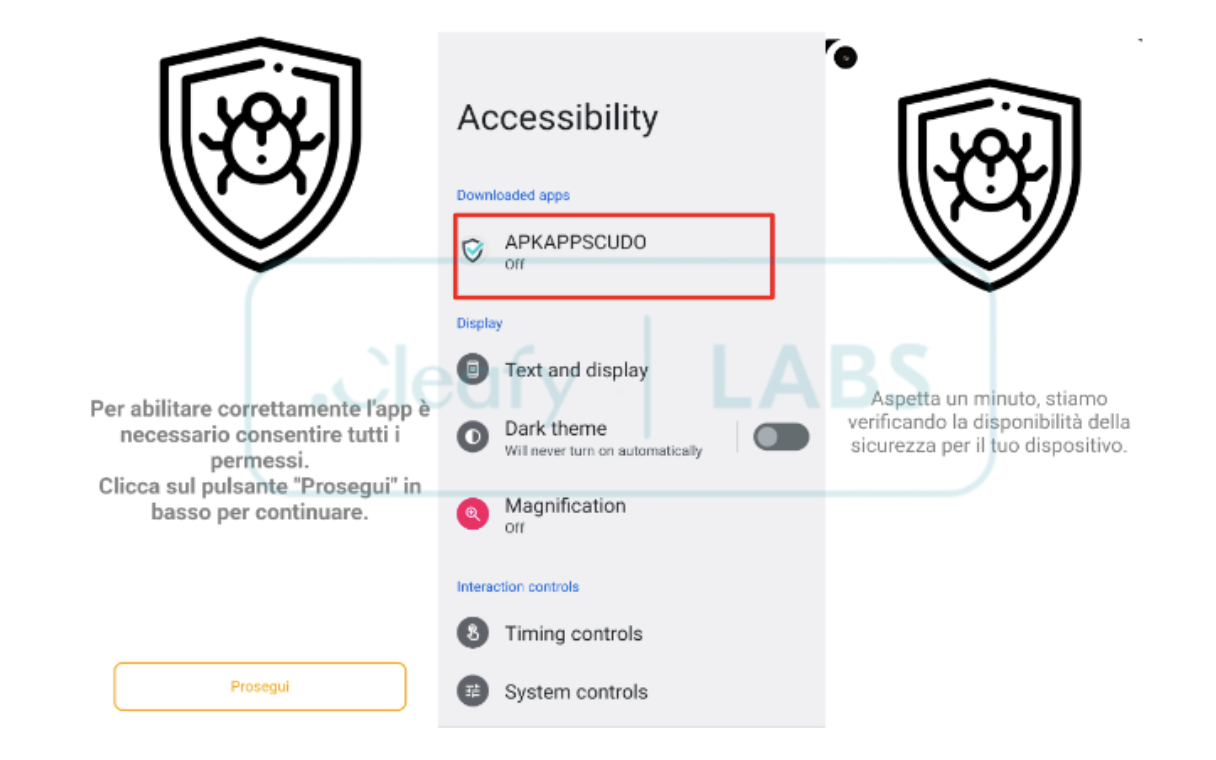
    Starting phase of BingoMod

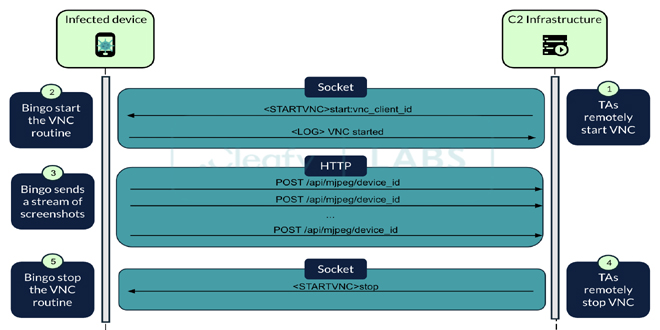
During the attack, BingoMod uses the system media projection API to capture and send the screen content to the attackers. After the attack, BingoMod erases external storage devices, like memory cards, on the affected device. Attackers can remotely control and delete all the stored content on the device, making it hard for the victim to trace.

Cleafy recommends not installing unfamiliar apps on Android devices and being careful with suspicious permission requests. They also suggest installing security software, enabling two-factor authentication, and regularly checking banking transactions for any malicious activity.
Check Also

Marquis

Over 74 US banks, credit unions impacted via Marquis data breach

Marquis Software Solutions has announced a data breach affecting multiple banks and credit unions in …