 InfoSecBulletin Cybersecurity for mankind

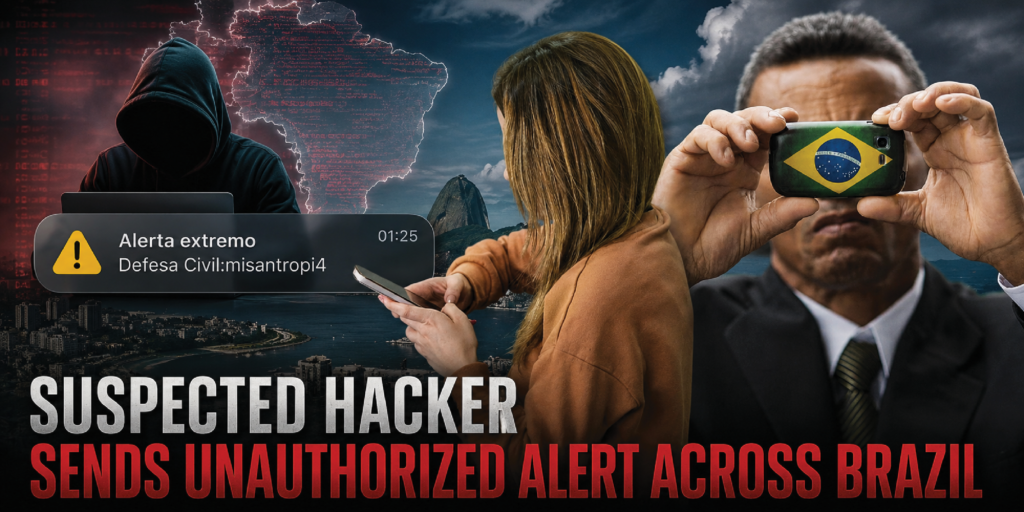
Brazil’s government suspects a hacking attack triggered an unauthorized alert sent to cell phones across parts of the country early on Saturday. In a statement, the National Protection and Civil Defense Secretariat said the country’s citizens’ notification system was taken offline at around 1:30 a.m. local time (0430 GMT) after a message containing the word “misanthropy” – meaning hatred of humanity – was sent to users in several states.
The unauthorized alert, which was ordered remotely, will be handed to the Federal Police for investigation, and the notification system will be restored as soon as possible, according to the statement.
Hackers deploy Casbaneiro Trojan that activates on bank websites

German police read Signal, Telegram, WhatsApp messages without breaking encryption

Urgent Patch! cPanel, GitLab Flaws Expose Users to RCE, File and Credential Theft

Palo Alto PAN-OS Flaw Enables Root Arbitrary Code Execution

Critical Check Point VPN flaws allow remote code execution attacks

Cisco confirms CVE-2026-20079 flaw in Secure FMC is exploited in attacks

Hackers exploit PaperCut flaws using hundreds of AI agents, compromising 440 servers globally

CISA Says Chinese Firms Extracted Billions of Tokens From Frontier AI Models

Nightmare Eclipse Drops New Microsoft Defender ‘ShieldCrash’ zero-day

cPanel Flaw Lets Hosting Accounts With Mail Privileges Execute Code as Root

Devices lit up with the word “misantropi4,” an alphanumeric spelling of the Portuguese word “misantropia,” which in English translates to “misanthropy.” The final letter “a” was substituted with a number ‘4’ – a practice often used by hackers and termed “leetspeak.”
The alert – categorized as “extreme” – was initially received in the southern state of Paraná, but a second warning was triggered a few minutes later for cell phones in the major cities of São Paulo and Rio de Janeiro.
São Paulo Civil Defense said in a statement that the alert was not sent by any of its agents and, so far, there is no record of any incident justifying the issuance of an extreme alert related to the reported content.
The statement also said that the Cellbroadcast tool, which is used to send severe and extreme alerts, is managed by Anatel (National Telecommunications Agency) and has been temporarily disabled. The São Paulo Civil Defense said it has contacted Anatel and other institutions involved in the system’s operation to investigate the origin of the message.
In addition to the alert through the Cellbroadcast platform, residents of the city of São Paulo also reported receiving a message with the same content via SMS.
In Paraná, the state government said the alert was not triggered by the state’s Civil Defense and there are no severe events forecasted for Curitiba. The state said it contacted the National Civil Defense and Anatel about the case.



