 InfoSecBulletin Cybersecurity for mankind
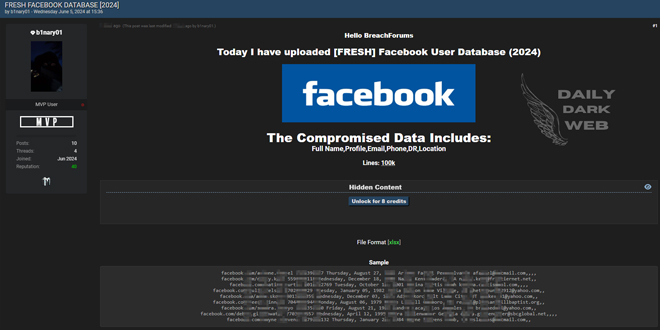
Bad actor claimed to have leaked a database of Facebook users from 2024. The database has 100,000 lines of data with names, profiles, emails, phone numbers, registration dates, and locations.
If the claim is true, users are at risk due to the leak. They might be victims of identity theft, phishing scams, or social engineering attacks. To protect themselves, users should change their passwords, enable two-factor authentication (2FA), and watch out for any suspicious activity in their accounts.
US banks faced unauthorized access by AI agents in customer accounts: Axios reports

Atlassian patched 176 flaw in Jira and Confluence: Fortinet Urges to Patch Flaws Affecting FortiOS, FortiManager

Hacker claim to access Rajasthan Police data: 70,000 records allegedly exposed

Update now! PHP2Shell: Critical PHP vulnerabilities patched

Trump says data centres should pay dividends to local community

Hackers Actively Exploiting Palo Alto VPN Flaw Via CVE-2026-0257

DeepSeek AI banned by U.S. Government; federal agencies must remove all related tools

CISA, NSA and NIST Publish New 10 AI Agent Control Guidelines

Claude AI Cracks 25-Year NSA Cryptography Number Mystery in Just 30 Minutes

Bypassing firewalls, AI Agents Accessed Indian ‘ Data Without Permission: CERT-In

Accessing the leaked Facebook user database allows hackers to use people’s personal information for harmful purposes. This includes their full names, email addresses, phone numbers, and locations. The data can be used for targeted phishing, identity theft, and social engineering. Hackers may also sell this information on the dark web, putting affected users at risk of exploitation and privacy violation. Users should stay alert and take steps to protect their accounts and personal information reported by dailydarkweb.
The dataset contains passwords and websites linked to them. It reveals a lot of new data that has been added to the breach alert service called Have I Been Pwned (HIBP).
Troy Hunt reported a big data breach was found with a combolist containing 122GB of data containing 361 million unique email addresses taken from thousands of Telegram channels. This shows that Telegram is widely used for sharing sensitive and illicit data.
(Media Disclaimer: This report is based on research conducted internally and externally using different ways. The information provided is for reference only, and users are responsible for relying on it. Infosecbulletin is not liable for the accuracy or consequences of using this information by any means)



