 InfoSecBulletin Cybersecurity for mankind
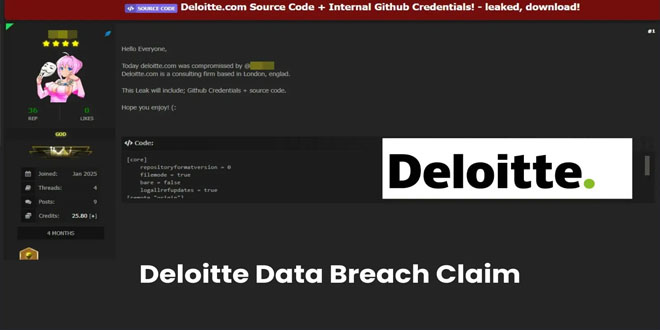
A hacker known as “303” claim to breach the company’s systems and leaked sensitive internal data on a dark web forum. The reported breach involves GitHub credentials and source code from Deloitte’s U.S. consulting division’s internal project repositories.
Medium reports, “On May 30, 2025, Deloitte, a leading global consulting firm, faced a significant cybersecurity incident. A threat actor known as “303” claimed responsibility for breaching Deloitte’s systems, allegedly accessing and leaking sensitive internal data, including GitHub credentials and source code from internal project repositories of Deloitte’s U.S. consulting division.”
Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

89 New ransomware groups emerge in 2026, claiming over 2,200 victims

Daily Cyber security update for 08.11. 2026

Japan banking crisis
Outage causes disruption at 128 japan banks: preventing ATM transaction

Daily Cyber security update for 06.11. 2026

Cyber attack causes French bank Credit Mutuel Arkea €100 million missing

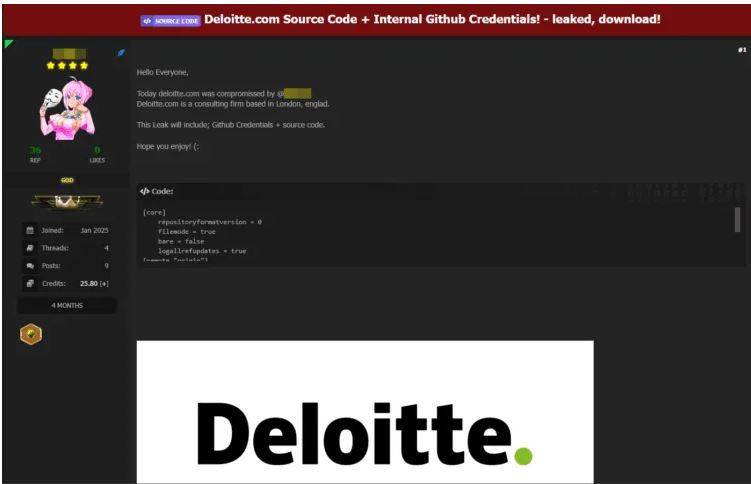
Cybersecuritynews reports indicate that a threat actor shared information about a suspected breach on a popular dark web forum, claiming to have accessed and stolen key development resources.
The leaked data reportedly contains GitHub credentials that could allow unauthorized access to Deloitte’s internal development systems and proprietary source code.
This latest incident adds to Deloitte’s ongoing cybersecurity challenges. The consulting firm has faced multiple breach allegations in recent months, including claims from the Brain Cipher ransomware group in December 2024, which Deloitte denied, stating that any compromised data originated from “a single client’s system which sits outside of the Deloitte network”. The company emphasized that “no Deloitte systems have been impacted” during that incident.
However, Deloitte’s history with credential leaks dates back several years. In 2017, security researchers discovered that Deloitte’s corporate VPN passwords, usernames, and operational details had been exposed in a public-facing GitHub repository.
The threat actor with the alias “303” has been linked to previous cybersecurity incidents, including an alleged breach of an Indian software company in December 2024 that affected major insurance providers. This pattern suggests the threat actor may be part of a broader campaign targeting large corporations and government entities.
The consulting giant has not provided a prompt response to inquiries seeking clarification or comment on the recent allegations that have come to light. As the investigations progress and further details emerge.
Source: Cybersecuritynews, Medium, dailydarkweb
(Media Disclaimer: This report is based on research conducted internally and externally using different ways. The information provided is for reference only, and users are responsible for relying on it. Infosecbulletin is not liable for the accuracy or consequences of using this information by any means).



