 InfoSecBulletin Cybersecurity for mankind

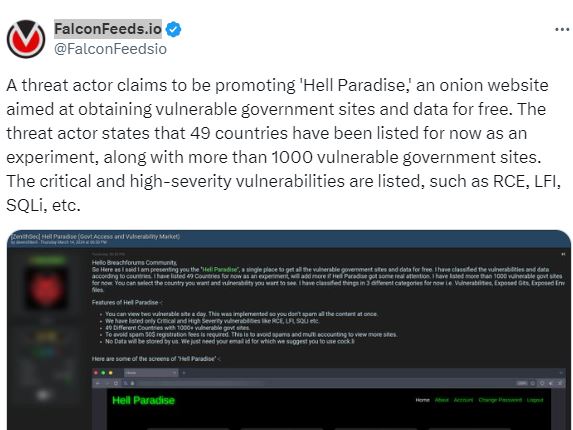
A cybercriminal has appeared on the dark web, announcing the creation of “Hell Paradise,” an undercover online platform supposedly made for taking advantage of weaknesses in government websites and getting access to important information. The cybercriminal mentions countries like the United Arab Emirates, Albania, Armenia, and Angola as some of their targets.
Daily Cyber security update for 25. 10. 2026

Daily Cyber security update for 24. 10. 2026

PHP shares new RCE flaw (CVE 2026-115560) with no patch but mitigation

US banks faced unauthorized access by AI agents in customer accounts: Axios reports

Atlassian patched 176 flaw in Jira and Confluence: Fortinet Urges to Patch Flaws Affecting FortiOS, FortiManager

Hacker claim to access Rajasthan Police data: 70,000 records allegedly exposed

Update now! PHP2Shell: Critical PHP vulnerabilities patched

Trump says data centres should pay dividends to local community

Hackers Actively Exploiting Palo Alto VPN Flaw Via CVE-2026-0257

DeepSeek AI banned by U.S. Government; federal agencies must remove all related tools

The hacker’s message to the Breachforums Community is a clear explanation of the “Hell Paradise” platform, which contains vulnerable government websites and related data categorized by country and vulnerability type.
The hacker claims to have found over 1000 vulnerable government websites from 49 countries. They are promoting “Hell Paradise” as a place to find and take advantage of these vulnerabilities.
Hackers classify vulnerabilities into three main categories: Vulnerabilities, Exposed Gits, and Exposed Env files. Of particular concern are critical and high-severity vulnerabilities such as Remote Code Execution (RCE), Local File Inclusion (LFI), and SQL injection (SQLi), which pose significant security risks if not fixed.
Access to “Hell Paradise” is not free. The hacker charges a $50 registration fee to prevent spam and abuse. This financial barrier helps the operator control access and reduce the risk of exploitation.
The hacker says that no data will be saved by the platform, only email addresses are needed for registration. However, the suggestion to use disposable email services like cock.li suggests that the operation is secretive and raises concerns about the real intentions of “Hell Paradise.”
“Hell Paradise” highlights the growing cyber threats to government infrastructures worldwide. Malicious actors are now more focused on attacking critical systems and stealing sensitive data. This poses a significant risk of widespread disruption and data compromise.
The cybersecurity community needs to collaborate and stay vigilant to face the increasing threat from cybercriminals and state-sponsored actors. We must take proactive measures and respond together to protect digital infrastructure and prevent the harmful effects of cyber exploitation.
Source: FalconFeeds, Cyberexpress
(Media disclaimer: This report is based on research from various sources and is for reference only. Users are responsible for how they use this information. InfoSecbulletin is not liable for the accuracy or consequences of using this information)



