Sunday , November 1 2026
LockBit
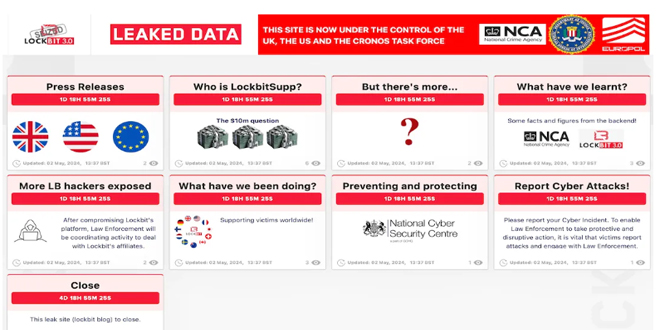
SCREENSHOT OF THE SEIZED DARKNET SITE OF THE LOCKBIT RANSOMWARE OPERATION ON MAY 5, 2024

LockBit’s seized darknet site resurrected by police, teasing new revelations

New information about the Lockbit ransomware gang might be coming soon. The gang’s old dark web leak site was taken down by law enforcement in February, but it has now reappeared, hinting at the release of new information in a few days.

Several parts of the site were updated on May 2, all promising more information to be dropped on May 7, including an answer to the “$10m question – who is LockbitSupp”. LockbutSupp is the gang’s apparent leader, and the law enforcement agencies involved in the site takedown have already suggested the individual is based in Russia, and had “engaged with law enforcement”.

Apple Warns 99 Countries iPhone Users of Mercenary Spyware Attacks

Apple has sent new threat warnings to some iPhone users in 99 countries. They said these users may be targeted...
Read More
Apple Warns 99 Countries iPhone Users of Mercenary Spyware Attacks

Daily Cyber security update for 31.10. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 31.10. 2026

NetamLoader malware to attack Win10: Customized for Gov.t in Asia
A new malware framework named NetamLoader is attacking a special version of Windows 10 used only by government agencies in...
Read More
NetamLoader malware to attack Win10: Customized for Gov.t in Asia

‘SMS of Death’ Zero-Click Flaw Disrupting Android Phones With a Single Text
A security expert shared information about a zero-click Android bug known as “SMS of Death.” Just one bad text message...
Read More
‘SMS of Death’ Zero-Click Flaw Disrupting Android Phones With a Single Text

NIST Unveiled Guidance for Post-Quantum Cryptography Transition
The National Institute of Standards and Technology (NIST) has shared advice on switching to post-quantum cryptography. This helps federal agencies...
Read More
NIST Unveiled Guidance for Post-Quantum Cryptography Transition

Daily Cyber security update for 29.10. 2026
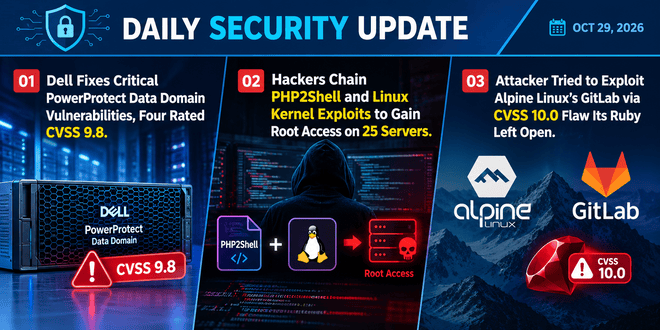
Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 29.10. 2026

Rapid7 Unveils 17 Zimbra Collaboration Suite Flaws Breaking Identity Boundaries
Rapid7 researchers found 17 security flaws in Zimbra Collaboration Suite (ZCS) that mess up authentication, mailbox isolation, and host privileges....
Read More
Rapid7 Unveils 17 Zimbra Collaboration Suite Flaws Breaking Identity Boundaries

CISA launched two free tools Identify Security Misconfig in Microsoft 365 and Google Workspace
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) provides two free tools to help organizations spot security flaws in Microsoft...
Read More
CISA launched two free tools Identify Security Misconfig in Microsoft 365 and Google Workspace

Apple iOS 27.2 Released Fixes 163 Flaws, Including Critical WebKit RCE
Apple launched iOS 27.2 and iPadOS 27.2 on October 26, 2026, fixing 163 security flaws. The update is for iPhone...
Read More
Apple iOS 27.2 Released Fixes 163 Flaws, Including Critical WebKit RCE

CISA adds PHP2Shell to KEV, PHP Releases New Security Updates to Fix Critical HTTP2Shell flaw
CISA has updated a new alert to reflect the addition of CVE-2026-109618 and CVE-2026-109619 to its Known Exploited Vulnerabilities (KEV)...
Read More
CISA adds PHP2Shell to KEV, PHP Releases New Security Updates to Fix Critical HTTP2Shell flaw

NCA will reveal information about Lockbit’s partners and share details from the gang’s backend systems soon. The seized site reveals more LB hackers.

“What have we learnt?” says another. “Some facts and figures from the backend.” And, again a date of May 7 is given for when these details will be shared.

Prior to that In February, the U.K. National Crime Agency (NCA) confirmed that it got LockBit’s source code and gathered intelligence about its activities and affiliates as part of Operation Cronos.

“Some of the data on LockBit’s systems belonged to victims who had paid a ransom to the threat actors, evidencing that even when a ransom is paid, it does not guarantee that data will be deleted, despite what the criminals have promised,” the agency said that time.
Check Also

two free tools

CISA launched two free tools Identify Security Misconfig in Microsoft 365 and Google Workspace

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) provides two free tools to help organizations …