 InfoSecBulletin Cybersecurity for mankind
Google has announced Vanir, an open-source tool for detecting and fixing security vulnerabilities, publicly available for developers.
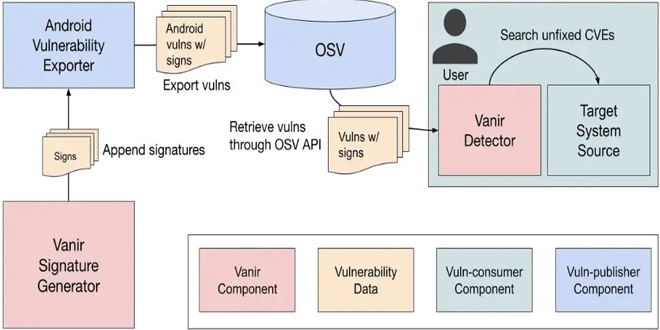
Vanir is a source code-based static analysis tool that automatically identifies the list of missing security patches in the target system. By default, Vanir pulls up-to-date CVEs from Open Source Vulnerabilities (OSV) together with their corresponding signatures so that users can transparently scan missing patches for an up-to-date list of CVEs.
Hacker claim to access Rajasthan Police data: 70,000 records allegedly exposed

Update now! PHP2Shell: Critical PHP vulnerabilities patched

Trump says data centres should pay dividends to local community

Hackers Actively Exploiting Palo Alto VPN Flaw Via CVE-2026-0257

DeepSeek AI banned by U.S. Government; federal agencies must remove all related tools

CISA, NSA and NIST Publish New 10 AI Agent Control Guidelines

Claude AI Cracks 25-Year NSA Cryptography Number Mystery in Just 30 Minutes

Bypassing firewalls, AI Agents Accessed Indian ‘ Data Without Permission: CERT-In

MITRE ATT&CK v20 Unveils 9 New Attack Techniques On AI Exploits, MFA Bypass, and CAPTCHA Evasion

Hackers Exploit Fortinet Flaws to Deploy Stealthy PEERSTITCH Malware on FortiGate Firewalls

Vanir, originally designed for Android, provides an effective way to manage security patches for various devices and software versions. As Google’s blog states, “This strengthens the security of the Android ecosystem, helping to keep Android users around the world safe.”
What sets Vanir apart?
Source-Code-Based Static Analysis: Instead of using potentially inaccurate metadata, Vanir examines the source code directly, offering a more precise and thorough analysis.
Automated Patch Identification: Vanir automates the time-consuming task of finding missing patches, saving both time and resources.
Versatility: Although made for Android, Vanir can easily be used in other systems, making it a valuable asset across the software development landscape.
“A main focus of Vanir is to automate the time consuming and costly process of identifying missing security patches in the open source software ecosystem,” Google emphasizes in their blog.
Early Success and Future Potential:
Early use of Vanir has shown great results. Google states that one engineer generated signatures for over 150 vulnerabilities and verified missing security patches in just five days using Vanir.
Vanir’s open-source nature encourages teamwork and innovation in security. “By open-sourcing Vanir, we aim to empower the broader security community to contribute to and benefit from this tool, enabling wider adoption and ultimately improving security across various ecosystems,” says Google.



