 InfoSecBulletin Cybersecurity for mankind
The spokesperson from Deloitte told two international media that, “No Deloitte systems have been impacted,”. The allegations relate to a single client’s system which sits outside the Deloitte network, according to cybersecurity news and infosecuritynews.
Times of India said, “Only a single client’s sensitive was impacted and none of the company’s systems were compromised”.
PHP shares new RCE flaw (CVE 2026-115560) with no patch but mitigation

US banks faced unauthorized access by AI agents in customer accounts: Axios reports

Atlassian patched 176 flaw in Jira and Confluence: Fortinet Urges to Patch Flaws Affecting FortiOS, FortiManager

Hacker claim to access Rajasthan Police data: 70,000 records allegedly exposed

Update now! PHP2Shell: Critical PHP vulnerabilities patched

Trump says data centres should pay dividends to local community

Hackers Actively Exploiting Palo Alto VPN Flaw Via CVE-2026-0257

DeepSeek AI banned by U.S. Government; federal agencies must remove all related tools

CISA, NSA and NIST Publish New 10 AI Agent Control Guidelines

Claude AI Cracks 25-Year NSA Cryptography Number Mystery in Just 30 Minutes

According to computing.co.uk, “the gang’s claims are false and relate to a client’s system, not its own”.
The ransomware group Brain Cipher has claimed to have hacked Deloitte UK and threatened to release 1tb of stolen data earlier this week.
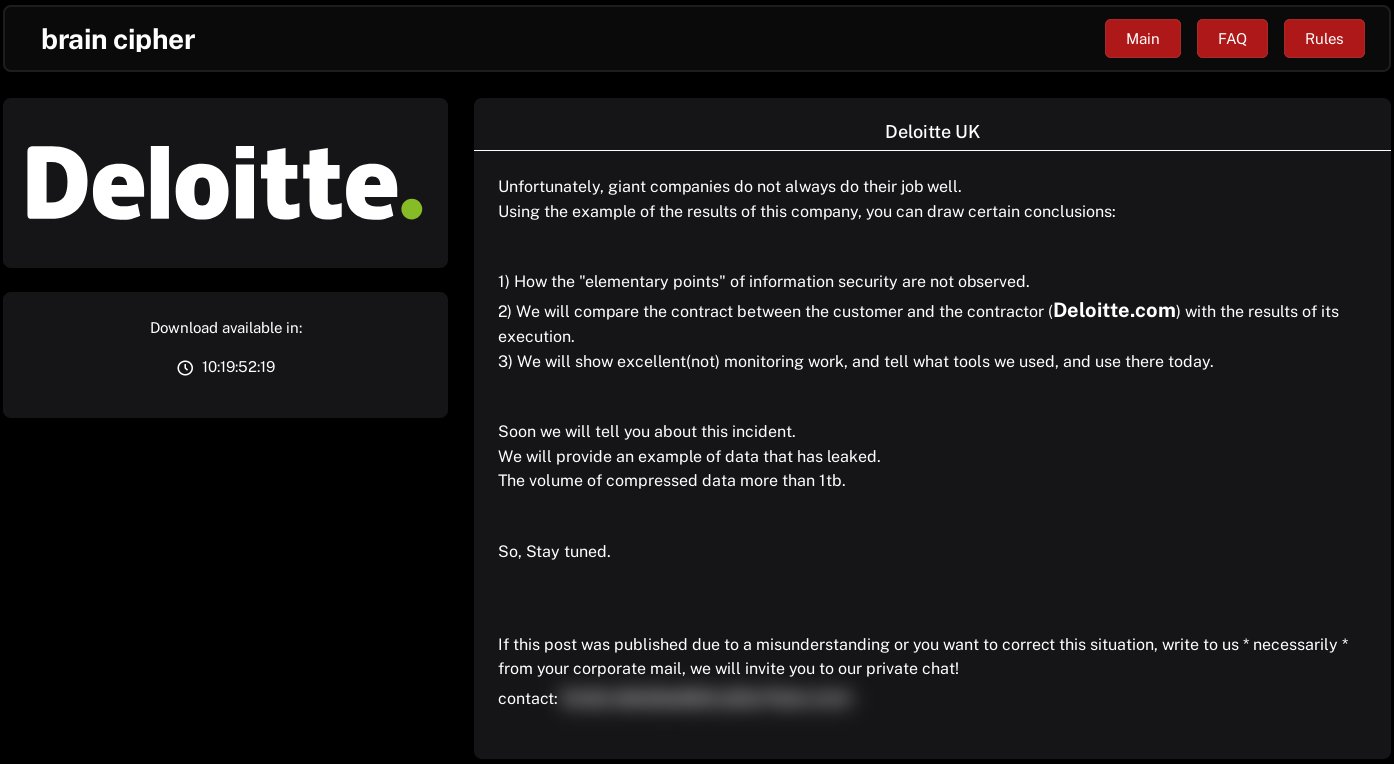
Hackers post read,
“Soon we will tell you about this incident.
“We will provide an example of data that has leaked.
“The volume of compressed data [is] more than 1tb.”
Brain cipher Group said, “We will show excellent (not) monitoring work, and tell what tools we used, and use there today.”
According to WatchGuard, the group uses a slightly modified version of the LockBit 3.0 builder for its encryption tool.
“Not affecting the target organization’s systems doesn’t mean there’s no impact,” Javvad Malik, lead security awareness advocate at KnowBe4, told Infosecurity. “The mere suggestion of a breach can harm reputations, affect stock prices, or trigger costly and unnecessary responses. Thus, even an empty threat carries the same weight as shouting ‘fire’ in a crowded theatre.”
Deloitte’s Response:
Deloitte UK has not confirmed or denied the breach publicly, and cybersecurity experts are monitoring the situation for updates.
Deloitte experienced another cyber incident recently, IntelBroker to claim to have leaked internal communications.
IntelBroker, the leader of the CyberN—–s ransomware gang, claims to have obtained email addresses, internal communications, and other internal company settings.
Deloitte accidentally exposed an Apache Solr server to the internet, leading to the breach, reported cyberdaily.au.
The group uses various extortion tactics to pressure victims and operates a TOR-based site to publish breaches and stolen data.
Brain Cipher ransomware attacks various critical sectors like healthcare, education, and manufacturing, as well as government and law enforcement. A notable incident was the attack on Indonesia’s National Data Center, which disrupted public services including immigration and student registration.
(Media Disclaimer: This report is based on research conducted internally and externally using different ways. The information provided is for reference only, and users are responsible for relying on it. Infosecbulletin is not liable for the accuracy or consequences of using this information by any means)



