 InfoSecBulletin Cybersecurity for mankind

A harmful Android app has been found that pretends to be real Indian banking apps to steal credentials, spy on users, and carry out unauthorized transactions. It uses Firebase for command-and-control operations to deploy phishing pages that look like real banking interfaces, deceiving users into sharing sensitive information.
Static analysis of the dropper reveals permissions such as ACCESS_NETWORK_STATE for monitoring connectivity to facilitate stealthy data exfiltration, REQUEST_INSTALL_PACKAGES for prompting installations of secondary APKs without user awareness, and QUERY_ALL_PACKAGES for profiling installed apps to target banking software specifically.
North Korean hackers steal more than $400 million using video images, FBI says

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

89 New ransomware groups emerge in 2026, claiming over 2,200 victims

Daily Cyber security update for 08.11. 2026

Japan banking crisis
Outage causes disruption at 128 japan banks: preventing ATM transaction

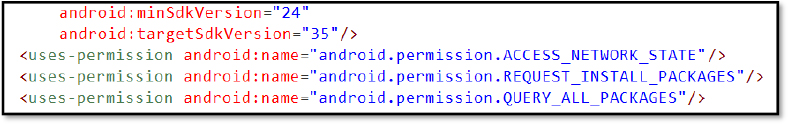
Permissions of a Dropper
The dropper secretly downloads a hidden file, saves it to external storage, and starts installation without regular app store checks, similar to methods used by advanced banking Trojans.
Delving deeper, the main payload requests permissions like READ_SMS, SEND_SMS, and RECEIVE_SMS to intercept and exfiltrate one-time passwords (OTPs) and two-factor authentication (2FA) codes, while REQUEST_IGNORE_BATTERY_OPTIMIZATIONS ensures uninterrupted background execution.
Permissions like READ_PHONE_STATE and READ_PHONE_NUMBERS allow device fingerprinting and SIM data extraction, including carrier names and phone numbers. They can also enable call forwarding abuse through USSD codes such as **21*number# to redirect calls to numbers controlled by attackers.
The payload disguises itself in the app launcher as INFO, operates silently without an icon, and uses modules like Account for credential theft, Debit for card data theft (validating CVV as 3 digits, card numbers as 19 characters, and ATM PINs as 4 digits), and AutostartHelper for persistence at boot using RECEIVE_BOOT_COMPLETED.
Data exfiltration happens via Firebase Realtime Database, which stores user IDs and intercepted SMS metadata, including sender, content, timestamp, and SIM slot in paths like user/<userID>. Local SharedPreferences also keep key-value pairs for offline storage.
Dynamic analysis shows the dropper initiating with fake update popups to lure users into enabling ‘Install Unknown Apps,’ followed by the payload requesting SMS access and displaying phishing pages that enforce input validation (e.g., 10-digit phone numbers and 4-digit MPINs) to appear legitimate.
Firebase Cloud Messaging (FCM) allows remote command execution, including unauthorized access and real-time SMS tracking, using embedded keys for sender ID, API, and storage buckets for covert control.
During the probe, the Firebase instance remained active but authentication-locked, underscoring its ongoing malicious use.

The malware seen since April 3, 2025, shows trends in mobile financial fraud. Cybercriminals replicate app icons and interfaces to trick users into giving risky permissions, allowing them to steal OTPs and bypass 2FA. Full report here.
CIRT alerts CII, Energy Sectors, Banks risk for a large-scale cyberattack



