 InfoSecBulletin Cybersecurity for mankind

BGD e-GOV CIRT alert for a potential risk of cyber attack on Thursday (24.07.2025). In its situational alert, CIRT said, based on current threat intelligence, there is a potential risk of a large-scale cyberattack targeting Bangladesh’s ICT infrastructure in the coming days.
CIRT mentioned that the cyber attack focuses on Critical Information Infrastructures (CII) and high-impact sectors such as banking, power, and public services.
Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

89 New ransomware groups emerge in 2026, claiming over 2,200 victims

Daily Cyber security update for 08.11. 2026

Japan banking crisis
Outage causes disruption at 128 japan banks: preventing ATM transaction

Daily Cyber security update for 06.11. 2026

Cyber attack causes French bank Credit Mutuel Arkea €100 million missing

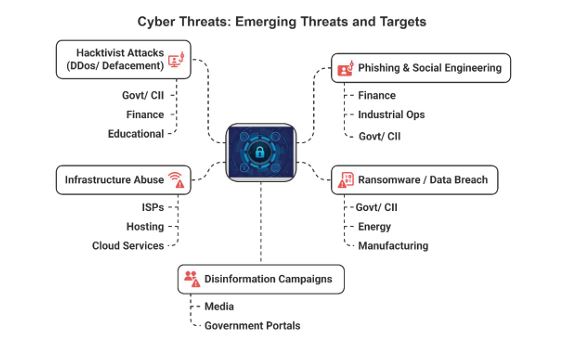
Recent attack trends show a focus on web application exploitation, website defacement, compromised credentials, and DDoS attacks.
CIRT advised organizations should improve 24/7 IT infrastructure monitoring, ensure proper logging, and maintain heightened security to quickly detect and respond to suspicious activities.
CIRT suggests implementing MFA for critical systems and restricting remote access immediately. It also emphasizes to:
Implement multi-factor authentication (MFA) for all critical systems.
Immediately review and restrict remote access, VPNs, and privileged accounts.
Urgently apply latest security patches to internet-facing services, servers, firewalls.
Review and patch vulnerabilities in web applications and exposed services.
Disable unused ports and services; enforce least-privilege access.
Utilize effectively SIEM/NIDS to detect abnormal behavior (e.g., lateral movement, DDoS, data
exfiltration).
Monitor for suspicious logins, unauthorized file changes, and external connections.
Use EDR or AV with updated threat signatures for detect threat.
Ensure critical data backups are regular, encrypted, and stored offline.
Review and update cyber incident response plans.



