Friday , November 13 2026
phone

ESET RESEARCH
“eXotic” spyware espionage campaign targets India and Pakistan

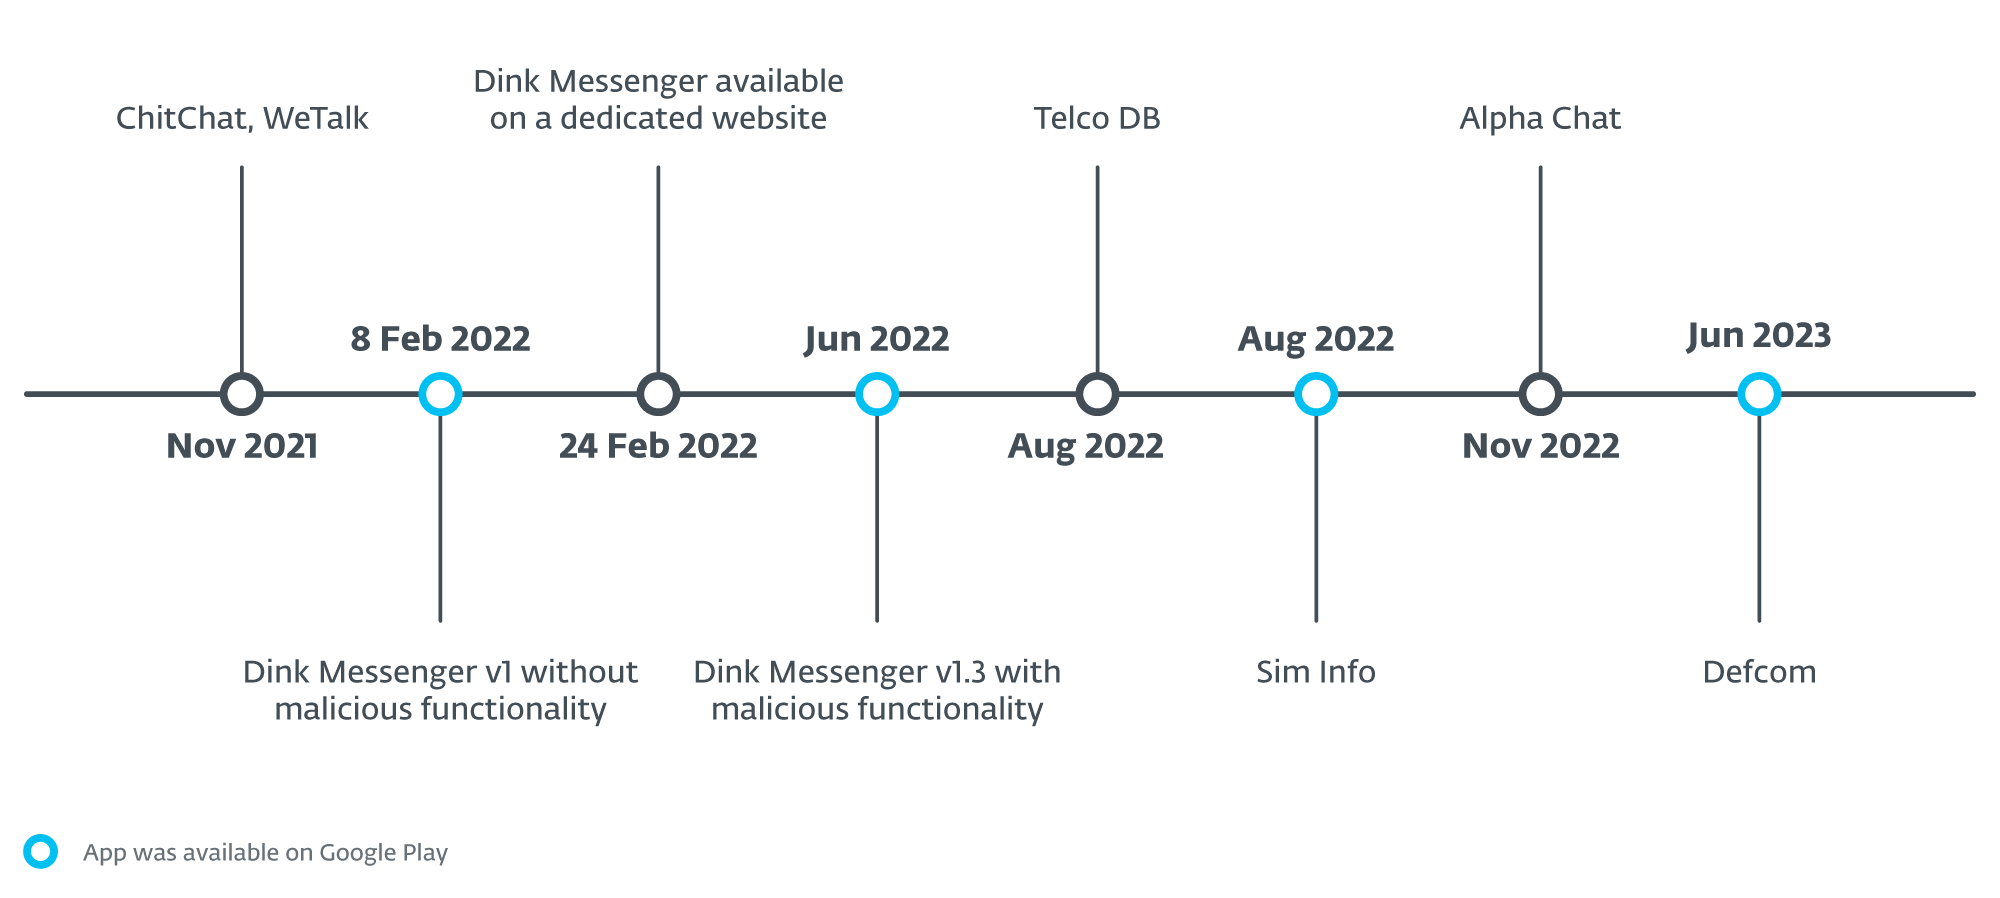
ESET researchers found a spying campaign targeting Android users. The campaign uses fake messaging apps that include XploitSPY malware. The campaign, called eXotic Visit, has been active from November 2021 to the end of 2023.

Malicious Android apps were distributed through targeted campaigns using dedicated websites and the Google Play store. These apps had a low number of installs on Google Play and have since been removed.

North Korean hackers steal more than $400 million using video images, FBI says

The United States Justice Department said Thursday it had seized cloud infrastructure used by North Korean hackers in a video-call...
Read More
North Korean hackers steal more than $400 million using video images, FBI says

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Microsoft has shared its updates for November 2026. These updates fix 1,093 new flaws in Windows, Office, SQL Server, SharePoint,...
Read More
Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Barracuda has confirmed active exploitation of security flaws affecting its Email Security Gateway (ESG), warning that attackers could combine two...
Read More
Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Apple, SAP, and Ivanti have published security updates that fix several flaws with messaging, Bluetooth, enterprise servers, and endpoint management...
Read More
Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

A jailbroken AI has been attacking a European telecom company and 13 companies using its data center and cloud for...
Read More
Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

IBM patched 208 security flaws in its API Connect platform. The CVE records released out on November 7, 2026. Among...
Read More
IBM fixes 208 API Connect vulnerabilities, 47 critical

89 New ransomware groups emerge in 2026, claiming over 2,200 victims

New ransomware actions in 2026 show more variety in cybercrime, with some groups claimed over 100 victims. The ransomware attack...
Read More
89 New ransomware groups emerge in 2026, claiming over 2,200 victims

Daily Cyber security update for 08.11. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 08.11. 2026

Japan banking crisis
Outage causes disruption at 128 japan banks: preventing ATM transaction

A major system failure has brought customer-facing banking services to a standstill at 128 shinkin banks across western Japan, leaving...
Read More
Japan banking crisis  Outage causes disruption at 128 japan banks: preventing ATM transaction
     Source: ESET

The eXotic Visit campaign seems to focus on specific Android users in Pakistan and India. It is not known which group is behind this campaign, but we are monitoring the threat actors and calling them Virtual Invaders.

Apps with XploitSPY can get contact lists, files, GPS location, and file names from specific directories related to the camera, downloads, Telegram, and WhatsApp. Certain filenames can be further extracted from these directories by a command from the control server. The chat function in XploitSPY is unique and believed to be developed by the Virtual Invaders group.

     Source: ESET

The malware uses a native library commonly used in Android app development to hide important information, such as C&C server addresses. This makes it difficult for security tools to analyze the app.

The apps mentioned below were removed from Google Play after ESET, as a Google App Defense Alliance partner, discovered that they contained harmful code. The low number of installations suggests that they were used in a targeted manner. The “eXotic Visit” apps were identified as part of this campaign, and the Technical analysis section examines the XploitSPY code present in these apps. Click here to read out the full report.


Check Also

SAP

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Apple, SAP, and Ivanti have published security updates that fix several flaws with messaging, Bluetooth, …