 InfoSecBulletin Cybersecurity for mankind
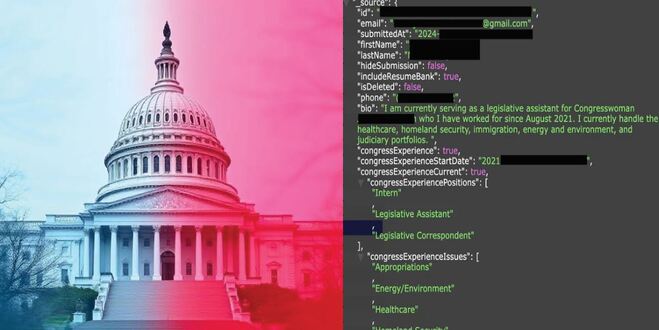
Thousands of Americans’ personal job-seeking details were publicly exposed because of an unsecured database linked to the House Democrats’ Official Online Resume Bank, DomeWatch.us.
The security lapse was brought to light by the research firm Safety Detectives, after an anonymous cybersecurity researcher reported to them about an “unencrypted and non-password-protected database,” containing over 7,000 records of applicants.
US banks faced unauthorized access by AI agents in customer accounts: Axios reports

Atlassian patched 176 flaw in Jira and Confluence: Fortinet Urges to Patch Flaws Affecting FortiOS, FortiManager

Hacker claim to access Rajasthan Police data: 70,000 records allegedly exposed

Update now! PHP2Shell: Critical PHP vulnerabilities patched

Trump says data centres should pay dividends to local community

Hackers Actively Exploiting Palo Alto VPN Flaw Via CVE-2026-0257

DeepSeek AI banned by U.S. Government; federal agencies must remove all related tools

CISA, NSA and NIST Publish New 10 AI Agent Control Guidelines

Claude AI Cracks 25-Year NSA Cryptography Number Mystery in Just 30 Minutes

Bypassing firewalls, AI Agents Accessed Indian ‘ Data Without Permission: CERT-In

The breach, revealed on October 27, 2025, showed a concerning amount of data on people applying for jobs, internships, or fellowships with Democratic Members’ offices and committees.
The leaked data contains Personally Identifiable Information (PII) such as names, phone numbers, email addresses, and security clearance details, raising the risk of fraud and targeted attacks. Additional investigation showed it also included applicants’ political party affiliation, home state, military service, and congressional experience.
The database included 469 people with “top secret” federal security clearance. Political analysis revealed that 6,300 individuals identified as Democrats, while only 17 were Republicans and 265 chose Independent or Other.
The exposed data included weblinks to Google forms and shared documents. Most records had timestamps from 2024–2025, which is confusing since the DomeWatch website says resumes are kept only for 90 days before archiving.
According to Safety Detective’s blog, the team notified the domain’s registration and technical contacts about data exposure, and access to the database was restricted the same day. The contacts responded simply, “Thanks for flagging.”
This exposure is a significant risk. Many of those affected have military or government backgrounds, making them potential targets for criminals using their information for impersonation or targeted phishing scams.
Discover more
Ethical hacking books
Network security audit
ransomware
Ransomware
Information security consulting
Ethical hacking tools
Privacy protection services
Artificial Intelligence
It’s important to check for job offers or messages if you think your personal information might be at risk.



