 InfoSecBulletin Cybersecurity for mankind
Trellix Advanced Research Center (ARC) found a campaign targeting a European embassy in New Delhi, India. Further investigation uncovered multiple targeted institutions across Sri Lanka, Pakistan, and Bangladesh.
PHP shares new RCE flaw (CVE 2026-115560) with no patch but mitigation

US banks faced unauthorized access by AI agents in customer accounts: Axios reports

Atlassian patched 176 flaw in Jira and Confluence: Fortinet Urges to Patch Flaws Affecting FortiOS, FortiManager

Hacker claim to access Rajasthan Police data: 70,000 records allegedly exposed

Update now! PHP2Shell: Critical PHP vulnerabilities patched

Trump says data centres should pay dividends to local community

Hackers Actively Exploiting Palo Alto VPN Flaw Via CVE-2026-0257

DeepSeek AI banned by U.S. Government; federal agencies must remove all related tools

CISA, NSA and NIST Publish New 10 AI Agent Control Guidelines

Claude AI Cracks 25-Year NSA Cryptography Number Mystery in Just 30 Minutes

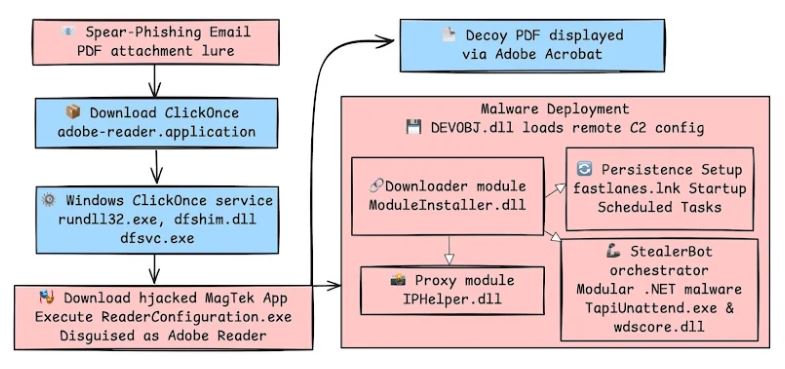
This report analyzes the tactics used by SideWinder, an APT group known for espionage in Asia. The investigation shows that SideWinder has evolved its methods, now using a new infection chain involving PDFs and ClickOnce, alongside their older Microsoft Word exploits. This change reflects their efforts to bypass standard security measures.
Email phishing lures and activity timeline:
The phishing campaign in 2025 had several waves, each targeting specific Asian diplomatic entities with unique themes. Its aim was to install ModuleInstaller and StealerBot malware for espionage.
The first round of emails occurred during March and April, targetingBangladeshi institutions with documents titled “Registration Form.pdf”, “Hajj training 2025.pdf”, or “Integrated Hajj Medical Team 2025.pdf”. To view the content of the files, the victim had to download the “latest Adobe Reader version” by clicking the button present in the document. The domains used to download the malicious Adobe Reader update included references to organizations and events from Bangladesh, such as the Cadet College, military high school, or the Hajj pilgrimage.
hajjtraining2025[.]moragovt[.]net
cadetcollege[.]adobeglobal[.]com
hajjmedicalteam[.]adobeglobal[.]com
The second wave of phishing emails targeted Pakistani diplomats from April to August 2025, using fake Adobe Reader updates and malicious Word documents.
pimec-paknavy[.]updates-installer[.]store
cabinet-gov-pk[.]dytt888[.]net
adobe[.]pdf-downlod[.]com
The third phase happened from June to September and involved phishing emails aimed at Sri Lankan authorities, using documents like “Annual Transfers of Officers in the Joint Services 2026.pdf” and “Promotion of officers in Grade I.pdf”. Both used the same method as phase one. Below is a list of domains for the next stages.
www-treasury-gov-lk[.]snagdrive[.]com
pubad-gov-lk[.]download-doc[.]net
“The multi-wave phishing campaigns demonstrate the group’s adaptability in crafting highly specific lures for various diplomatic targets, indicating a sophisticated understanding of geopolitical contexts,” Trellix said. “The consistent use of custom malware, such as ModuleInstaller and StealerBot, coupled with the clever exploitation of legitimate applications for side-loading, underscores SideWinder’s commitment to sophisticated evasion techniques and espionage objectives.”
CIRT Alert RCE Vulnerability in Microsoft WSUS in Bangladesh



