 InfoSecBulletin Cybersecurity for mankind
Fortinet customers must apply the latest updates, as almost 50,000 management interfaces remain vulnerable to the latest zero-day exploit.
The Shadowserver Foundation reports that 48,457 Fortinet devices remain publicly exposed and unpatched for CVE-2024-55591, despite urgent warnings in the last week.
Daily Cyber security update for 14.11. 2026

Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

PHP2Shell attack exploited a Check Point 0-day to deploy malware

North Korean hackers steal more than $400 million using video images, FBI says

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

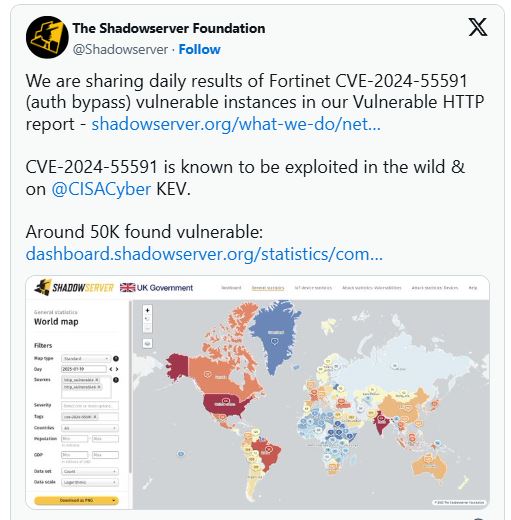
The situation hasn’t improved. Shadowserver started tracking exposed devices on January 16, two days after the zero-day CVE identifier was released, and found nearly 52,000 vulnerable instances.
Asia has the highest number of vulnerable firewalls accessible online, totaling 20,687, followed by North America with 12,866 and Europe with 7,401.
The register said, Last week Arctic Wolf Labs’ lead threat intelligence researcher Stefan Hostetler said exploits have been widespread, opportunistic, and date back to December.
He added that once they’ve pwned their target, attackers appear to be stealing credentials and using them to worm their way through the victim’s network with admin privileges. The rest of the details are still being gathered, but – needless to say – an intruder with admin access is not a welcome addition to the network.
“What we can say is that ransomware is not off the table,” Hostetler said, citing similar tactics used in the past by the likes of Akira and Fog.
Fortinet’s advisory provides details on upgrading to a safe version of FortiOS and FortiProxy or implementing a temporary workaround.
Recommended actions include:
Upgrade Firmware: Update to FortiOS 7.0.17 or newer and FortiProxy 7.2.13 or newer.
Restrict Access: Disable HTTP/HTTPS administrative interfaces or limit access to trusted IP addresses using local-in policies.
Monitor Networks: Review indicators of compromise (IoCs), such as unauthorized account creation or changes to firewall configurations.
Source: theregister, cybersecuritynews, the Shadowserver Foundation
OWASP Reveils Top 10 Smart Contract Vulnerabilities for 2025



