Saturday , November 14 2026
OWASP

OWASP Reveils Top 10 Smart Contract Vulnerabilities for 2025

OWASP has released its updated list of the top 10 vulnerabilities in smart contracts for 2025. This guide highlights the most critical vulnerabilities and provides developers and security professionals with a roadmap to reduce risks in decentralized systems.
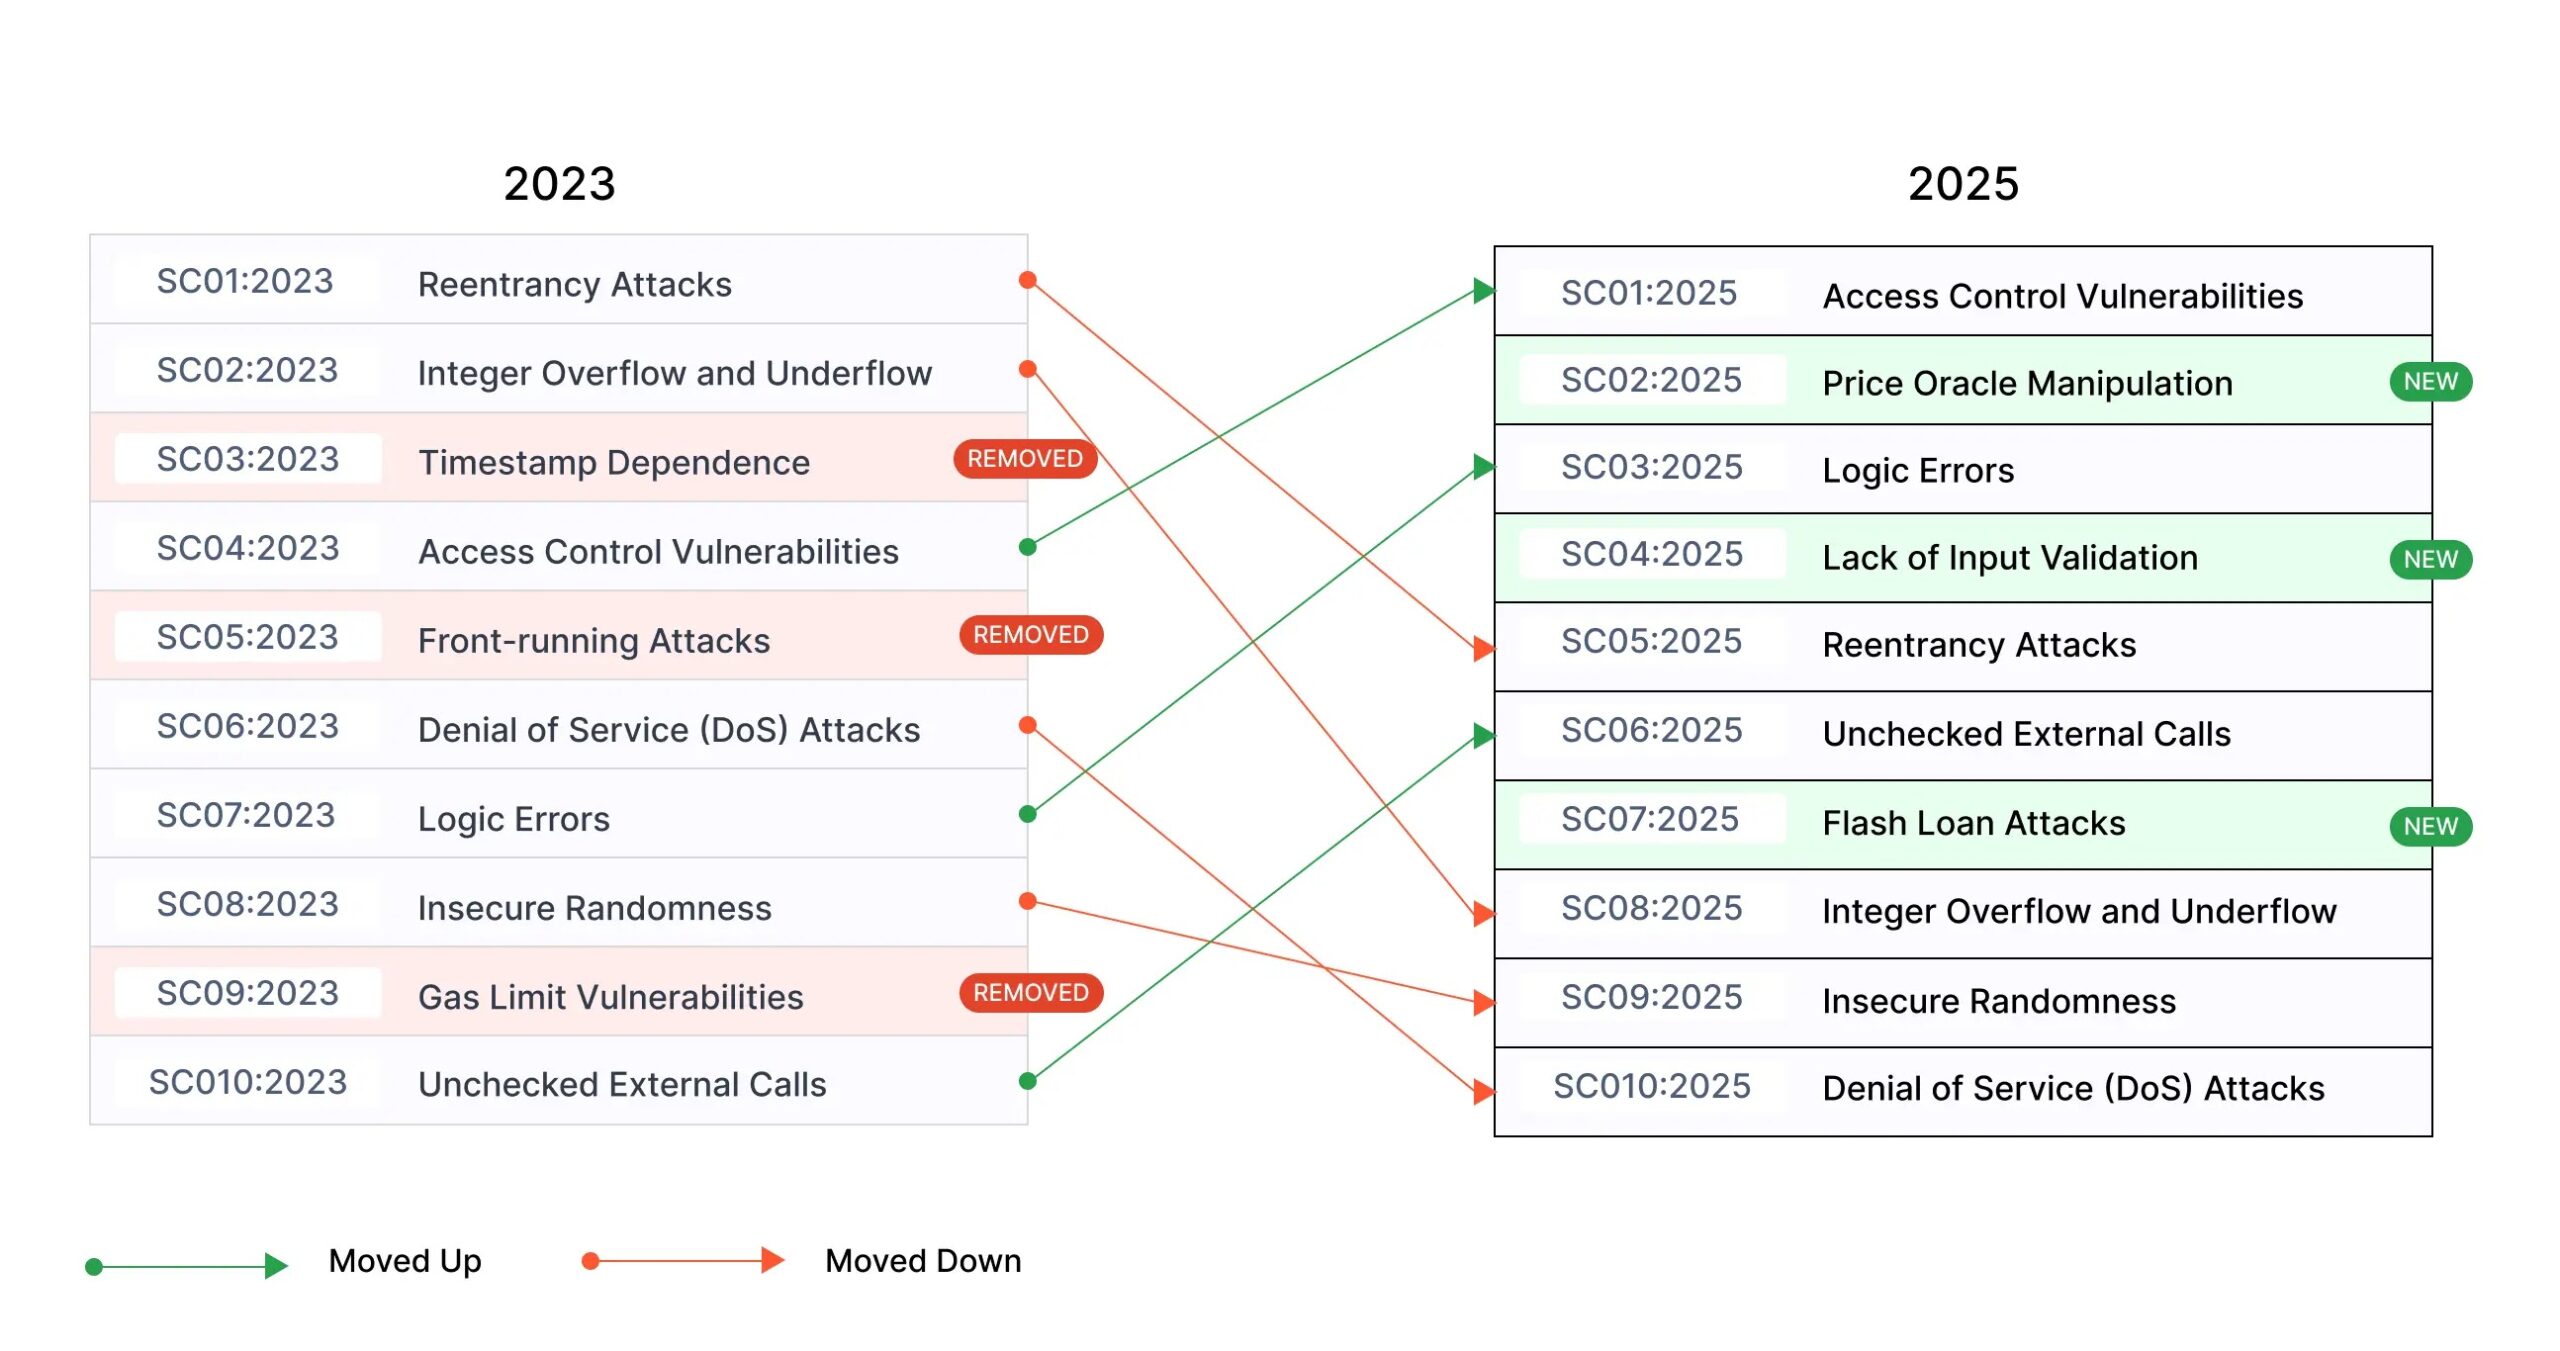
  OWASP 2023 – 2025

The OWASP Smart Contract Top 10 lists the most common vulnerabilities in the Web3 space, including:

Daily Cyber security update for 14.11. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 14.11. 2026

Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

The Latvian part of CSCTelecom,  a telecommunications provider, made a database with over 125 million SMS messages public. The leaked...
Read More
Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

PHP2Shell attack exploited a Check Point 0-day to deploy malware

Hackers used Check Point firewall flaws to get root access, insert backdoors, and install harmful malware on a VMware ESXi...
Read More
PHP2Shell attack exploited a Check Point 0-day to deploy malware

North Korean hackers steal more than $400 million using video images, FBI says

The United States Justice Department said Thursday it had seized cloud infrastructure used by North Korean hackers in a video-call...
Read More
North Korean hackers steal more than $400 million using video images, FBI says

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Microsoft has shared its updates for November 2026. These updates fix 1,093 new flaws in Windows, Office, SQL Server, SharePoint,...
Read More
Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Barracuda has confirmed active exploitation of security flaws affecting its Email Security Gateway (ESG), warning that attackers could combine two...
Read More
Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Apple, SAP, and Ivanti have published security updates that fix several flaws with messaging, Bluetooth, enterprise servers, and endpoint management...
Read More
Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

A jailbroken AI has been attacking a European telecom company and 13 companies using its data center and cloud for...
Read More
Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

IBM patched 208 security flaws in its API Connect platform. The CVE records released out on November 7, 2026. Among...
Read More
IBM fixes 208 API Connect vulnerabilities, 47 critical

Access Control Vulnerabilities (SC01:2025): Access control flaws can let unauthorized users modify a contract’s data or functions, resulting in major security breaches. In 2024, these issues caused losses of $953.2 million, as reported by SolidityScan’s Web3HackHub.

Price Oracle Manipulation (SC02:2025): Attackers exploit weak data feeds to manipulate external data sources, destabilizing protocols and creating financial chaos.

Logic Errors (SC03:2025): Mistakes in business logic remain a costly issue, leading to improper token minting, flawed lending logic, or incorrect reward distributions.

Reentrancy Attacks (SC05:2025): These attacks exploit a contract’s weak functions to drain funds or disrupt logic, leading to $35.7 million in losses in 2024.

Flash Loan Attacks (SC07:2025): These attacks exploit uncollateralized loans, disrupting liquidity and token prices. Key vulnerabilities include Integer Overflow and Underflow, Insecure Randomness, and Denial of Service Attacks.

Multiple Azure DevOps Vulns Allow To Inject CRLF Queries & Rebind DNS

Check Also

Cathedral

The Washington Post report
Ex-DOGE AI startup Cathedral Breaches Anthropic Internal Systems within 12 Hours

AI startup Cathedral gained a limited access to internal systems at Anthropic in less than …