InfoSecBulletin Cybersecurity for mankind
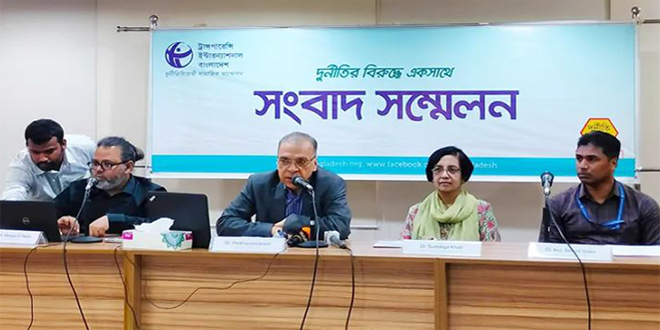
Transparency International Bangladesh (TIB) believes that the draft Data Protection Act, designed to protect information, will be as arbitrary as the Digital Security Act (DSA) if it is finally passed into law. The TIB released its observations on the draft Data Protection Act, 2023 at a press conference in the capital on Monday (April 17). TIB has identified various risks in monitoring the Act.
TIB says that if the law is implemented, the government will abuse its power to monitor individuals and strengthen its control over organizations working on human rights. The TIB’s observation says that while there is a demand for the formation of an independent commission outside the control of the government to monitor the issue of personal data protection, the discussed draft proposes the formation of a data protection agency, which will be appointed by the government.
US banks faced unauthorized access by AI agents in customer accounts: Axios reports

Atlassian patched 176 flaw in Jira and Confluence: Fortinet Urges to Patch Flaws Affecting FortiOS, FortiManager

Hacker claim to access Rajasthan Police data: 70,000 records allegedly exposed

Update now! PHP2Shell: Critical PHP vulnerabilities patched

Trump says data centres should pay dividends to local community

Hackers Actively Exploiting Palo Alto VPN Flaw Via CVE-2026-0257

DeepSeek AI banned by U.S. Government; federal agencies must remove all related tools

CISA, NSA and NIST Publish New 10 AI Agent Control Guidelines

Claude AI Cracks 25-Year NSA Cryptography Number Mystery in Just 30 Minutes

Bypassing firewalls, AI Agents Accessed Indian ‘ Data Without Permission: CERT-In

This agency is again empowered to access data, servers, prohibit data processing and order deletion of data of any controller/processor. And the fact of ensuring the proper application and execution of the Act has been left to a person appointed and necessarily controlled by the Government, with the provision that in initiating an inquiry ‘if it is reasonable to the Director-General.
Risk also states that where the government itself is the data (personal information) user and processor, it is not clear how another government agency can ensure that the government is complying with the law. It also said that such precedent of conflict of interest raises new fears that, like the Digital Security Act, this law will also be arbitrarily misused. The privacy of individuals’ information will be violated with the help of the government. If it goes against the government’s position, access to the server of any company, deletion of data and ban on data processing will happen.
As a result, the government’s power to monitor individuals, its abuses and control over organizations working on human rights will be strengthened. According to the observation, the discussed draft mentions three types of data, sensitive data; user generated data and classified data (classified data) which are subject to storage obligations within the country’s borders. It also talks about imposing restrictions on data transfer.
The risk this creates is that by keeping the data stored within the country’s borders, the power to monitor and make decisions on the data is effectively placed in the hands of the government. Given the enormous power of the Data Protection Agency under the direct control of the government and no effective safeguards against its abuse, the proposed draft will surely undermine people’s constitutional rights to freedom of speech and privacy. Monitoring of social media and people’s personal communication by various agencies of the government will be strengthened.
As data localization is expensive for small and mid-sized organizations, they will be left out of the competition. In addition, consumer spending will also increase as business expenses of all levels of organizations increase. The TIB report found that the country’s digital exports could drop by up to 45 percent depending on what kind of restrictions are imposed on data transfers. Growth rate may drop to 0.58 percent. Besides, there is fear of negative impact on foreign investment.
The draft states that, in case a company commits any offense under this Act, every owner, chief executive, director, manager, secretary, partner or any other officer or employee or representative of the company shall be deemed to have committed the said offence, unless he. Be able to prove that the offense was committed without his knowledge or that he tried his best to prevent the offence.
This section proposes a system in direct contrast to the principle of onus of proof in the criminal law. As a result, legal risk has been created for all organizations working on civil rights, media and all types of domestic and foreign organizations. And this risk is not limited to monetary penalties as the Criminal Procedure Code provides for enforcement. The experience of harassment of journalists and civil society under the Digital Security Act in Bangladesh does not guarantee that nothing will be done with the Data Protection Act.
Dr. Iftekharuzzaman, Executive Director of TIB, consultant-executive management, Sumaiya Khair, Outreach and Communication Director Sheikh Manzoor-e-Alam, Data Protection Expert Dr. Tariqul Islam were present at the press conference.