InfoSecBulletin Cybersecurity for mankind
The National Safety Council has leaked nearly 10,000 emails and passwords of their members, exposing 2000 companies, including governmental organizations and big corporations.
The National Safety Council (NSC) is a non-profit organization in the United States providing workplace and driving safety training. On its digital platform, NSC provides online resources for its nearly 55,000 members spread across different businesses, agencies, and educational institutions.
Daily Cyber security update for 14.11. 2026

Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

PHP2Shell attack exploited a Check Point 0-day to deploy malware

North Korean hackers steal more than $400 million using video images, FBI says

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

However, the organization’s website was left vulnerable to cyberattacks for five months. The Cybernews research team discovered public access to the web directories that exposed thousands of credentials.
Among a long list of leaked credentials were employees of around 2000 companies and governmental entities, including:
- Fossil fuel giants: Shell, BP, Exxon, Chevron
- Electronics manufacturers: Siemens, Intel, HP, Dell, Intel, IBM, AMD
- Aerospace companies: Boeing, Federal Aviation Administration (FAA)
- Pharmaceutical companies: Pfizer, Eli Lilly
- Car manufacturers: Ford, Toyota, Volkswagen, General Motors, Rolls Royce, Tesla
- Governmental entities: Department of Justice (DoJ), US Navy, FBI, Pentagon, NASA, The Occupational Safety and Health Administration (OSHA)
- Internet service providers: Verizon, Cingular, Vodafone, ATT, Sprint, Comcast
- Others: Amazon, Home Depot, Honeywell, Coca Cola, UPS
These companies likely held accounts on the platform to access training materials or participate in events organized by the NSC.
The vulnerability posed a risk not only to NSC systems but also to the companies using NSC services. Leaked credentials could have been used for credential stuffing attacks, which try to log into companies’ internet-connected tools such as VPN portals, HR management platforms, or corporate emails.
Also, the credentials could have been used to gain initial access into corporate networks to deploy ransomware, steal or sabotage internal documents, or gain access to user data. Cybernews reached out to the NSC, and it quickly fixed the issue.
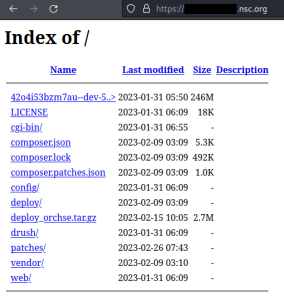
Public access to web directories
The discovery of the vulnerability was made on March 7th. The Cybernews research team found a subdomain of the NSC website, which was likely used for development purposes. It exposed the listing of its web directories to the public, enabling an attacker to access the majority of files crucial for the operation of the web server. Among the accessible files, researchers also discovered a backup of a database storing user emails and hashed passwords. The data was publicly accessible for 5 months, as the leak was first indexed by IoT search engines on January 31st, 2023.
In total, the backup stored around 9500 unique accounts and their credentials, with nearly 2000 different corporate email domains belonging to companies spreading across various industries.
Having a development environment accessible to the public shows poor development practices. Such environments should be hosted separately from the production environment’s domain and must refrain from hosting actual user data, and, of course, it should not be publicly accessible.
As a huge number of emails were leaked, platform users could potentially experience a surge in spam and phishing emails. It’s advisable for them to externally verify the information contained in emails and exercise caution when clicking links or opening attachments.
Crackable passwords
Exposed passwords were hashed using the SHA-512 algorithm, which is considered secure for password hashing. An additional level of security was also used – salts. However, the salts were stored together with password hashes and were only encoded using base64. This made it trivial for potential attackers to retrieve the plaintext version of the salt, subsequently easing the password cracking process.
It might take as long as 6 hours to crack a single password found in the database, depending on the password strength, and the list of previously leaked passwords or word combinations used by the attacker.
This doesn’t imply that every password within the found database could be cracked, yet it’s probable that a significant portion of them could be. Research indicates that it’s relatively commonplace to successfully crack approximately 80% of the hashes present in such data dumps.
For this reason, we recommend that users who had accounts on NSC change their passwords both on the nsc.org website and on any other accounts where they used the same password.
Source: cybernews