InfoSecBulletin Cybersecurity for mankind
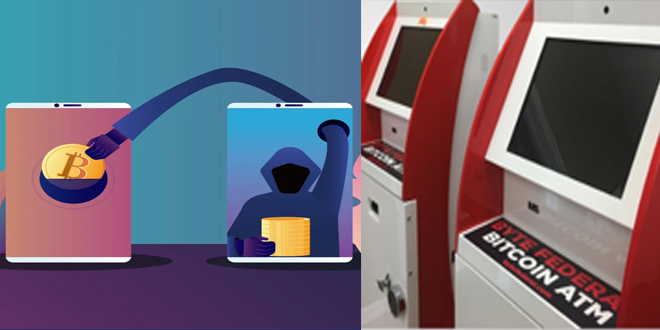
TechCrunch reports that Byte Federal, a major Bitcoin ATM operator in the U.S., has experienced a data breach affecting the personal information of thousands of customers.
A Florida-based company recently reported to the Maine attorney general that hackers tried to access data from about 58,000 customers. The breached information includes names, addresses, phone numbers, IDs, Social Security numbers, transaction details, and user photos.
Six 0-Days Discovered by Researchers Allow Unauthorized Access to Supermarket Fridge Systems

Daily Cyber security update for 14.11. 2026

Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

PHP2Shell attack exploited a Check Point 0-day to deploy malware

North Korean hackers steal more than $400 million using video images, FBI says

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

The breach happened on September 30 and was discovered by Byte Federal on November 18. An unknown attacker exploited a vulnerability in third-party software to access the company’s network. In a November blog post, Byte Federal revealed that the vulnerability was in the popular developer platform GitLab.
Byte Federal, which runs more than 1,200 Bitcoin ATMs in the U.S., has taken steps to secure its systems. They reset all customer accounts and changed internal passwords to prevent unauthorized access. This incident underscores the ongoing challenge of protecting sensitive customer data from cyber threats.
Byte Federal is actively working to safeguard user data and address concerns.
Byte Federal has established a helpline for affected customers and is providing support through their customer service team. They advise users to reset their login credentials and be alert for signs of fraud or identity theft.
The company advises users to regularly check their account statements and credit reports for any suspicious activity. They also offer guidance on how to place fraud alerts or security freezes with major credit reporting agencies.
“We take our responsibilities to protect your personal data very seriously,” Tarantino stated. “We are deeply troubled by this situation and are doing everything in our power to address it.”